Board reporting on human risk
Give the board a quarterly human-risk number with a trend, not a training completion percentage.
Five-to-ten-minute 3D exercises your people finish, with completion evidence your auditor can export.
- SEC
- Reg. S-K Item 106, annual disclosure
- Incidents
- Form 8-K Item 1.05, four business days
- Readers
- Board, audit committee, CEO
What goes on the board slide
- The score. Organization human risk score and its quarter-over-quarter trend.
- Reporting rate. How many people flag a phish, next to how many click.
- Hot spots. The three riskiest behaviours, by department.
- Follow-through. Remediation completed after each failure.
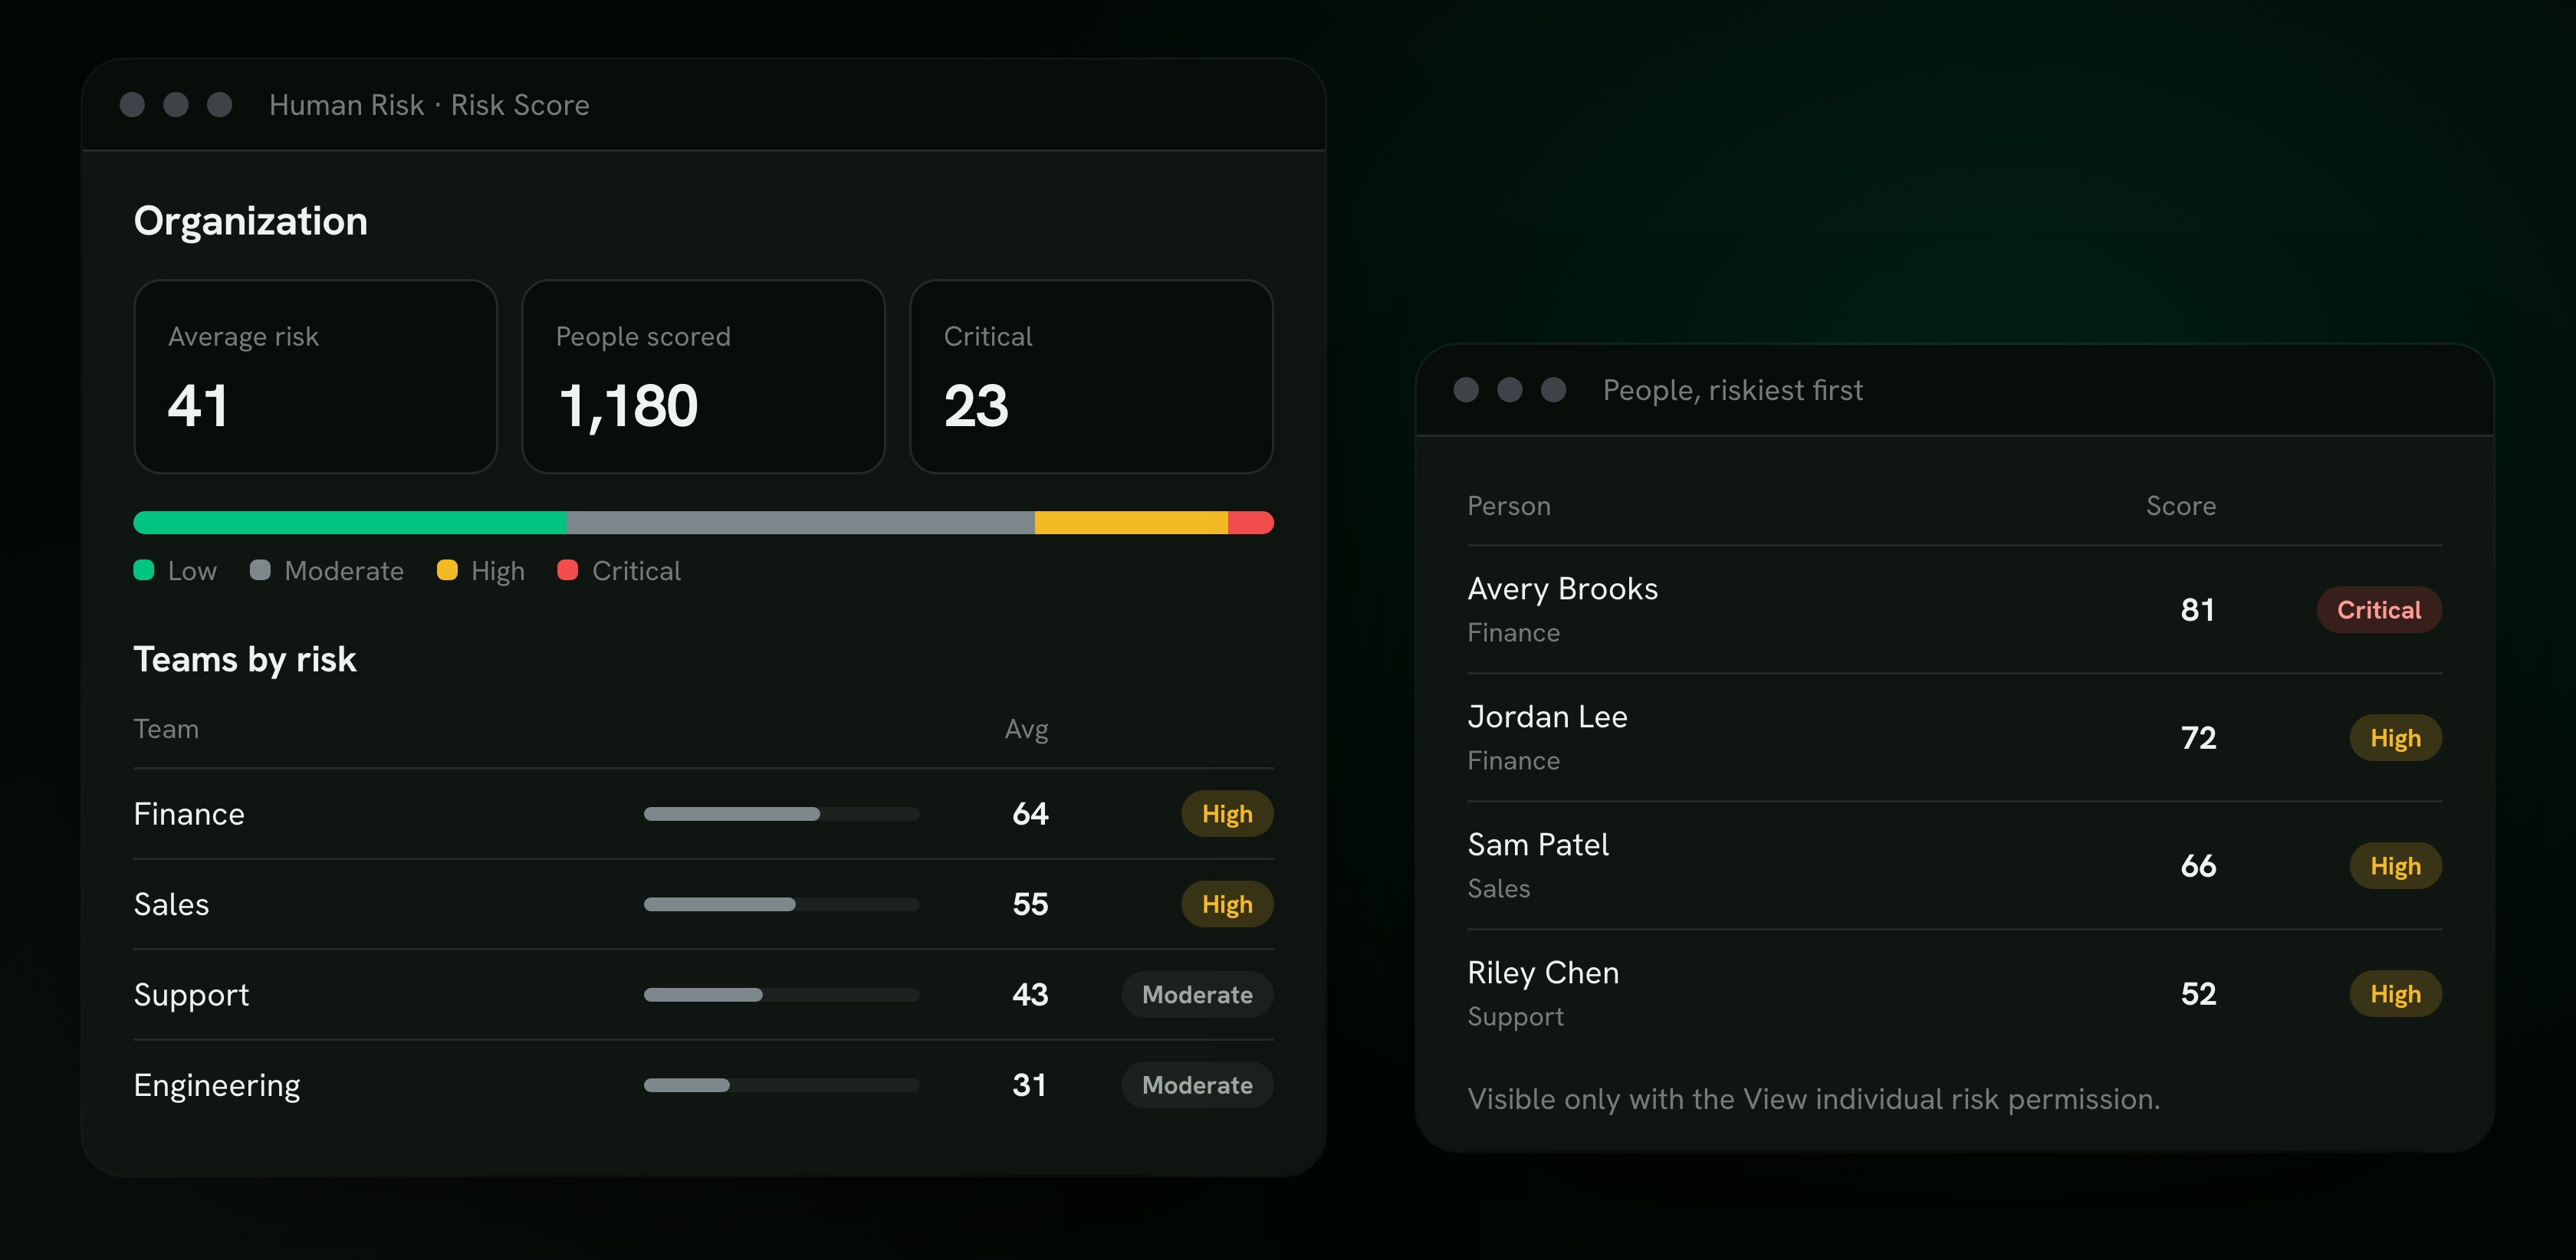
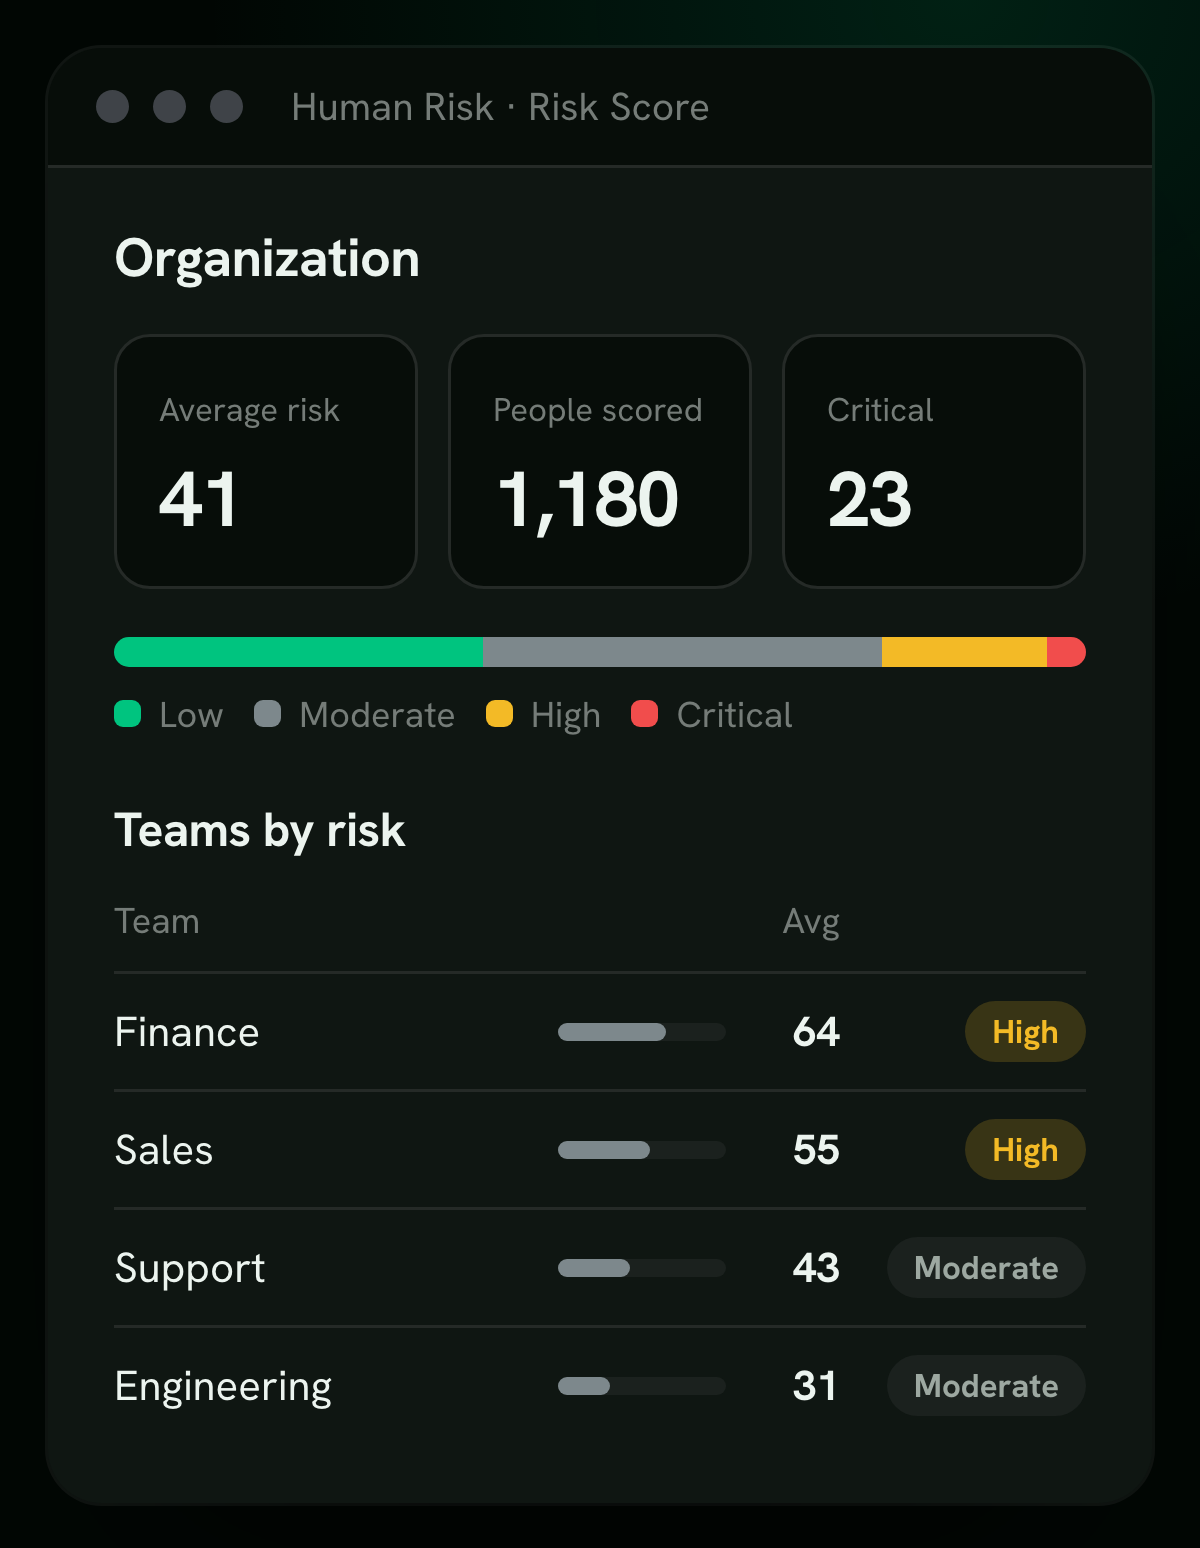
One number for the whole organization
Human risk by department, with the trend the board asks about.
Boards are now accountable for cyber
- 2023 SolarWinds The SEC charged the company and its CISO over cybersecurity disclosures; a court dismissed most claims in 2024. SEC, SDNY ruling
What you get
- Board-ready slide deck
- A four-slide quarterly template tuned for cyber-committee or audit-committee presentation.
- Quarter-over-quarter trend line
- Four quarters of click rate, report rate, completion rate, and scoring on a single chart.
- Industry benchmark comparison
- Peer-median comparison sourced from public benchmarks.
- SEC 10-K Item 106 alignment
- The narrative format aligns with Item 106 of Regulation S-K, including the management process and board-oversight language the filing requires.
- Audit-aligned source-of-truth
- The same data feeds the ISO 27001 audit, the SOC 2 audit, the cyber-insurance renewal, and the board report.
How it works
01 Pull quarter-over-quarter metrics
Four core measures: completion rate, scores across the catalogue, phishing click rate and phishing report rate.
Each shows the change from last quarter, a four-quarter trend and a split by group: employees, contractors, finance, IT and leadership.
02 Build the risk-reduction narrative
Turn the numbers into a risk story. A 40 percent drop in clicks and a threefold rise in reports means measurably less ransomware exposure.
Put a dollar figure on it using a defensible benchmark such as IBM's Cost of a Data Breach report.
03 Compare to industry benchmark
Pull the click and report benchmarks for your sector from the Verizon DBIR, IBM, Proofpoint, Egress or a sector report.
Show whether you sit above or below the peer median, and how your trend compares.
04 Drop into the board-ready slide template
Fill in four slides: program overview, quarter results with changes, benchmark comparison and next actions.
They fit a 15 to 20-minute committee slot, with detail in the appendix.
05 File with the risk register and cyber-insurance package
The same quarterly data goes into the enterprise risk register, the cyber-insurance renewal questionnaire and the 10-K Item 106 narrative.
One report instead of three separate exercises.
Go deeper
The full picture
Since the SEC adopted its cyber disclosure rules in 2023, board oversight of cybersecurity is a regulated topic. Item 106 of Regulation S-K asks registrants to describe the board's cyber expertise, how management handles risk, and any material incidents.
Cyber or audit committees now expect a quarterly briefing, and awareness training is one of the few program metrics directors can actually judge.
A completion percentage tells directors very little. It doesn't say whether staff are more or less likely to fall for the next phish or BEC email.
They want a risk-reduction story in dollars, a comparison with peers, and a trend line showing whether the program works.
So the quarterly report comes as a set: a slide template, a narrative tied to risk-reduction metrics, an industry benchmark, and a summary that maps to 10-K Item 106 and a standard cyber-committee charter. The same data feeds your risk register and the cyber-insurance renewal.
Related reading
Sources
- Cybersecurity Risk Management, Strategy, Governance, and Incident Disclosure (Final Rule, Item 106 of Regulation S-K) , U.S. Securities and Exchange Commission
- Director's Handbook on Cyber-Risk Oversight , National Association of Corporate Directors (NACD)
- Principles for Board Governance of Cyber Risk , World Economic Forum
- Directive (EU) 2022/2555 (NIS2) — Article 20: Governance (management body cybersecurity training and accountability) , EUR-Lex (Official Journal of the European Union)
- NIST Cybersecurity Framework 2.0 — Govern (GV) Function , National Institute of Standards and Technology (NIST)
- Reporting Cybersecurity Risk to the Board of Directors , ISACA
- 2024 Global Digital Trust Insights — Board Oversight of Cyber Risk , PwC
See it running in your workspace
We walk you through the threats, frameworks and exercises that matter for you, on your own data.