GDPR security awareness training
GDPR never says “annual training”. It puts training inside the DPO's tasks in Article 39 and the security measures of Article 32, then makes you prove both under Article 5(2).
Five-to-ten-minute 3D exercises mapped to each GDPR duty, with completion evidence your auditor can export.
At a glance
- Reach
- Article 3: anyone offering to, or monitoring, people in the EU
- Training duty
- Article 39(1)(b) DPO task; Article 32(4) staff act on instruction
- Fine ceiling
- €20M or 4% of worldwide turnover under Article 83(5)
- Breach clock
- 72 hours to the supervisory authority under Article 33
Trusted by teams at





Founded by the creator of Kontra Application Security Training.
Play the exercises behind your GDPR program
Each one is a 3D scenario your staff finish in 5 to 10 minutes. Pick one and play it here, with no sign-up.
Exercises run in interactive 3D environments.
Six articles that become a training plan
Each one changes who you train or what you have to be able to show.
- Art. 5(2) Accountability You must demonstrate compliance, so completion records are evidence.
- Art. 24 Controller responsibility Appropriate organisational measures, and training is one of them.
- Art. 32(4) Acting on instruction People with access to personal data process it only as instructed.
- Art. 33 72-hour breach notice Staff have to recognise a breach and escalate it fast.
- Art. 39(1)(b) DPO tasks Awareness-raising and training of staff involved in processing.
- Art. 88 Employee data Monitoring staff, phishing tests included, may need works-council agreement.
Fines that started with how staff handled personal data
Data protection authorities keep citing missing or outdated staff training.
H&M Hennes & Mauritz Online Shop EUR 35.3M (2020), Hamburg HmbBfDI
In October 2020 the Hamburg Commissioner for Data Protection and Freedom of Information fined H&M EUR 35,258,707.95. Managers at a Nuremberg service centre had kept detailed notes on employees’ private lives after return-to-work meetings, covering illnesses, family disputes, religious beliefs and holidays, and used them in employment decisions.
The authority named the lack of effective training, awareness and supervision when weighing responsibility under Article 83(2)(d).
H&M published a remediation plan with company-wide data protection training, a new whistleblower channel and signed commitments from leadership. Any HR-led training program in the EU should start from this case.
British Airways GBP 20M (2020), UK ICO
In July 2019 the ICO proposed a GBP 183.39 million fine against British Airways for the 2018 Magecart-style breach that exposed card and personal data of about 429,612 customers and staff. The final penalty notice in October 2020 set it at GBP 20 million.
The ICO listed weak monitoring, poor third-party risk management and low staff security awareness as contributing factors. It also credited the refreshed staff training program when reducing the fine.
So Article 83(2)(d) cut both ways: weak training helped cause the breach, and a credible fix lowered the penalty.
Uber Technologies EUR 290M (2024), Dutch Autoriteit Persoonsgegevens
On 26 August 2024 the Dutch authority fined Uber Technologies Inc and Uber BV EUR 290 million. Uber had sent European drivers’ data, including ID documents, taxi licences, location and payment details and in some cases criminal and medical data, to US servers without a valid transfer mechanism after Schrems II struck down the Privacy Shield.
The Autoriteit Persoonsgegevens cited Article 32 organisational measures and the controller’s responsibility under Article 24. It is the largest fine that authority has issued.
Use it when training engineering and operations on cross-border data flows.
GDPR articles, mapped to exercises
Articles a supervisory authority cites, next to scenarios on DSARs, consent and breach handling.
Art. 35 / 39 DPIA & DPO Awareness Training Art. 33-34 Breach Notification Art. 25 Privacy by Design Art. 15-22 Data Subject Rights Art. 28 Processor Obligations Art. 44-49 International Transfers Art. 5 Data Principles Art. 22 Automated Decision-Making & AI Profiling Art. 6-7 Lawful Basis & Consent Art. 9 Special Categories of Personal Data Five courses, starting with GDPR itself
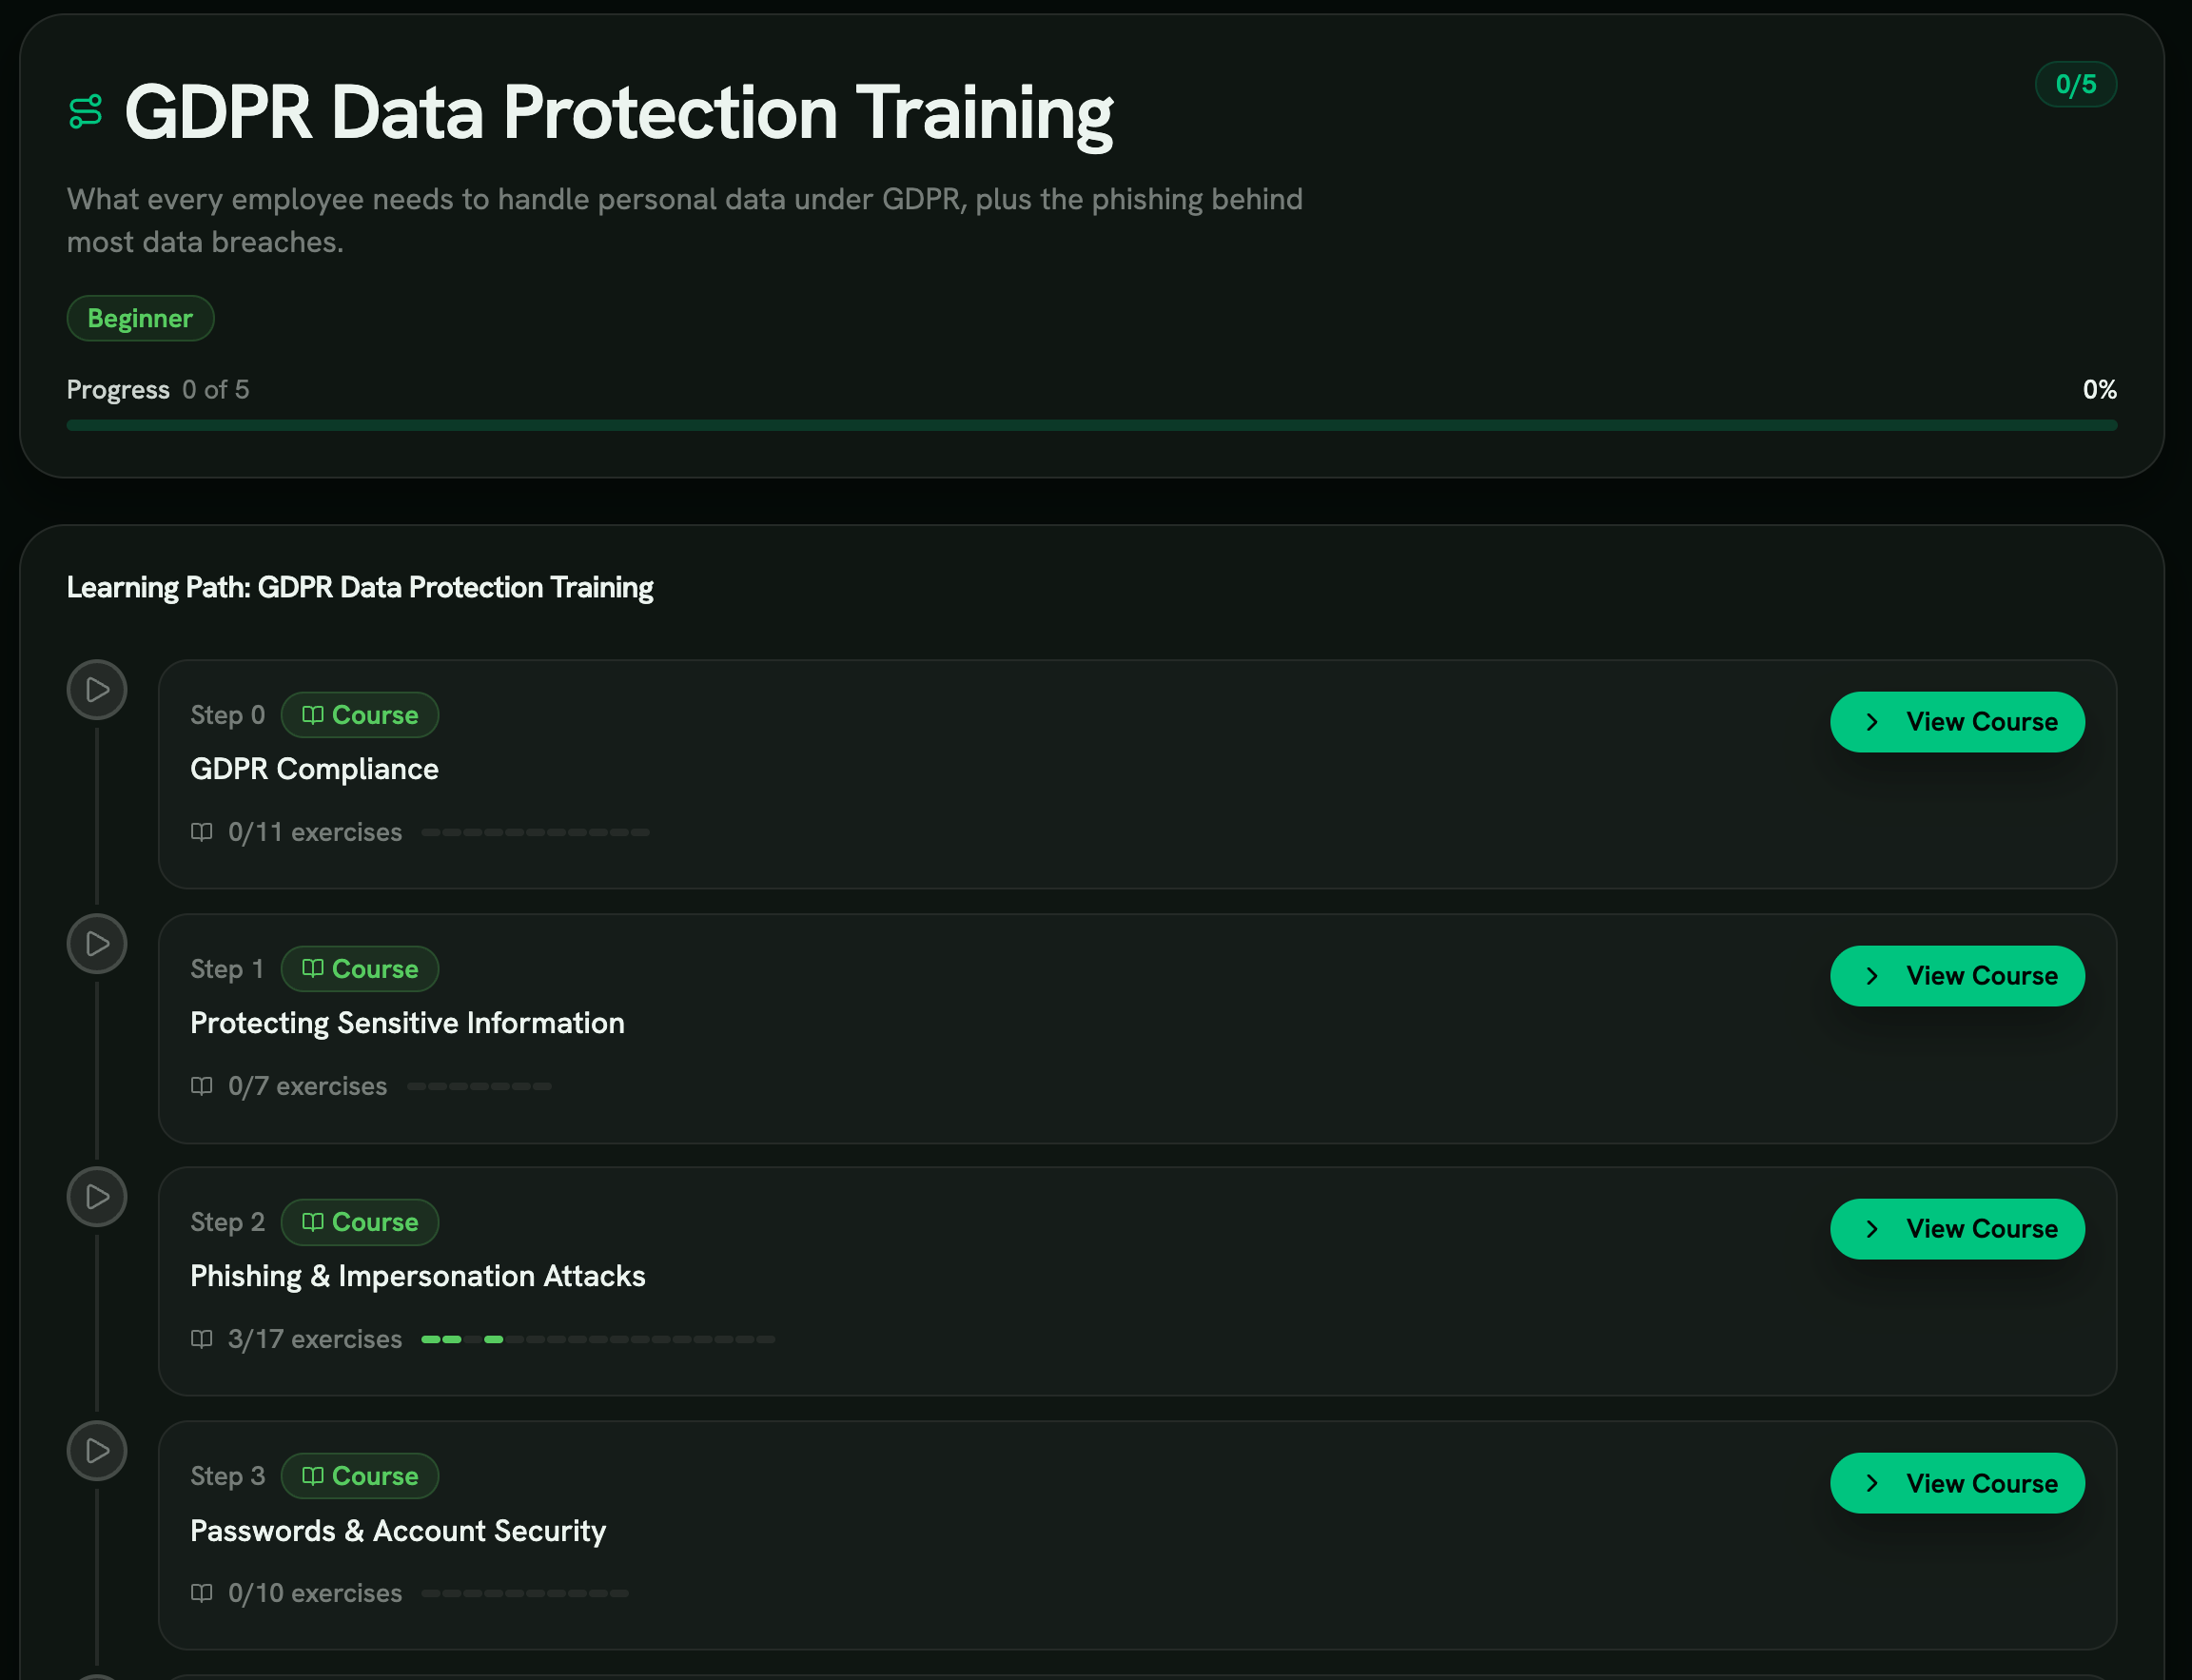
The GDPR path opens with an 11-exercise GDPR course, then adds the attacks that cause most personal data breaches.
- Lawful processing first
- Data subject rights, cross-border transfers and the 72-hour breach clock.
- Then the breach causes
- Phishing and account security, since most breaches start with stolen credentials.
- Short enough to finish
- Five steps, so Article 39 awareness duties are met without a week of training.
Where GDPR puts the duty to train
Where the duty to train actually comes from, article by article.
01 Scope: who is a controller, who is a processor, and who needs training
GDPR separates the controller, which decides why and how personal data is processed, from the processor, which processes it for a controller under a written Article 28 contract. Both have training duties.
Inside the organisation, anyone who touches personal data is in scope: marketing running campaigns on legitimate interest, sales in the CRM, HR with employee files, engineers designing schemas, support handling tickets, finance running payroll.
The DPO is not the only one who must know the rules. The DPO is the one responsible for making sure everyone else does.
02 Article 39 and Article 32: the two anchor articles
Article 39(1)(b) lists the DPO’s tasks, including monitoring compliance “including the assignment of responsibilities, awareness-raising and training of staff involved in processing operations, and the related audits”.
Article 32 requires technical and organisational measures that fit the risk. EDPB Guidelines 04/2019 and the Article 29 Working Party guidance on DPOs both count staff training as one of those measures.
Skip either article and the program fails before the auditor opens the spreadsheet.
03 Role-based assignment by data-touching role
One annual module for everyone does not survive an enforcement case. Each team touches personal data differently, so each gets its own scenarios:
- DPO: the full regulation.
- Marketing: consent, legitimate interest, and the e-Privacy rules for cookies and email.
- Sales: lawful basis, transfers, and buying contact lists.
- HR: Article 9 special category data, employee monitoring, and the limits the H&M decision drew.
- Engineering: Article 25 privacy by design, data minimisation, production data in test, and Article 22 automated decisions.
- Customer support: spotting a DSAR, the 72-hour breach clock, and checking who is really asking.
Each team is scored on the decisions its own job involves.
04 Documented evidence: training records, signed acknowledgments, content versioning
When a supervisory authority asks for Article 32 evidence, an attendance sheet screenshot will not do.
Expect to show:
- timestamped training records per employee
- signed acknowledgments
- a version history of the content as the law and guidance changed
- a refresh log tied to events: Schrems II in 2020, the new SCCs in 2021, the EU US Data Privacy Framework in 2023 and the EU AI Act in 2024
EDPB Guidelines 09/2022 on breach notification say the same thing: the controller must be able to show what staff knew, and when.
05 Refresh cadence and new-hire onboarding
GDPR sets no frequency. Supervisory authorities treat once a year as the minimum and quarterly to monthly as normal for high-risk roles.
New hires who handle personal data should finish role training before they get production access, not within 30 days of starting.
France’s CNIL, Germany’s BfDI and the UK’s ICO have all published guidance making the same point. Training is a continuous control, and its pace should match the role’s risk and how fast the rules change.
06 The Article 83(2)(d) mitigation calculus
Article 83(2) lists eleven factors an authority weighs when setting a fine. Point (d) is “the degree of responsibility of the controller or processor taking into account technical and organisational measures implemented by them pursuant to Articles 25 and 32”.
A documented training program is the strongest evidence you can offer on that point. When the ICO cut British Airways’ proposed GBP 183 million fine to GBP 20 million in 2020, it cited remedial steps that included staff training.
H&M shows the opposite: EUR 35.3 million in 2020, with the Hamburg authority treating the lack of effective training and supervision as an aggravating factor.
07 An evidence pack built for your supervisory authority
A GDPR scenario starts where data really leaks: a chat that turns into a spoken DSAR, a marketing brief asking for a segment with no recorded lawful basis, a ticket to copy production data into staging, a lost laptop that starts the 72-hour clock.
The learner’s decisions are scored against the article in question. So the DPO’s export says “Article 33 breach response: 412 staff trained, median time-to-report 47 minutes, scenario version 2026.04”, not “96% completion”.
Data protection risk sits in specific jobs, so assignments do too:
- Marketing: Marketing Consent Management and Consent Dark Patterns.
- Customer support: Legitimate DSAR Processing and Fraudulent DSAR Detection.
- Engineering: Privacy by Design Review, PII Document Redaction and Cross-Border Data Transfers.
- HR and finance: Personal Data Deletion Failures and Data Mapping.
- DPO: the full library plus the Data Protection Impact Assessment scenario.
Assignments refresh every quarter and after each significant regulatory change.
A supervisory authority wants the evidence pack, not a dashboard screenshot. It holds timestamped records per employee, signed acknowledgments, a version history linking each scenario to its article and any guidance updates, the refresh log, and the reasoning behind each role mapping.
It slots into the Article 32 section of an audit response, and into an Article 83(2)(d) mitigation submission if enforcement starts.
Every scenario ships as SCORM 1.2 and 2004, so the same pack comes out of Cornerstone, Workday Learning, Docebo, SAP SuccessFactors or any standards-based LMS.
Article by article, the scenarios that cover it
Organisational measures that sit beside training under Article 32.
Article 39: DPO awareness and training duty
Article 39(1)(b) makes staff awareness and training a DPO task. RansomLeak gives the DPO scenarios for every team that touches personal data, and the completion records export straight into the pack shown to the supervisory authority.
Each scenario carries a version stamp, so the DPO can show the content changed after Schrems II, the new SCCs and the Data Privacy Framework.
Article 32: organisational security measures
Article 32 asks for organisational measures that fit the risk, and the EDPB and Article 29 Working Party both count training as one.
When an authority investigates a complaint or breach, you can produce timestamped records per employee, signed acknowledgments and the content version history.
Article 5(1)(f): integrity and confidentiality principle
The integrity and confidentiality principle requires security against unauthorised processing and accidental loss.
The scenarios practise the everyday moments where that goes wrong: an email sent to the wrong person, personal data visible during screen sharing, production records copied into a test system, and a fake DSAR that needs checking.
Article 25: data protection by design and by default
Privacy by design is not only an engineering job. Every new form, dashboard or report is a privacy decision.
The Privacy by Design Review exercise gives product, design and engineering teams realistic feature decisions. It tests the three failures regulators cite most under Article 25: collecting too much data, choosing the wrong lawful basis, and weak default settings.
Article 28: processor obligations and the third-party vetting reflex
Article 28 allows only processors that give sufficient guarantees, under a written data processing agreement.
The Third-Party Data Processor Vetting exercise has procurement, security and engineering ask the right questions before a vendor touches personal data:
- Where is the data hosted?
- Which sub-processors are involved?
- How fast will they report a breach?
- What audit rights do we have?
It follows the vendor risk review most companies already run at procurement.
Articles 33 and 34: 72-hour breach notification window
Article 33 gives the controller 72 hours from becoming aware of a breach to notify the authority. Article 34 requires telling the people affected when the risk to them is high.
The Data Breach Response and Personal Data Breach exercises practise spotting, escalating, preserving evidence and meeting the deadline.
The clock starts when an employee knows, not when legal hears about it. That is why the program tracks time from spotting to reporting.
Article 47: Binding Corporate Rules and intra-group training
A group that relies on Binding Corporate Rules for intra-group transfers must train everyone who has permanent or regular access to personal data.
RansomLeak delivers the same scenarios to every legal entity in the BCR scope, translated where needed. The completion records meet Article 47(2)(n) and the EDPB BCR-C and BCR-P referentials.
Article 22: automated decision-making, profiling, and the AI overlay
Article 22 gives people the right not to be subject to decisions based solely on automated processing, including profiling, that have legal or similar effects. With the EU AI Act in force, this is the GDPR side of AI compliance.
The Safe GenAI Usage and Sensitive Data Exposure Through AI exercises cover the choices staff make with AI tools: what personal data can go into an LLM, what notice or consent is needed, what must be logged, and what the person can demand.
Recommended exercises
DSARs, consent, transfers and breach response, split by who handles the data.
- Personal Data Essentials The Article 4(1) vocabulary the rest of GDPR assumes: online identifiers people think are anonymous, Article 9 data hiding in free-text notes, and the controller, processor and third-party split that decides whether a file may leave. Try the exercise
- Everyday Privacy Duties Three duties that fall on ordinary staff, not the DPO: spotting a rights request that never says “GDPR”, reporting a misdirected file before the Article 33 clock runs, and keeping data out of tools with no Article 28 contract. Try the exercise
- Data Mapping and Records of Processing Article 30 records of processing, the base for every other control. The DPO and data stewards make realistic mapping decisions across systems, processors and lawful bases. Try the exercise
- Data Breach Response The Article 33 and 34 reflex against the 72-hour clock. Time from spotting to reporting is scored, because regulators weigh it under Article 83(2)(d). Try the exercise
- Legitimate DSAR Processing Article 15 access requests arriving by chat, phone and social media. Slow escalation within the one-month deadline is the failure authorities cite most. Try the exercise
- Fraudulent DSAR Detection Checking a DSAR that is really an attempt to get someone else’s data. The counterpart to the legitimate DSAR exercise. Try the exercise
- Cross-Border Data Transfers Transfers after Schrems II, which led to Uber’s EUR 290 million fine in 2024: SCCs, the Data Privacy Framework and transfer impact assessments. Try the exercise
- PII Document Redaction Redaction before a DSAR response or document share. Personal data left in metadata, footnotes or quoted threads turns a routine release into a reportable breach. Try the exercise
- Marketing Consent Management Choosing an Article 6 lawful basis, the e-Privacy rules for email and cookies, and consent records that survive an audit. Try the exercise
- Sensitive Data Exposure Through AI The Article 22 and Article 32 choices staff make when putting personal data into LLMs, the situation the Italian Garante’s OpenAI decision addressed. Try the exercise
- Unapproved AI Notetakers An unapproved AI notetaker records a confidential HR meeting and posts a public recap link: Article 5 principles and the Article 32 security duty in one meeting. Try the exercise
- Shadow AI Tools A whiteboard photo goes into a free consumer AI app with no Article 28 contract. The learner checks the approved-tool list and reports the upload. Try the exercise
- Using AI Within the Law What may go into a prompt: an approved tool with an Article 28 agreement, only the data the task needs, and no Article 9 health data or details about third parties. Try the exercise
Further reading
Related glossary terms
References
- Regulation (EU) 2016/679 (General Data Protection Regulation) EUR-Lex
- Guidelines, Recommendations, Best Practices European Data Protection Board (EDPB)
- Data Protection Officers Guidance UK Information Commissioner's Office (ICO)
- Article 29 Working Party Guidelines on Data Protection Officers European Commission Article 29 Working Party
- CNIL Data Protection Guidance Commission Nationale de l'Informatique et des Libertés
Show your DPA the training, not just the policy
Role-based GDPR scenarios and an Article 5(2) evidence pack.
Frequently asked questions
What is GDPR security awareness training?
GDPR employee training is the structured education program that satisfies Article 39 DPO duties and the Article 32 organisational measures obligation. EU and EEA Data Protection Authorities now treat training records as part of the Article 83(2)(d) calculus when sizing fines, and the regulation reaches every controller and processor handling EU resident data, wherever they are based.
Can RansomLeak host our training data in the EU?
Yes. The Cloud LMS runs in an EU region (Ireland) or a US region, chosen when your tenant is created, and the database, uploads, reports, and backups stay in that region. That keeps learner data inside the EEA and simplifies the Chapter V transfer analysis.
Organizations that need stricter separation run a dedicated single-tenant private cloud in the EU, or an on-premises install on their own infrastructure that keeps learner data entirely inside their own perimeter.
What does GDPR Article 39 require for employee training?
Article 39(1)(b) lists the tasks of the Data Protection Officer and explicitly names monitoring compliance with the GDPR "including the assignment of responsibilities, awareness-raising and training of staff involved in processing operations, and the related audits". The article makes training a continuous DPO duty, not a one-off project, and the EDPB and the former Article 29 Working Party guidance on DPOs both treat it as a baseline expectation.
In practice, satisfying Article 39 means the DPO can produce a current training plan, role-based scenario coverage, per-employee completion records, signed acknowledgments, and a refresh log that shows content was updated after material regulatory events. The supervisory authority looks for evidence of an ongoing program, not a slide deck filed in a SharePoint folder.
Does GDPR mandate annual data protection training?
The GDPR text does not specify a frequency. National DPA guidance (CNIL in France, BfDI in Germany, ICO in the UK, the Irish DPC) has settled on annual as the floor and quarterly to monthly as the operating norm for high-risk roles. EDPB Guidelines 09/2022 on personal data breach notification reinforce the expectation that training is a continuous control.
The defensible cadence depends on the role. The DPO and the breach response team need monthly drills. Engineering and customer support need quarterly refreshes tied to product and regulatory change. The general workforce needs annual training plus a refresher when the privacy notice or major processing activities change. New hires who touch personal data should complete training before they are granted production access, not within 30 days of starting.
Who needs GDPR training in our organisation?
Every workforce member who touches personal data, which in most organisations is most of the workforce. The DPO needs the full regulation. Marketing needs consent, legitimate interest, and the e-Privacy Directive overlay for cookies and email outreach. Sales needs lawful basis, transfer mechanisms, and the rules on buying contact lists. HR needs special category data under Article 9 and the limits the H&M decision drew on employee monitoring.
Engineering needs Article 25 privacy by design, the risks of production data in test environments, and Article 22 rules on automated decision-making. Customer support needs DSAR recognition and the 72-hour breach reporting clock. Finance needs the rules on payment-card data and the special category treatment for sickness and benefits records. Each role gets the scenarios that match its job, scored against the article being trained.
What evidence do DPAs look for when auditing GDPR training?
The expected evidence pack includes per-employee training records with timestamps, signed acknowledgments confirming understanding, content version history showing how material has been updated as the regulation and DPA guidance have evolved, a refresh log covering material events (Schrems II, the new Standard Contractual Clauses, the EU US Data Privacy Framework, EU AI Act), and the role-mapping rationale that shows why each cohort received the content it did.
A screenshot of an attendance sheet does not pass. The pack is the artefact the DPO presents in the Article 32 organisational-measures section of the audit response and in the Article 83(2)(d) mitigation submission when an enforcement action is opened. Build it once and refresh it on the same cadence as the training itself.
How do training records affect GDPR fines under Article 83?
Article 83(2) lists eleven factors a supervisory authority weighs when sizing a fine. Subsection (d) is "the degree of responsibility of the controller or processor taking into account technical and organisational measures implemented by them pursuant to Articles 25 and 32". A documented, role-based, current training program reduces the fine. The absence of one increases it.
British Airways is the clearest example. The ICO originally proposed GBP 183.39 million in 2019 and issued a final GBP 20 million penalty notice in October 2020, citing remedial actions including a refreshed staff security training program among the mitigating factors. The H&M EUR 35.3 million fine in 2020 ran the opposite direction: the Hamburg DPA cited the absence of effective training and supervisory controls as an aggravating factor in the responsibility calculation.
Do we need GDPR training if we are a US company with EU customers?
Yes. Article 3 gives the GDPR extraterritorial reach. The regulation applies to any controller or processor that offers goods or services to data subjects in the European Union or monitors their behaviour, regardless of where the organisation is established. A US SaaS that signs up an EU customer falls inside the regulation, and so does a US ad-tech vendor that drops cookies on EU residents.
The training obligation tracks the substantive obligation. If you are inside Article 3, you are inside Article 32, and Article 32 organisational measures include staff training. The Uber EUR 290 million fine in August 2024 was issued by the Dutch DPA against Uber Technologies Inc and Uber BV for unlawful EU to US transfers, the clearest recent reminder that the regulation reaches across the Atlantic.
What is the difference between GDPR training and security awareness training?
Security awareness training teaches the workforce to spot and report security threats: phishing, social engineering, malicious attachments, credential reuse, lost devices. GDPR training teaches the workforce to handle personal data lawfully: consent, lawful basis, data minimisation, retention, transfer rules, DSAR handling, breach reporting under the 72-hour clock.
The two programs share muscle memory. Breach recognition, incident reporting, and verification reflex apply to both. The mature pattern is a single human risk management backbone that covers security awareness, GDPR, NIS2, and the EU AI Act in one role-based scenario library, with separate evidence packs for each regulator. Running them as two unrelated tracks doubles the budget and halves the retention.
Does AI use require additional GDPR training under Article 22?
Yes. Article 22 grants the data subject the right not to be subject to a decision based solely on automated processing, including profiling, that produces legal or similarly significant effects. The article is the GDPR side of the AI compliance bar that the EU AI Act now sits on top of, and the Italian Garante EUR 15 million fine against OpenAI in late 2024 for ChatGPT privacy violations is the working reference for how DPAs read it.
The training overlay covers the data-protection decisions staff make when using AI tools: what personal data may be sent to an LLM, what consent or notice is required, what audit trail must be preserved, what the data subject is entitled to demand. The Safe GenAI Usage and Sensitive Data Exposure Through AI scenarios drill those decisions for engineering, marketing, customer support, and any role whose job has been augmented by an AI assistant in the past two years.