SOC 2 security awareness training
SOC 2 has no training rule of its own. Auditors read it into CC1.4 and CC2.2, then sample your completion records across the whole Type II window.
Five-to-ten-minute 3D exercises mapped to each SOC 2 duty, with completion evidence your auditor can export.
At a glance
- Report
- Type I tests one date; Type II a 3 to 12 month window
- Criteria cited
- CC1.4 competence and CC2.2 internal communication
- Who attests
- A licensed CPA firm, under AICPA attestation standards
- Sampled
- New joiners against start date, everyone else against refresher date
Trusted by teams at





Founded by the creator of Kontra Application Security Training.
Play the exercises behind your SOC 2 program
Each one is a 3D scenario your staff finish in 5 to 10 minutes. Pick one and play it here, with no sign-up.
Exercises run in interactive 3D environments.
Trust Services Criteria, mapped to exercises
Where your auditor's test steps land, and the exercises whose completion records answer them.
CC1.4 Security Awareness & Communication CC6.1 Logical Access Controls CC6.7 System Operations Monitoring CC7.2 Anomaly & Incident Detection CC7.3 Incident Response CC9.2 Risk Mitigation CC3.2 Risk Identification (AI & Emerging Tech) CC8.1 Change Management & Secure Development Type I checks a date. Type II checks every month.
A Type II auditor samples across the observation window, so a refresher that lapsed in month five becomes an exception in the report.
- Type I One point in time Is the training control designed and in place on the report date?
- Type II 3 to 12 months Did it operate all period: hires trained on time, refreshers done, exceptions closed?
- Sample Pulled from your HRIS Each sampled person is checked against their own due date, not the company average.
An exception is not a failed audit, but it is printed in the report your customers read.
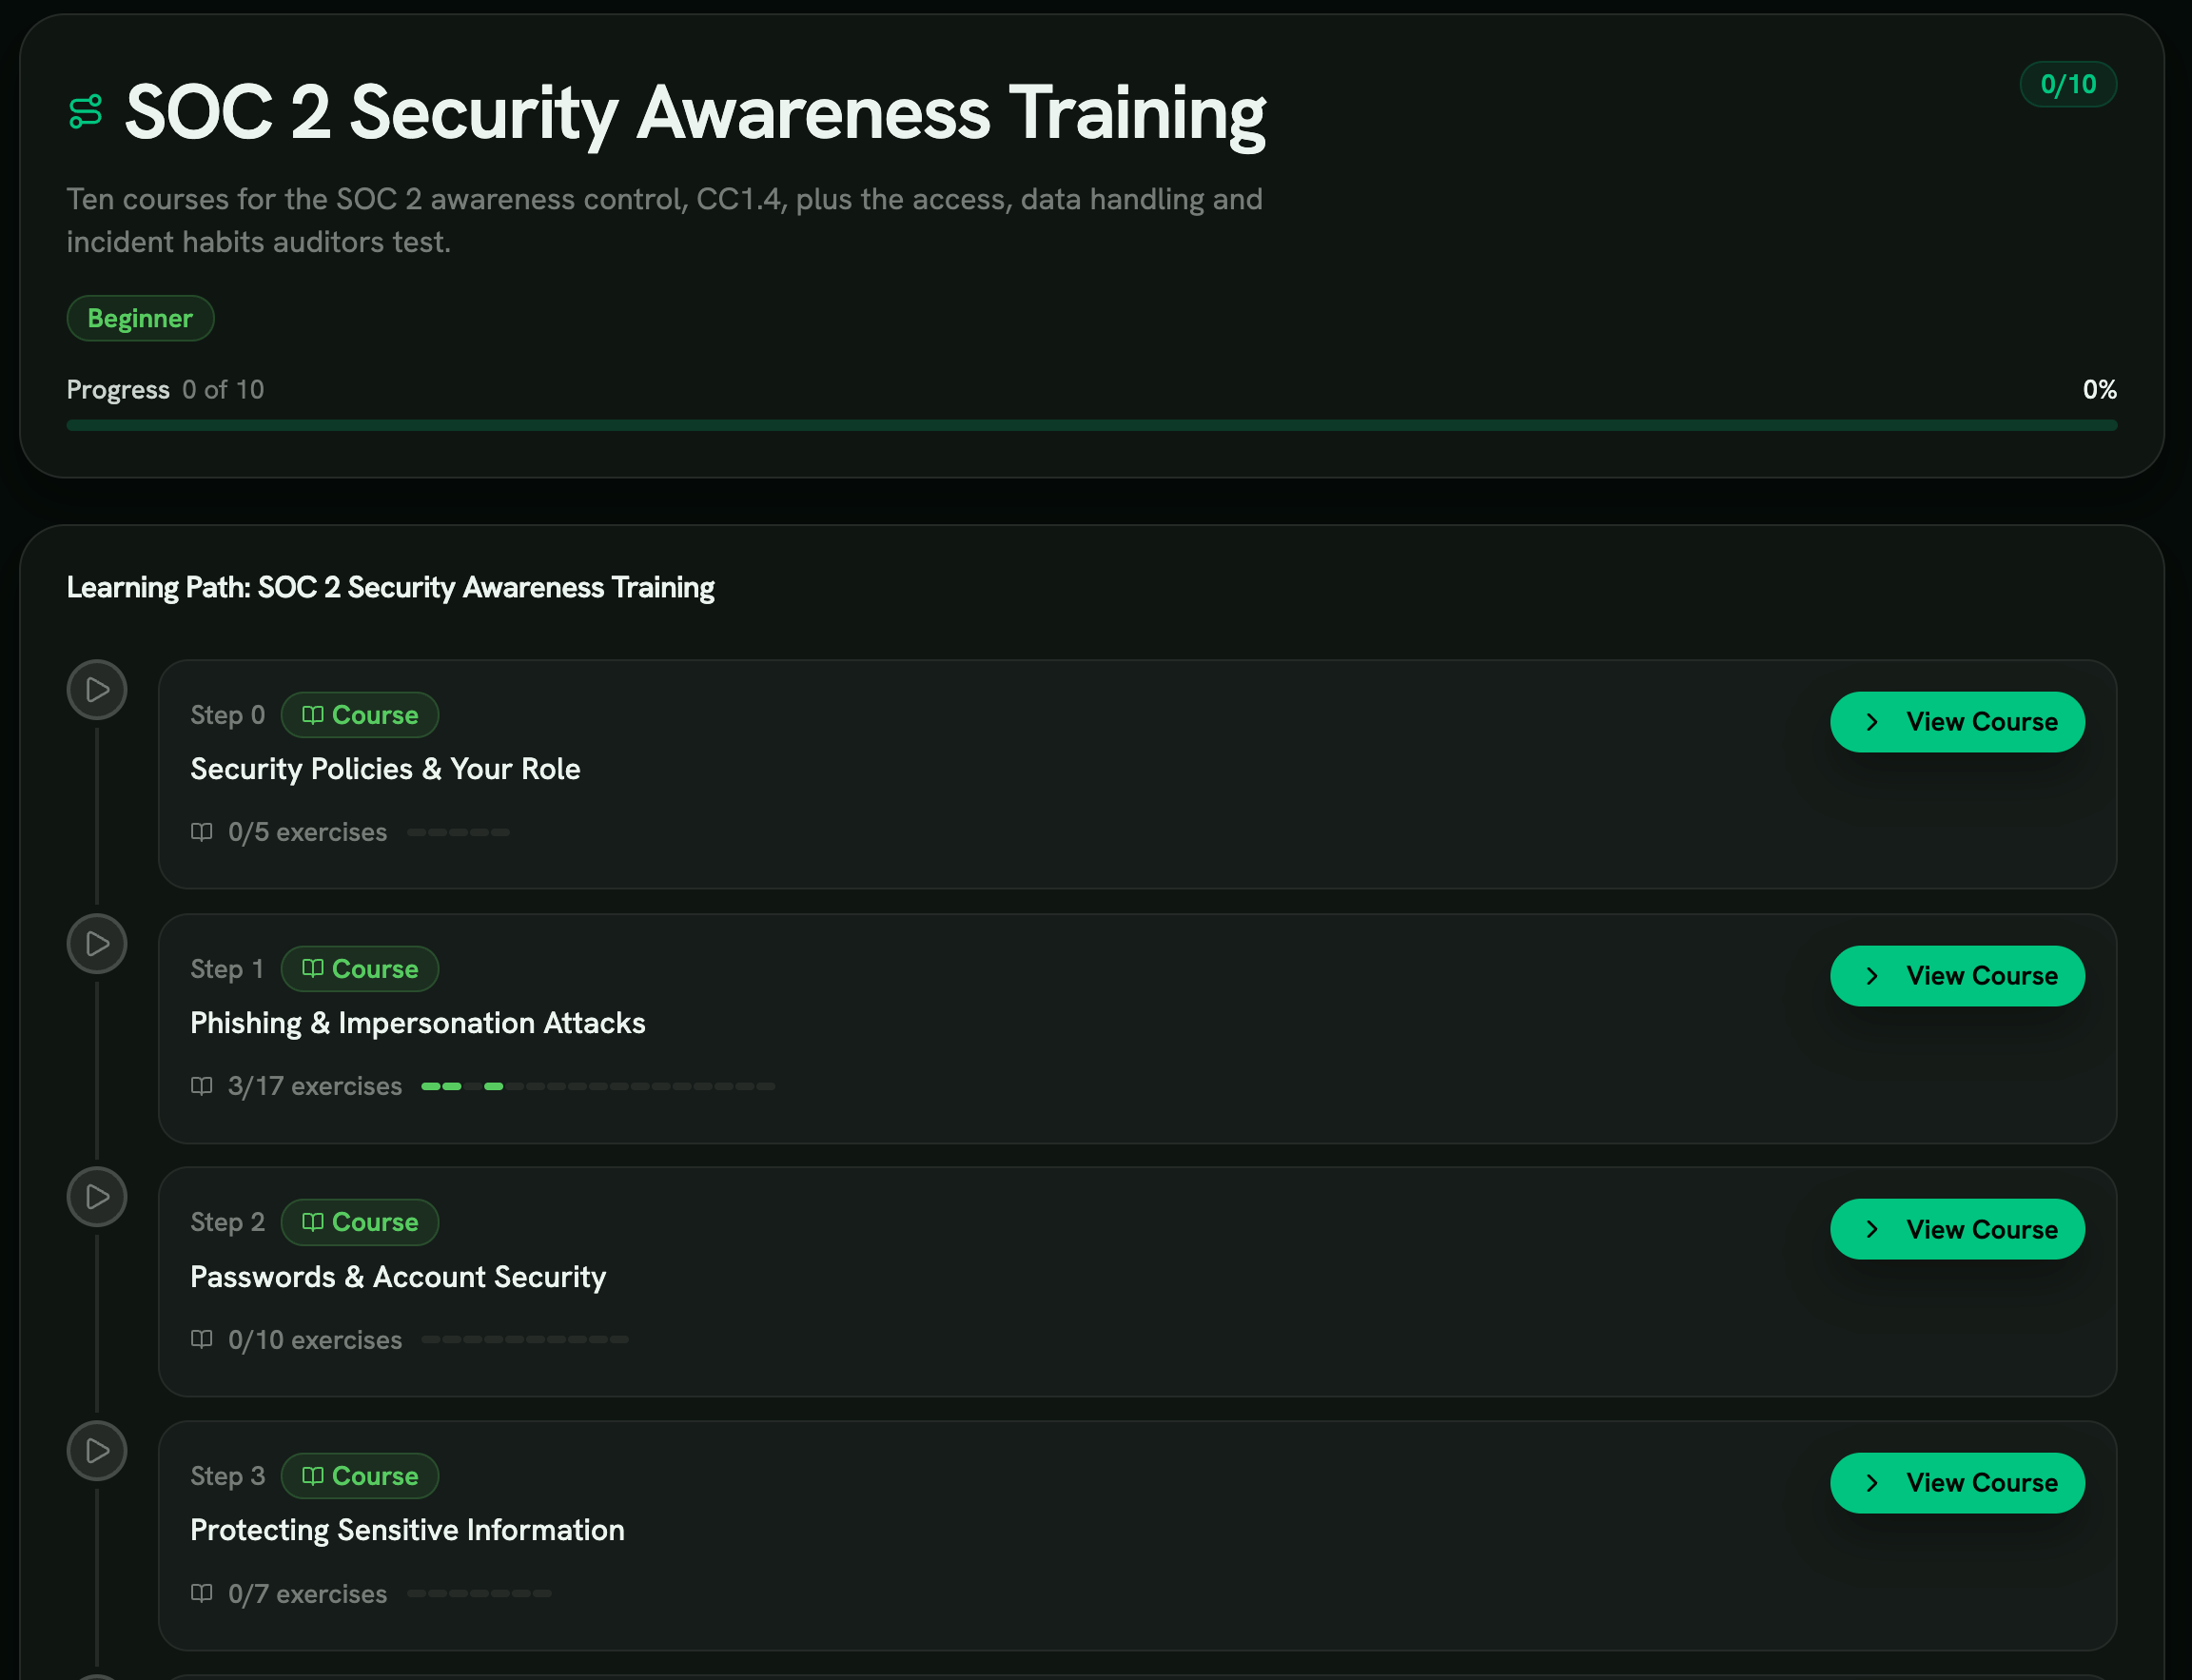
Ten courses mapped to the Trust Services Criteria
The SOC 2 path tags every step to the criterion it supports, from CC1.4 awareness to CC9.2 risk mitigation.
- CC1.4 first
- Security policies and your role opens the path, the awareness commitment auditors test.
- CC6 and CC7 next
- Phishing, passwords and sensitive data cover access, protection and incident response.
- Progress per person
- Each learner sees 0 of 10 move as they finish, and so does your auditor.
What a SOC 2 auditor actually tests
How the Trust Services Criteria turn into the test steps a CPA firm runs.
01 Scope and period of operating effectiveness
A Type I report tests design on one day. A Type II report tests whether the control worked across a period, usually six months for a first audit and twelve after that.
Anyone who held in-scope access on any day of that period needs a training record covering that day. A new hire who joined on day 364 counts. So does a contractor who had production access for two weeks.
Auditors sample from everyone who had access during the period, not from the headcount on the last day.
02 CC1.4 control activity and internal communication
CC1.4 asks the entity to show a commitment to competence. Its point of focus says the entity trains people to build and keep the competencies its objectives depend on.
Expect the auditor to ask for five things: the program description, the curriculum, the assignment policy, how completion is tracked, and what happens to people who do not finish.
CC2.2 adds internal communication. People must be told about the program, reminded, and escalated, and management must be able to see who has completed it.
03 Role-based training depth
One video for everyone is how programs draw exceptions. Auditors expect depth that matches each role’s risk:
- Engineering: secure coding, OAuth consent abuse, secrets, and prompt injection in AI assistants.
- Customer support: verification steps, social engineering pretexts, and least privilege.
- Finance and AP: business email compromise, deepfake wire fraud, and call-back verification.
- Executives and assistants: whaling and personal-device hardening.
- Contractors: a baseline scoped to their access.
The auditor reads the mapping, then samples completions from each group.
04 Per-employee evidence and LMS exports
The deliverable is a completion register with one row per person: name or anonymised ID, role, hire date, training assigned, training completed, timestamp, and score where there is one.
Auditors pick names from the personnel list, ask for each person’s record, and trace it back to the source system.
An LMS export or a SCORM completion record holds up. Screenshots, signed PDFs and email receipts are weak evidence and lead to follow-up requests.
05 Refresh cadence
The Trust Services Criteria set no refresh interval. Once a year is the practical minimum.
Many auditors now expect more than that: short quarterly modules, monthly phishing exercises, or refreshers when the product or attacker techniques change.
One all-hands video at the start of a twelve-month window, never refreshed, can earn an exception even if every employee completed it.
06 Type I versus Type II evidence demands
Type I evidence shows the program exists on a given date: a written policy, a configured LMS, assignments made.
Type II evidence shows it ran. Everyone in scope finished on time, exceptions were tracked and closed, and management reviewed completion on a schedule.
Enterprise buyers read the Type II report because it shows the control working across the window. Type I opens the conversation; Type II is what procurement signs off on.
07 Building the register your CPA firm samples
A CC1.4 test asks whether people are competent, not whether they pressed play. Each exercise drops the learner into a simulated inbox, call or meeting and records what they decided.
So the record in your LMS shows a skill being used, not minutes spent. That is easier to defend than a video with a checkbox on the last screen.
SOC 2 rewards a curriculum you can explain by role:
- Finance and AP: business email compromise, vendor-invoice fraud and deepfake wire requests.
- IT and help desk: vishing, MFA-reset pretexts and verification steps.
- Engineering: least privilege, OAuth consent and safe AI use.
- Executives and assistants: whaling, deepfake video and reporting.
- Contractors: a scoped baseline.
Assignments land in the LMS you already use, through SCORM 1.2 and 2004 packages or the API for Cornerstone, Workday Learning, Docebo, SAP SuccessFactors and Moodle.
What the auditor wants is the evidence pack: the program description, the role mapping, the assignment policy, a completion register for the whole period, exceptions with the date each was closed, and a quarterly management review.
That list matches the AICPA SOC 2 description criteria and the guidance from the large audit firms. Buyers reading your report then find the awareness control described in concrete terms.
Criterion by criterion, where the exercises land
Controls auditors expect to see working next to training.
CC1.4: documented security awareness program with role-based content
The curriculum is published and mapped to standard roles: engineering, support, finance, AP, executives, IT and contractors.
The program description, assignment policy and completion criteria are written down and can be exported for the auditor. Training matched to role is what the CC1.4 point of focus asks for.
CC1.4: per-employee completion evidence with timestamps
Each finished exercise creates a record with the user ID, role, exercise, timestamp and pass status.
You can export it as CSV or JSON, or send it through SCORM 1.2 and SCORM 2004 packages into Cornerstone, Workday Learning, Docebo, SAP SuccessFactors, Moodle or another standards-based LMS. The format matches what auditors sample during fieldwork.
CC1.4: training assignment to all in-scope personnel
Training is assigned at onboarding through your HRIS or directory sync, so new hires get their role’s exercises shortly after access is granted. Contractors get a scoped baseline the same way.
When the auditor samples new joiners and contractors, each one has a record.
CC1.5: personnel responsibility and accountability
Managers and the security team see who has finished. Non-completers are escalated, and failed scenarios trigger tracked remediation.
That manager view supports CC1.5, which holds people accountable for their security responsibilities across the audit period.
CC2.2: internal communication of security information
Assignment notices, reminders and program updates go out by email, Slack or Microsoft Teams. Management gets a monthly status summary.
The templates, reminder schedule and escalation rules are documented, which gives the auditor evidence for CC2.2.
CC2.3: external communication where required
If vendors and contractors sit inside your trust boundary, they are assigned training the same way, with their own role groups and reports.
That covers the CC2.3 point of focus on telling external parties what is expected of them.
CC1.1 and CC1.5: management oversight and review evidence
A quarterly review report shows coverage, completion by role, open exceptions and remediation. It is a table you can send to the audit committee or security steering group.
Auditors testing CC1.1 and CC1.5 use it to confirm management oversaw the program for the whole period.
Refresh cadence beyond annual
New scenarios ship every month and follow changes in attacker technique.
Short quarterly modules and monthly role exercises give a steady stream of completion records, which satisfies auditors who expect more than one annual touch. They also cover deepfake video, AI-written phishing, MFA fatigue and OAuth consent abuse, which last year’s video does not.
Report exceptions where training was the weak control
What auditors wrote up, and what the fix looked like the next year.
SolarWinds 2020: clean SOC reports preceded the breach
SolarWinds held current SOC 1 and SOC 2 attestations when the SUNBURST compromise was disclosed in December 2020. CISA, the Department of Justice and Mandiant traced it to attacker access in the Orion build pipeline that went unnoticed for months.
The lesson is about scope. A SOC 2 report describes how controls operated against the Trust Services Criteria during a period. It does not promise that no breach will happen.
Since then, buyers and auditors have asked for stronger evidence on awareness training, secure development and access control.
Common audit pattern: missing completion evidence for new hires and contractors
The exception auditors cite most often, according to practice notes from firms such as Schellman and A-LIGN, is missing completion records for people who joined mid-period or worked as contractors.
A typical case: training ran in January, a new hire started in August, a contractor had production access from June to September, and neither got the module soon after access was granted.
The Type II report then lists a CC1.4 exception, because the control did not operate for that group during the period.
Common audit pattern: annual video with no role-based depth
The second common finding is one generic video assigned to everyone, with no role modules and no refresh during the period.
The auditor sees that engineering, finance, support and executives all got the same content. A lenient auditor writes a management-letter recommendation; a strict one records a formal exception.
Experienced auditors read “competencies needed to support the achievement of objectives” as training matched to each role’s risk.
Recommended exercises
Pick by department: finance, help desk, engineering and executives each have a set.
- Employee Security Responsibilities Covers personnel responsibility for CC1.5: access duties, what to report, and who is accountable. Try the exercise
- Phishing The baseline exercise auditors expect every in-scope employee to finish during the period, under CC1.4. Try the exercise
- Business Email Compromise Role depth for finance and AP, which is what CC1.4 means by competencies tied to objectives. Try the exercise
- MFA Setup & Best Practices Phishing-resistant MFA in practice, giving you evidence for both CC1.4 and CC6.1. Try the exercise
- MFA Fatigue Attack Push-bombing, the MFA bypass auditors now expect a current curriculum to cover. Try the exercise
- Least Privilege Awareness Role depth for engineering and IT, mapped to CC6.1 access control as well as CC1.4. Try the exercise
- Reporting Culture Builds the habit of checking and reporting, which supports CC2.2 and CC7.3. Try the exercise
- General Incident Reporting Practises the reporting flow behind CC7.2 detection and CC7.3 incident response. Try the exercise
Further reading
Related glossary terms
References
- SOC 2 Report AICPA
- 2017 Trust Services Criteria with Revised Points of Focus 2022 AICPA
- Cost of a Data Breach Report 2024 IBM Security and Ponemon Institute
- SSAE No. 18 Attestation Standards AICPA
Walk into fieldwork with the register ready
We export the population, completions and exceptions for your exact Type II window.
Frequently asked questions
What is SOC 2 security awareness training?
SOC 2 is the AICPA attestation report that B2B SaaS buyers ask for before they sign. Security awareness training is named explicitly in Common Criterion CC1.4, and Type II auditors test the control across a six to twelve month period of operating effectiveness.
What is SOC 2 CC1.4?
CC1.4 is one of the nine Common Criteria families in the AICPA Trust Services Criteria (TSP Section 100, 2017 with 2022 revised points of focus). It requires the service organization to demonstrate a commitment to attract, develop, and retain competent individuals in alignment with objectives.
The control activity language is explicit: the entity provides training to enable personnel to develop and maintain the competencies needed to support the achievement of objectives. Auditors read this as requiring a documented security awareness program with per-employee completion evidence and role-based content depth.
Does SOC 2 require security awareness training?
Yes. Security awareness training is named explicitly in Common Criterion CC1.4 within the Trust Services Criteria. The criterion is mandatory for any SOC 2 report that includes the Security category, which is the only category required for every SOC 2 attestation.
The criterion is enforced through a documented program, per-employee completion records, role-based content, and a refresh cadence sufficient to keep the workforce competent against current threats. Type II auditors test that the control operated effectively across the entire period of operating effectiveness, not just at a single point in time.
Is one course a year enough for SOC 2 Type II?
The Trust Services Criteria do not name a specific refresh frequency. Annual is the practical floor that most auditors accept for a baseline program, and it is what most service organizations document in their training policy.
Modern auditor practice notes from firms like Schellman, A-LIGN, and Coalfire increasingly read CC1.4 as requiring more than annual: quarterly micro-modules, monthly role-based exercises, or refreshers tied to new attacker techniques. A program that runs one all-hands video and nothing else across a twelve-month period of operating effectiveness will draw an exception from a thoughtful auditor.
What evidence do SOC 2 auditors check for training?
Auditors expect three artifacts. First, a documented training program description: curriculum, cadence, scope, assignment policy, and completion criteria. Second, a per-employee completion register for the full period of operating effectiveness, listing user identifier, role, training assigned, completion timestamp, and pass status. Third, evidence of role-based content depth that matches the risk profile of each job function.
Acceptable evidence is an LMS export (Cornerstone, Workday Learning, Docebo, SAP SuccessFactors, Moodle) or a SCORM completion record. Screenshots, signed PDFs, and email receipts are weak evidence and invite follow-up requests. Auditors sample from the personnel listing and trace each sample back to the source training record.
Type I versus Type II for training evidence: what is the difference?
Type I evidence is point-in-time: the program exists, the policy is documented, the LMS is configured, and assignments have been made. The auditor inspects design and confirms the control is in place on a single date.
Type II evidence is operational: the program ran throughout the period of operating effectiveness (six or twelve months), every in-scope person completed it on time, exceptions were tracked and remediated, and management reviewed completion status on a defined cadence. Enterprise buyers usually require Type II reports because Type II tells them the control worked in practice across the audit window, not just on the day the auditor visited.
Do contractors need SOC 2 security awareness training?
Yes, when contractors hold access to in-scope systems or data during the audit period. The SOC 2 personnel population includes employees, contractors, interns, and any third party with logical or physical access relevant to the trust boundary.
The most frequent qualified opinion pattern in Type II reports is missing completion evidence for contractors who held access for a short window during the period and never received the training assignment. The control needs to operate effectively for that population during the days they held access, not after they left.
How is SOC 2 training different from ISO 27001 awareness training?
The intent is similar; the framing differs. ISO/IEC 27001 Annex A (specifically A.7.2.2 in the 2013 version, A.6.3 in the 2022 version) requires information security awareness, education, and training. SOC 2 places the same requirement inside Common Criterion CC1.4 of the Trust Services Criteria, with CC1.5, CC2.2, and CC2.3 layering in personnel responsibility and communication.
The audit mechanic is also different. ISO 27001 is a certification against a management system standard with a three-year cycle and annual surveillance. SOC 2 is an attestation by a CPA firm that issues a report against the Trust Services Criteria for a defined period. Most enterprise buyers in North America ask for SOC 2; most enterprise buyers in Europe and APAC ask for ISO 27001. Many service organizations hold both.
What happens if a SOC 2 audit finds a training gap?
The auditor records an exception in the Type II report against the relevant Common Criterion (usually CC1.4). The exception describes the population sampled, the gap found, and the affected period. Depending on severity and scope, the report opinion is either unqualified with noted exceptions or qualified.
A qualified opinion is the failure mode that procurement teams flag. Buyers reviewing a qualified report ask follow-up questions, request remediation evidence, and may delay or block the contract. The remediation path is to close the gap, document the corrective action, and earn an unqualified opinion in the next reporting period.