NIS2 security awareness training
NIS2 makes training a board matter: Article 20 requires management bodies to be trained and holds them personally liable, and Article 21(2)(g) extends cyber hygiene training to everyone else.
Five-to-ten-minute 3D exercises mapped to each NIS2 duty, with completion evidence your auditor can export.
At a glance
- Directive
- (EU) 2022/2555, transposition deadline 17 October 2024
- Board duty
- Article 20(2): members of management bodies must follow training
- Staff duty
- Article 21(2)(g): cyber hygiene and cybersecurity training
- Fines
- Essential €10M or 2%; important €7M or 1.4%
Trusted by teams at





Founded by the creator of Kontra Application Security Training.
Play the exercises behind your NIS2 program
Each one is a 3D scenario your staff finish in 5 to 10 minutes. Pick one and play it here, with no sign-up.
Exercises run in interactive 3D environments.
When something goes wrong, Article 23 starts a clock
Trained staff are how a significant incident reaches the right person in hours, not days.
- 24 hours Early warning Alert the CSIRT or authority and flag suspected malicious or cross-border impact.
- 72 hours Incident notification Update with an initial assessment, severity and indicators of compromise.
- 1 month Final report Root cause, the mitigation applied and any cross-border impact.
If these measures fail, Article 20 lets authorities hold management personally liable.
What Articles 20 and 21 require, and of whom
Article 20, Article 21 and how national transposition changes the detail.
01 Stage 1: Scope determination (essential vs important entity)
First, check whether NIS2 applies at all. It covers 18 sectors, split into Annex I (essential) and Annex II (important), with size thresholds from Commission Recommendation 2003/361/EC.
As a rule, medium and large organisations are in scope:
- Important: 50+ employees and EUR 10M+ turnover, or a balance sheet of EUR 43M+.
- Essential: 250+ employees and EUR 50M+ turnover.
Some smaller entities are in scope regardless of size, including trust service providers, top-level domain registries, DNS providers and public electronic communications providers. Non-EU entities offering services in the EU are covered under Article 26 and must appoint an EU representative.
02 Stage 2: Article 20 governance and management body training
Article 20 makes the management body approve and oversee the cybersecurity risk measures. It also requires every member of that body to take training good enough to spot risks and judge practices.
Infringements carry personal liability. National authorities can even bar a named person from management roles for a time.
A one-off board briefing no longer covers it. The management body needs its own track, with records, covering its governance duties, the entity’s risk position and the consequences of falling short.
03 Stage 3: Article 21(2)(g) cyber hygiene practices and cybersecurity training program
Article 21(2)(g) requires basic cyber hygiene and cybersecurity training for the whole workforce.
The safest reading pairs role-based scenarios (phishing, vishing, BEC, deepfakes, OAuth consent abuse, mobile devices) with policy modules on passwords, encryption and screen locking, incident reporting and acceptable use.
The hygiene wording follows ENISA’s guidance on risk-management measures. Auditors look for training proportionate to risk, refreshed regularly (once a year at minimum, monthly role content in practice), with completion records that hold up to sampling.
04 Stage 4: Article 21(2)(b) incident handling and Article 23 incident reporting cadence
Article 21(2)(b) requires incident handling procedures covering detection, response and recovery.
Article 23 then sets the reporting clock for a significant incident:
- an early warning to the authority or CSIRT within 24 hours of becoming aware
- an incident notification within 72 hours
- a final report within one month
Front-line staff have to recognise a significant incident and start that chain straight away. That is a trained skill, practised through reporting exercises and breach scenarios that follow the real notification path.
05 Stage 5: Article 21(2)(d) supply chain security and Article 21(2)(i) HR security
Article 21(2)(d) covers supply chain security, including direct suppliers and service providers. Procurement, engineering and security need scenarios on third-party OAuth apps, checking new vendors, and the changed-bank-details requests behind most BEC losses.
Article 21(2)(i) covers HR security, access control and asset management. Joiner-mover-leaver, guest access, verifying help desk requests, and encryption and screen locking all map here.
Authorities now check whether training reaches these areas too, not only the core phishing module.
06 Stage 6: National competent authorities, audits, and the penalty regime
Each Member State names its own competent authorities:
- Belgium: the CCB, under the NIS 2-Wet / Loi NIS 2.
- Germany: the BSI, under the pending NIS2UmsuCG.
- France: ANSSI.
- Ireland: the NCSC.
- Italy: AGID and ACN.
Fines reach EUR 10 million or 2% of global turnover for essential entities and EUR 7 million or 1.4% for important ones. Authorities can also issue public reprimands and suspension orders, and hold management body members personally liable.
ENISA coordinates EU-wide guidance and the CSIRT network. The first inspections are being scoped where the national law is already in force.
07 Board and staff tracks an inspector can follow
NIS2 audits sample evidence, not intentions. An exercise that puts the learner in an inbox, a vishing call, a BEC pretext or a deepfake video meeting gives the auditor a record linked to Article 21(2)(g) and to a specific risk.
A 30-minute compliance video only proves someone watched it. The directive sets no format, but authorities tend to read “proportionate to the risk” as training that reflects how attackers operate now.
The Verizon DBIR 2024 finding that 68% of breaches involve a non-malicious human element, and the EUR 25 million Arup deepfake fraud, are both part of the risk picture authorities cite.
Role tracks are how a NIS2 program shows proportionality:
- Management body, Article 20: governance, personal liability and a current-threat briefing.
- All staff, Article 21(2)(g): phishing, passwords, mobile devices, locking and encryption, incident reporting.
- IT and help desk, Articles 21(2)(b) and (i): vishing, MFA-reset social engineering, verification and joiner-mover-leaver.
- Procurement and engineering, Articles 21(2)(d) and (e): third-party OAuth apps, vendor checks and supply chain BEC.
Each track has its own completion list, so audit evidence is split by role from the start.
During an inspection, authorities ask for the export. Records come per learner, role and module, with acknowledgment timestamps, proof of passed scenarios, and metadata linking each exercise to its Article 21 measure.
The format suits the CCB, BSI, ANSSI, NCSC, AGID, ACN and other EU authorities. Building the export before the first inspection saves days compared with assembling it after the request arrives.
Article 21 measures, mapped to exercises
The Article 21 measures an inspector samples, matched to the board and staff tracks.
Art. 21(2)(g) Cyber Hygiene & Training Art. 21(2)(b) Incident Handling Art. 21(2)(d) Supply Chain Security Art. 21(2)(i) Human Resources Security Art. 21(2)(j) Cryptography & Encryption Art. 21(2)(e) ICT Acquisition & Development (AI Systems) Article 21 cyber hygiene, step by step
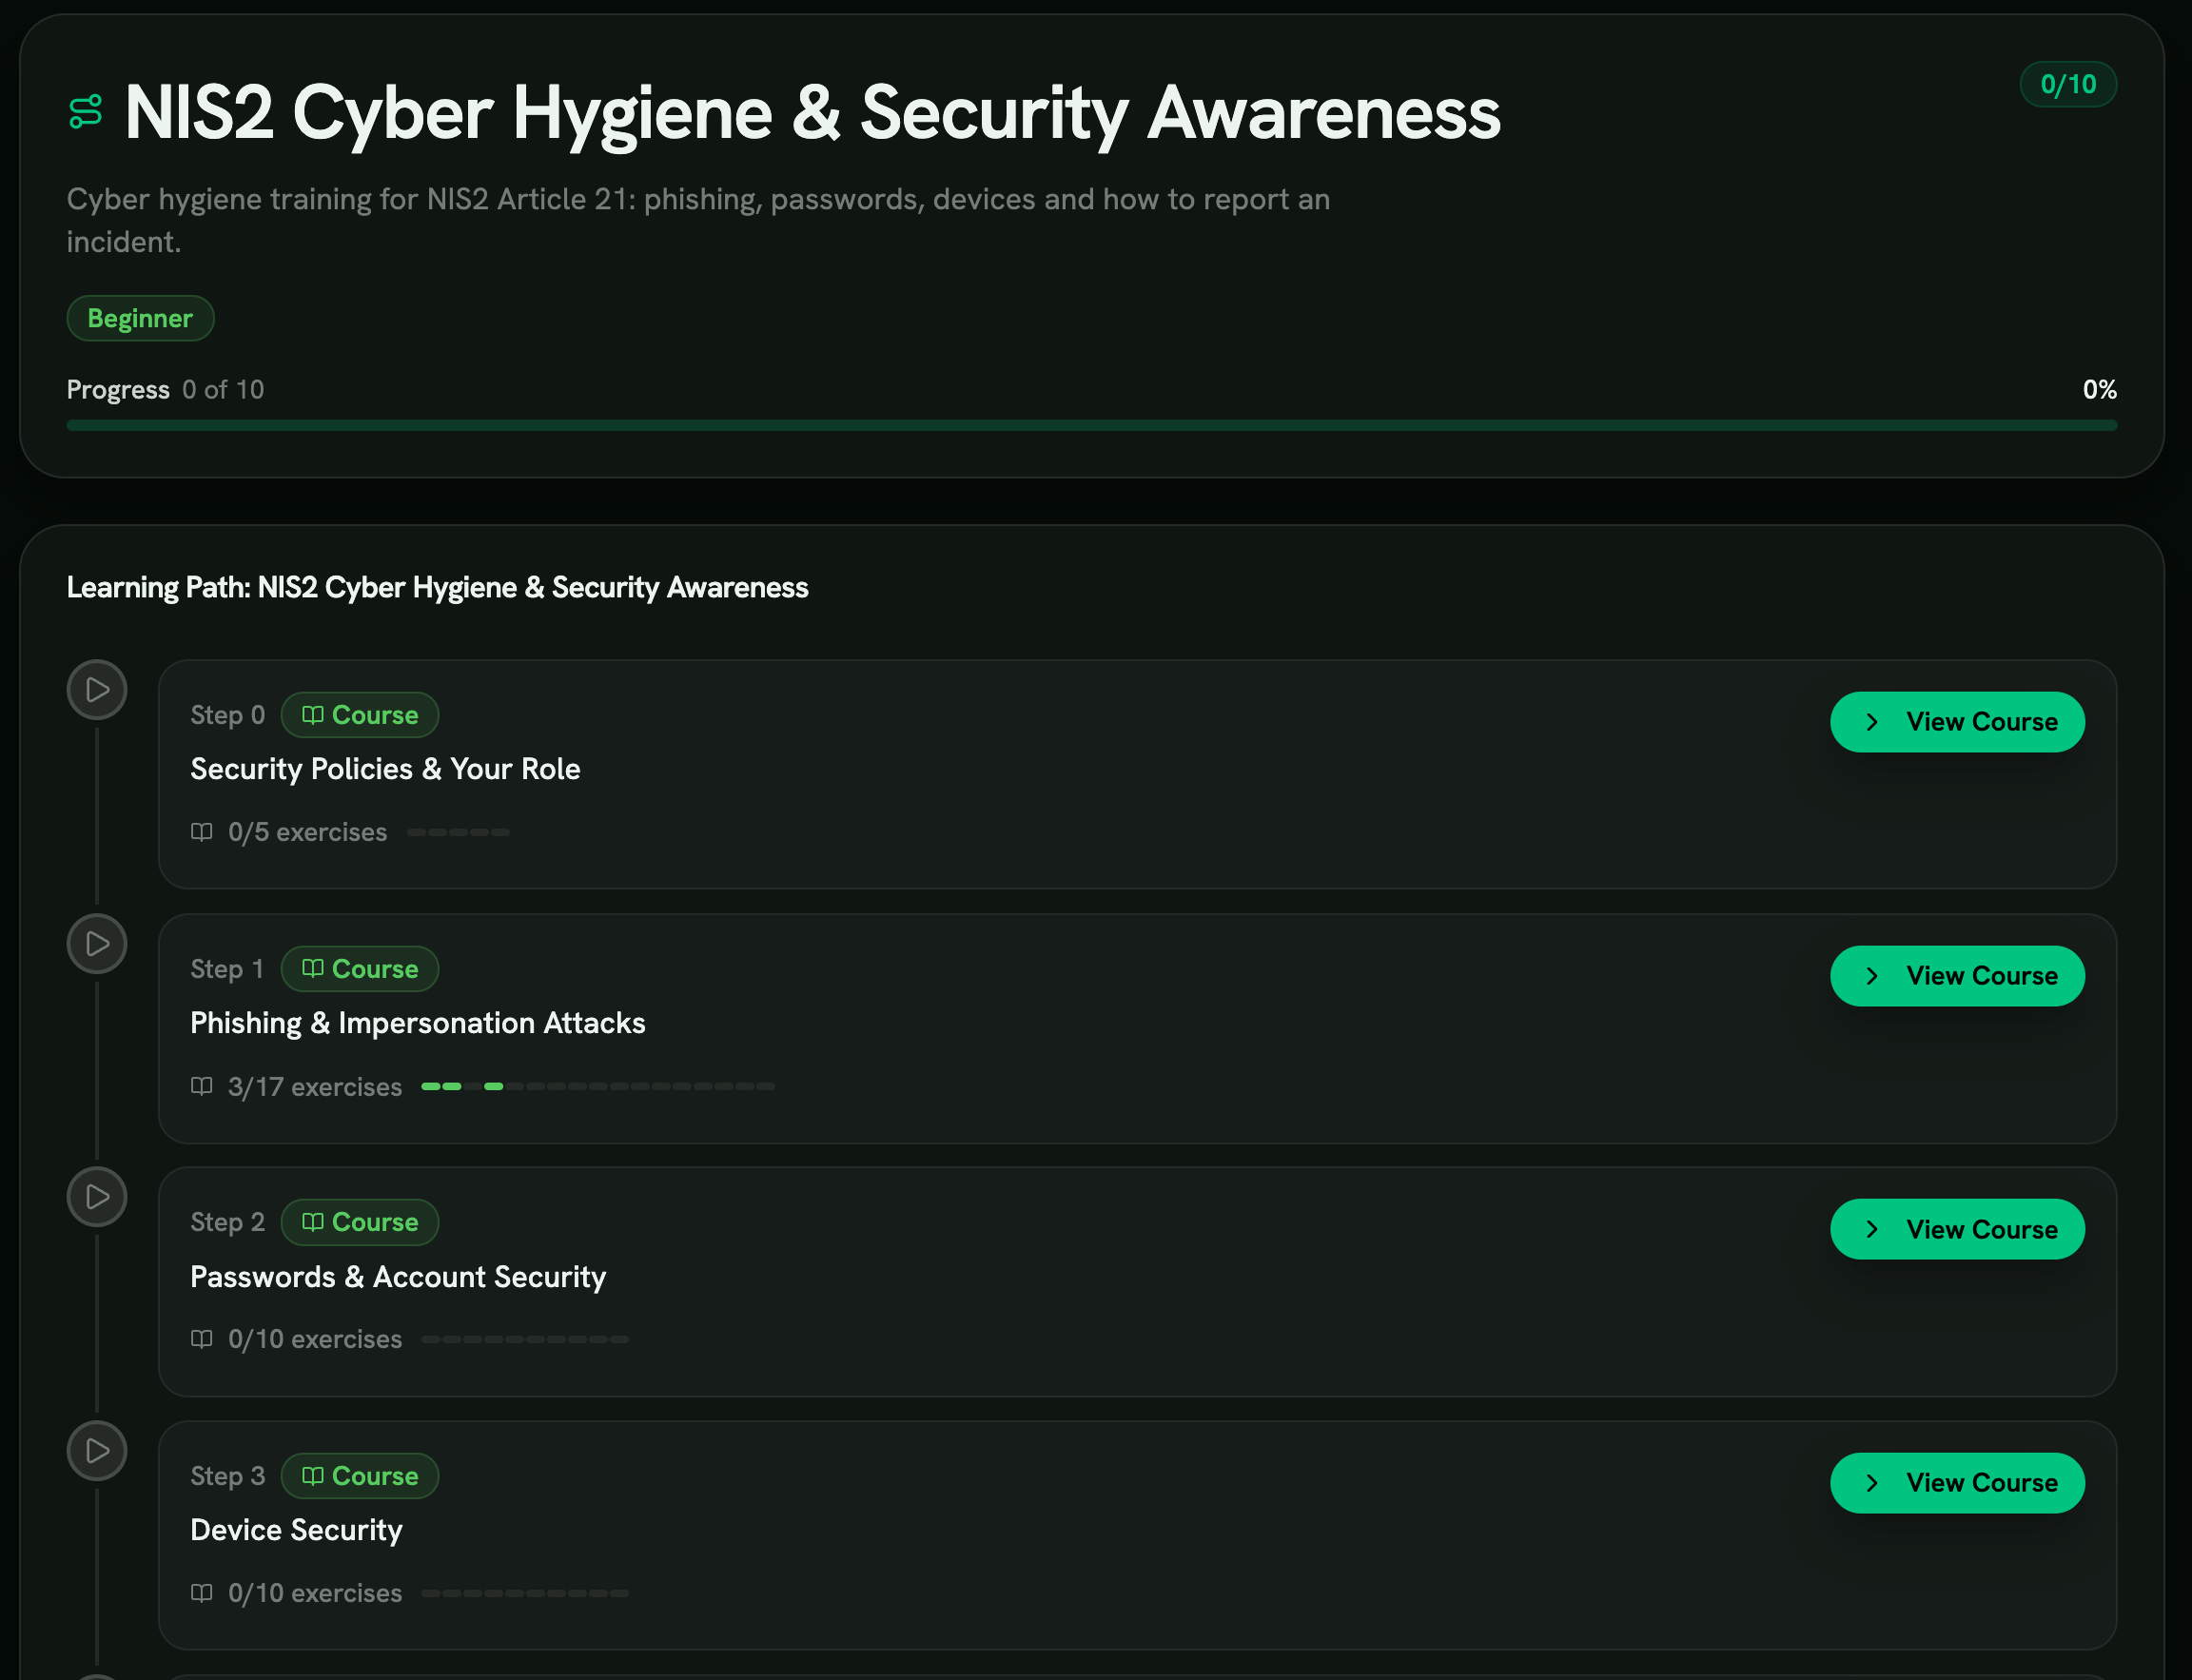
The NIS2 path maps to the Article 21 measures: risk analysis, incident handling, supply chain, hygiene, HR security and MFA.
- Letters (a) to (j)
- Each step names the Article 21(2) measure it supports.
- Hygiene in practice
- Phishing, passwords and device security make point (g) concrete.
- Ready for supervisors
- Ten courses with per-person progress for your national authority.
How member states are enforcing the training duty
National laws now make board members personally answerable for training.
Belgium NIS 2-Wet / Loi NIS 2 in force since October 2024
Belgium was the first EU country with a fully working NIS2 law. The NIS 2-Wet / Loi NIS 2 took effect in October 2024, on the directive’s deadline.
The Centre for Cybersecurity Belgium (CCB) is both the competent authority and the CSIRT. Its CyFun framework turns the Article 21(2) measures, training included, into auditable controls with maturity levels essential entities must reach by set dates.
The CCB can apply fines of EUR 10 million or 2% of turnover for essential entities and EUR 7 million or 1.4% for important ones. It has published royal decrees and a registration portal by sector. For Belgian essential entities, enforcement is real and the question of training evidence is no longer theoretical.
Germany NIS2UmsuCG draft delays and the legal limbo for essential entities
Germany missed the 17 October 2024 transposition deadline. The draft NIS2UmsuCG has been through cabinet several times without taking effect.
The BSI keeps issuing guidance under the existing IT-Sicherheitsgesetz, and German entities know the NIS2 duties apply once the law is published. Several large operators built training programs early so they are ready for inspection on day one.
The directive binds Member States, not companies, until national law transposes it. Still, under the European Court of Justice’s direct-effect doctrine, an in-scope company that ignores Article 21(2)(g) while waiting should not expect a lenient first inspection.
CCB CyFun framework as a worked example of Article 21(2)(g) in practice
Belgium’s CyFun framework is the clearest published example of a national authority turning the NIS2 measures into controls it can audit. It maps each Article 21(2) measure to named controls, sets maturity levels (Basic, Important, Essential) and gives each sector a deadline to reach its target.
Training sits under the Awareness and Training capability and cites both Article 20 (management) and Article 21(2)(g) (workforce hygiene). It also lists the role content other authorities now mention: phishing scenarios, incident reporting drills, supply chain awareness and governance modules for management.
Companies operating in several Member States increasingly use CyFun as their baseline until each national law arrives.
The Article 21 measures your people carry
Other Article 21 measures your staff make work.
Article 21(2)(g): cyber hygiene practices and cybersecurity training
Phishing, vishing, smishing, BEC, deepfake, mobile device and OAuth abuse scenarios map to the hygiene practices in Article 21(2)(g). Each module ships as SCORM 1.2 and 2004 or as a hosted assignment, and completion records export in the format authorities sample.
There is a baseline for everyone and role tracks that show the program fits the entity’s size and risk.
Article 21(2)(b): incident handling detection, response, and recovery
Incident reporting, reporting culture and personal data breach exercises train the recognition and escalation that Article 23 depends on.
Learners decide what an authority would ask: is this a significant incident, who do I tell, and what evidence do I keep? The 24-hour, 72-hour and one-month steps are taught as one connected timeline.
Article 21(2)(d): supply chain security including direct suppliers
Third-party OAuth apps, invoice and payment fraud, and verification procedures cover the supply chain risks authorities flag most in early audits.
Procurement and engineering also practise checking new vendors, governing OAuth consent and spotting changed bank details. Every completion is tied to a named role that deals with suppliers.
Article 21(2)(i): human resources security, access control, asset management
Joiner-mover-leaver, guest access, encryption and screen locking, employee security responsibilities and verification procedures map to the HR security and access control measures.
Joiners (setting access up correctly) and leavers (removing access and returning assets) are both covered, which closes the gap most audit findings cite.
Article 21(2)(j): cryptography and encryption policies
Encryption and lock discipline, mobile device security, and VPN use cover cryptography across laptops, removable media and remote access.
Learners practise the daily habits that turn a written cryptography policy into behaviour: locking devices, handling USB drives, and staying on trusted networks.
Article 20: management body approval, oversight, and personal liability
A separate track for the management body covers what Article 20 puts on leadership: approving risk measures, how often to oversee them, personal liability, the authorities’ powers to publish findings and bar managers, and a briefing on current threats.
Its completion records are kept apart, so evidence for the management body is never mixed with general staff records.
Article 23: incident reporting cadence (24 hours, 72 hours, one month)
Reporting exercises rehearse the three notification stages against a running clock: what goes in the 24-hour early warning, how the 72-hour notification is structured, and what the one-month final report covers, plus when to notify affected service users.
The drills mirror what the CSIRT and authority actually receive.
Article 21(2)(e): security in the acquisition of network and information systems
Deepfake audio detection, prompt injection, third-party OAuth apps and mobile app permissions cover the AI risks some authorities now cite under Article 21(2)(e).
Procurement and engineering tracks cover the security questions for buying AI components, supply chain dependencies, and OAuth integrations into core systems.
Recommended exercises
A board briefing track and a cyber hygiene baseline for every employee.
- Phishing The all-staff scenario for Article 21(2)(g) hygiene: checking AI-written email lures before acting. Try the exercise
- Business Email Compromise For finance and AP under Article 21(2)(d): the changed-bank-details requests authorities flag in audits. Try the exercise
- Whaling With A Deepfake For the management body under Article 20: leaders face the deepfake video call behind the 2024 Arup loss. Try the exercise
- General Incident Reporting The Article 23 clock (24-hour warning, 72-hour notification, one-month report), so front-line staff start the chain straight away. Try the exercise
- Reporting Culture No-blame reporting for Article 21(2)(b) incident handling, with figures authorities recognise. Try the exercise
- Third-Party App OAuth Risks For procurement and engineering: supply chain security under Article 21(2)(d) and system acquisition under 21(2)(e). Try the exercise
- Verification Procedures For IT and help desk under Article 21(2)(i): calling back and using code words to stop vishing and MFA-reset pretexts. Try the exercise
- Joiner-Mover-Leaver Awareness Fixes the Article 21(2)(i) gap audits cite most: setting up and removing access properly. Try the exercise
- Encryption & Lock Discipline For Article 21(2)(j) cryptography: the daily device locking and removable media habits policy relies on. Try the exercise
Further reading
Related glossary terms
References
- Directive (EU) 2022/2555 (NIS2) EUR-Lex
- NIS2 Directive policy page European Commission
- NIS Directive (new) ENISA
- NIS 2 Law Centre for Cybersecurity Belgium (CCB)
- National Cybersecurity Coordination Centre NCC-EU
Train the board before the inspector asks
Management-body and staff tracks, with an export for your national authority.
Frequently asked questions
What is NIS2 security awareness training?
NIS2 (Directive (EU) 2022/2555) makes cybersecurity training a named technical and organisational measure for essential and important entities across the EU. Article 20 holds management body members personally liable for the program. Penalties run to EUR 10 million or 2% of global turnover for essential entities, with national competent authorities now scoping their first inspections.
What is NIS2 Article 21(2)(g)?
Article 21(2)(g) of Directive (EU) 2022/2555 (NIS2) requires every essential and important entity to implement "basic cyber hygiene practices and cybersecurity training" as one of ten minimum cybersecurity risk-management measures. It is the article auditors cite first when they sample a training program.
The directive does not prescribe a curriculum. The burden of demonstrating the program is proportionate to the risk and to the size of the entity sits with the entity. National competent authorities sample completion records, content scope, and refresh cadence during inspections.
Does NIS2 require security awareness training?
Yes. NIS2 makes cybersecurity training a named technical and organisational measure under Article 21(2)(g) for the workforce, and Article 20 separately requires members of the management body to follow training that gives them enough knowledge to identify risks and assess practices.
Training that reaches general staff but skips the management body fails Article 20. Training that addresses leadership but not the workforce fails Article 21(2)(g). A compliant program covers both layers and documents completion separately for each.
Who counts as essential vs important under NIS2?
Essential entities are large organizations in sectors including energy, transport, banking, financial market infrastructure, healthcare, drinking water, wastewater, digital infrastructure (DNS, TLD registries, cloud, data centres), ICT-managed services, public administration, and space. Important entities are medium-sized organizations in those sectors plus postal and courier, waste management, chemicals, food, manufacturing of medical devices, computers, electronics, machinery, motor vehicles, transport equipment, digital providers (online marketplaces, search engines, social networks), and research.
Size thresholds follow EU Commission Recommendation 2003/361/EC. Essential entities are typically 250+ employees or EUR 50M+ turnover; important entities are 50+ employees or EUR 10M+ turnover or balance sheet EUR 43M+. Sector-specific overrides catch some smaller entities including trust service providers, TLD registries, DNS providers, and public electronic communications providers regardless of size.
What does "cyber hygiene" mean in NIS2?
Cyber hygiene in the Article 21(2)(g) sense is the everyday set of practices the workforce needs to keep the systems they touch safe. ENISA guidance and national competent authority frameworks generally read this as phishing recognition, password and credential hygiene, mobile and removable media discipline, lock and encryption habits, incident reporting reflexes, and access control basics.
The framing is deliberately practical. Training that teaches policy in the abstract without rehearsing the behaviour does not meet the Article 21(2)(g) bar in the way most national competent authorities now interpret it.
Are management body members personally liable under NIS2?
Yes. Article 20 requires the management body of each essential and important entity to approve the cybersecurity risk-management measures and to oversee their implementation. The same article makes management body members personally liable for infringements of that duty. National competent authorities can publicly disclose infringements and temporarily prohibit named individuals from exercising managerial functions.
The liability regime is structural, not symbolic. It is one of the most significant changes from the 2016 NIS Directive, and it is the reason a NIS2 program needs a dedicated management body training track with its own completion record.
What evidence do national competent authorities look for?
Granular records: who completed which module, when, what content the module covered, what role the learner holds, and how the module maps to a specific Article 21(2) measure. Auditors and competent authorities sample the records, they do not trust dashboard summaries.
Programs that ship per-learner, per-role, per-module export packs with policy acknowledgment timestamps and scenario-pass evidence respond to inspections in hours. Programs that have to assemble the evidence after the request lands tend to spend days, sometimes weeks, on the same response.
How does NIS2 affect supply chain training?
Article 21(2)(d) requires entities to manage supply chain security including direct suppliers and service providers. Training has to reach the procurement, engineering, and security teams that touch supplier onboarding, OAuth integration, vendor verification, and payment-instruction changes.
Third-party app OAuth risks, invoice and payment fraud, and verification procedures exercises cover the supply chain attack surface most national competent authorities flag in their first audit cycles. Generic phishing content alone does not satisfy the supply chain measure.
Does NIS2 require EU-only hosting for the training platform?
NIS2 itself does not mandate where a training platform is hosted, but the Article 21(2)(d) supply chain measures and several national implementations push essential entities toward vendors that can prove data location and isolation.
RansomLeak answers that with an EU region (Ireland) for the Cloud LMS, a dedicated private cloud in the EU, or an on-premises edition for operators of critical infrastructure that keep training data inside their own network.
What is the timeline for NIS2 enforcement in 2025-2026?
The 17 October 2024 transposition deadline passed and the picture has split. Belgium (NIS 2-Wet / Loi NIS 2, in force 18 October 2024, CCB) and Italy (Decreto Legislativo 138/2024, in force 16 October 2024, ACN) transposed on time. Germany joined the in-force group with the NIS2UmsuCG, passed by the Bundestag on 13 November 2025 and binding from 5 December 2025 under BSI supervision of roughly 29,500 entities. The Netherlands Cyberbeveiligingswet cleared the Tweede Kamer on 15 April 2026 and is expected to enter force in Q2 2026 after Senate review.
France, Spain, and Ireland are still not transposed: France is waiting on the loi resilience cyber (NIS2 + REC + DORA) with a full National Assembly vote expected in the July 2026 extraordinary session, Spain’s Ley de Coordinacion y Gobernanza de la Ciberseguridad remains in the legislative pipeline despite urgent status, and Ireland’s National Cyber Security Bill is still in pre-legislative scrutiny. The European Commission sent letters of formal notice in November 2024 and reasoned opinions to 19 Member States on 7 May 2025, with referrals to the Court of Justice now the next step for laggards. First inspection cycles are operational where the law is in force.