ISO 27001 security awareness training
ISO/IEC 27001:2022 splits awareness across Clause 7.2 competence, Clause 7.3 awareness and Annex A control 6.3, and a certification auditor checks all three.
Five-to-ten-minute 3D exercises mapped to each ISO 27001 duty, with completion evidence your auditor can export.
At a glance
- Edition
- ISO/IEC 27001:2022, with Annex A cut from 114 to 93 controls
- Annex A control
- 6.3 Information security awareness, education and training
- Always mandatory
- Clauses 7.2 and 7.3, outside the Statement of Applicability
- Transition
- 2013 certificates lapsed on 31 October 2025
Trusted by teams at





Founded by the creator of Kontra Application Security Training.
Play the exercises behind your ISO 27001 program
Each one is a 3D scenario your staff finish in 5 to 10 minutes. Pick one and play it here, with no sign-up.
Exercises run in interactive 3D environments.
Three requirements, one awareness program
The clauses bind every certified ISMS. Annex A 6.3 comes in through your Statement of Applicability, and almost nobody excludes it.
- Clause 7.2 Competence Define the competence each role needs, close the gaps and keep documented evidence.
- Clause 7.3 Awareness People know the policy, their part in the ISMS and what non-conformity leads to.
- Annex A 6.3 Awareness, education and training Regular training relevant to the job, updated when policies and procedures change.
Surveillance audits revisit this every year; recertification comes round every three.
Annex A and clause requirements, mapped to exercises
Controls a certification body samples at stage 2, linked to the exercises that produce the evidence.
A.6.3 Information Security Awareness A.5.10 Acceptable Use of Assets A.8.3 Access Restriction A.5.24 Incident Management A.8.7 Malware Protection A.5.14 Information Transfer A.5.23 Security for Cloud & AI Services A.8.25 / A.8.28 Secure Development & Coding A.8.9 Configuration Management Clause by clause, what the standard asks of awareness
Read clause by clause, the way a stage 2 auditor walks it.
01 ISMS scope and Statement of Applicability
The ISMS scope statement says which business units, sites, services and systems sit inside the certificate. The Statement of Applicability (SoA) lists every Annex A control, marks it applicable or not, and justifies each exclusion.
A.6.3 is almost never excluded, because every ISMS has people in it. The SoA is the auditor’s map of what to test and what to ask for.
Training evidence has to cover everyone inside the documented scope, not only head office.
02 Annex A 6.3 plus Clauses 7.2 and 7.3 control hierarchy
Clause 7.3 (awareness) applies to everyone working under the organisation’s control. Each person must know the policy, how they contribute, and what happens if they do not conform.
Clause 7.2 (competence) goes further for roles that depend on specific skills: security engineers, administrators, developers and incident responders.
Annex A 6.3 is the control that delivers both: a written program with content, a schedule, role assignments and kept records. The auditor follows the thread from policy to SoA to program, then checks individual employees.
03 Role-based competence by job function
ISO 27001 does not prescribe content. It requires training that fits the role and competence that can be checked.
In practice that means a baseline for everyone (policy acknowledgment, phishing, acceptable use, incident reporting) plus modules for roles with more at stake:
- Finance and AP: invoice fraud and BEC.
- Engineering: secure coding and access management.
- Help desk: vishing and MFA reset pretexts.
- Executives: whaling and deepfake video.
Document the mapping, often as a RACI matrix tied to the SoA, so the auditor can see why each role gets what it gets.
04 Documented evidence pack for the certification body
“We ran the training” is not evidence. The auditor wants the person, the module, the completion date, the score where there is one, and the signed policy acknowledgment.
A typical pack holds:
- the program plan and role assignment matrix
- an LMS export of completion across the certified scope
- phishing simulation results
- campaign material such as newsletters, posters and town-hall slides
- a register of joiner and contractor onboarding
It has to cover the whole audit period: 12 months for surveillance, 3 years for recertification.
05 Audit cycle from Stage 1 readiness to recertification
Stage 1 is a readiness review. The auditor reads your documentation, confirms the ISMS exists on paper and flags gaps.
Stage 2 is the certification audit, on site or remote, sampling evidence across all clauses and applicable Annex A controls, A.6.3 included.
A pass gives a three-year certificate. Surveillance audits in years one and two sample a subset of controls, and A.6.3 is nearly always in it. Year three is a full recertification. An awareness finding that opens at Stage 2 and is not fixed comes back at surveillance and can block recertification.
06 The 27001:2022 transition and what changed for awareness
The 2013 edition put awareness training at A.7.2.2, under human resource security.
The 2022 edition moved it to A.6.3 in the people controls and made the program requirement explicit: plan it, establish it, implement it, maintain it, and update it regularly in line with the security policy and the topic-specific policies.
The deadline to move off 27001:2013 was 31 October 2025, and certificates against the old edition are no longer valid. Even if you have transitioned, check that the SoA and program documents cite A.6.3, not A.7.2.2.
07 Keeping the Statement of Applicability traceable
ISO 27001 auditors look at whether training resembles real work, not how many modules you have. A recorded video and a click-through quiz produce a record, but not proof that someone can apply the policy under pressure.
Each exercise puts the learner in a simulated inbox, vendor portal, call or video meeting and asks for a decision judged against the policy.
When the auditor asks how you keep training current with threats, as A.6.3 requires, you show scenarios mapped to threats and behaviour data, not a slide deck from three years ago.
Assignments follow the SoA trail the auditor walks.
Everyone inside the ISMS scope gets the baseline, including contractors and third parties who hold an account or handle information assets. Roles with elevated controls get more:
- Finance and AP: invoice fraud, BEC and deepfake wire requests.
- Engineering: secure coding and AI prompt injection.
- IT and help desk: vishing and MFA reset pretexts.
- Executives and assistants: whaling and deepfake video.
Joiners and movers get the right set automatically in their first week. The assignment matrix exports as Clause 7.2 evidence.
The export follows the certification body’s checklist. Records with name, module, date, score and signed acknowledgment flow into Cornerstone, Workday Learning, Docebo, SAP SuccessFactors or any standards-based LMS through SCORM 1.2 and 2004.
Coverage by role, refresh cadence and phishing report rate export as the summaries surveillance auditors review. The result is a Clause 7 and A.6.3 pack that survives sampling at any site in scope.
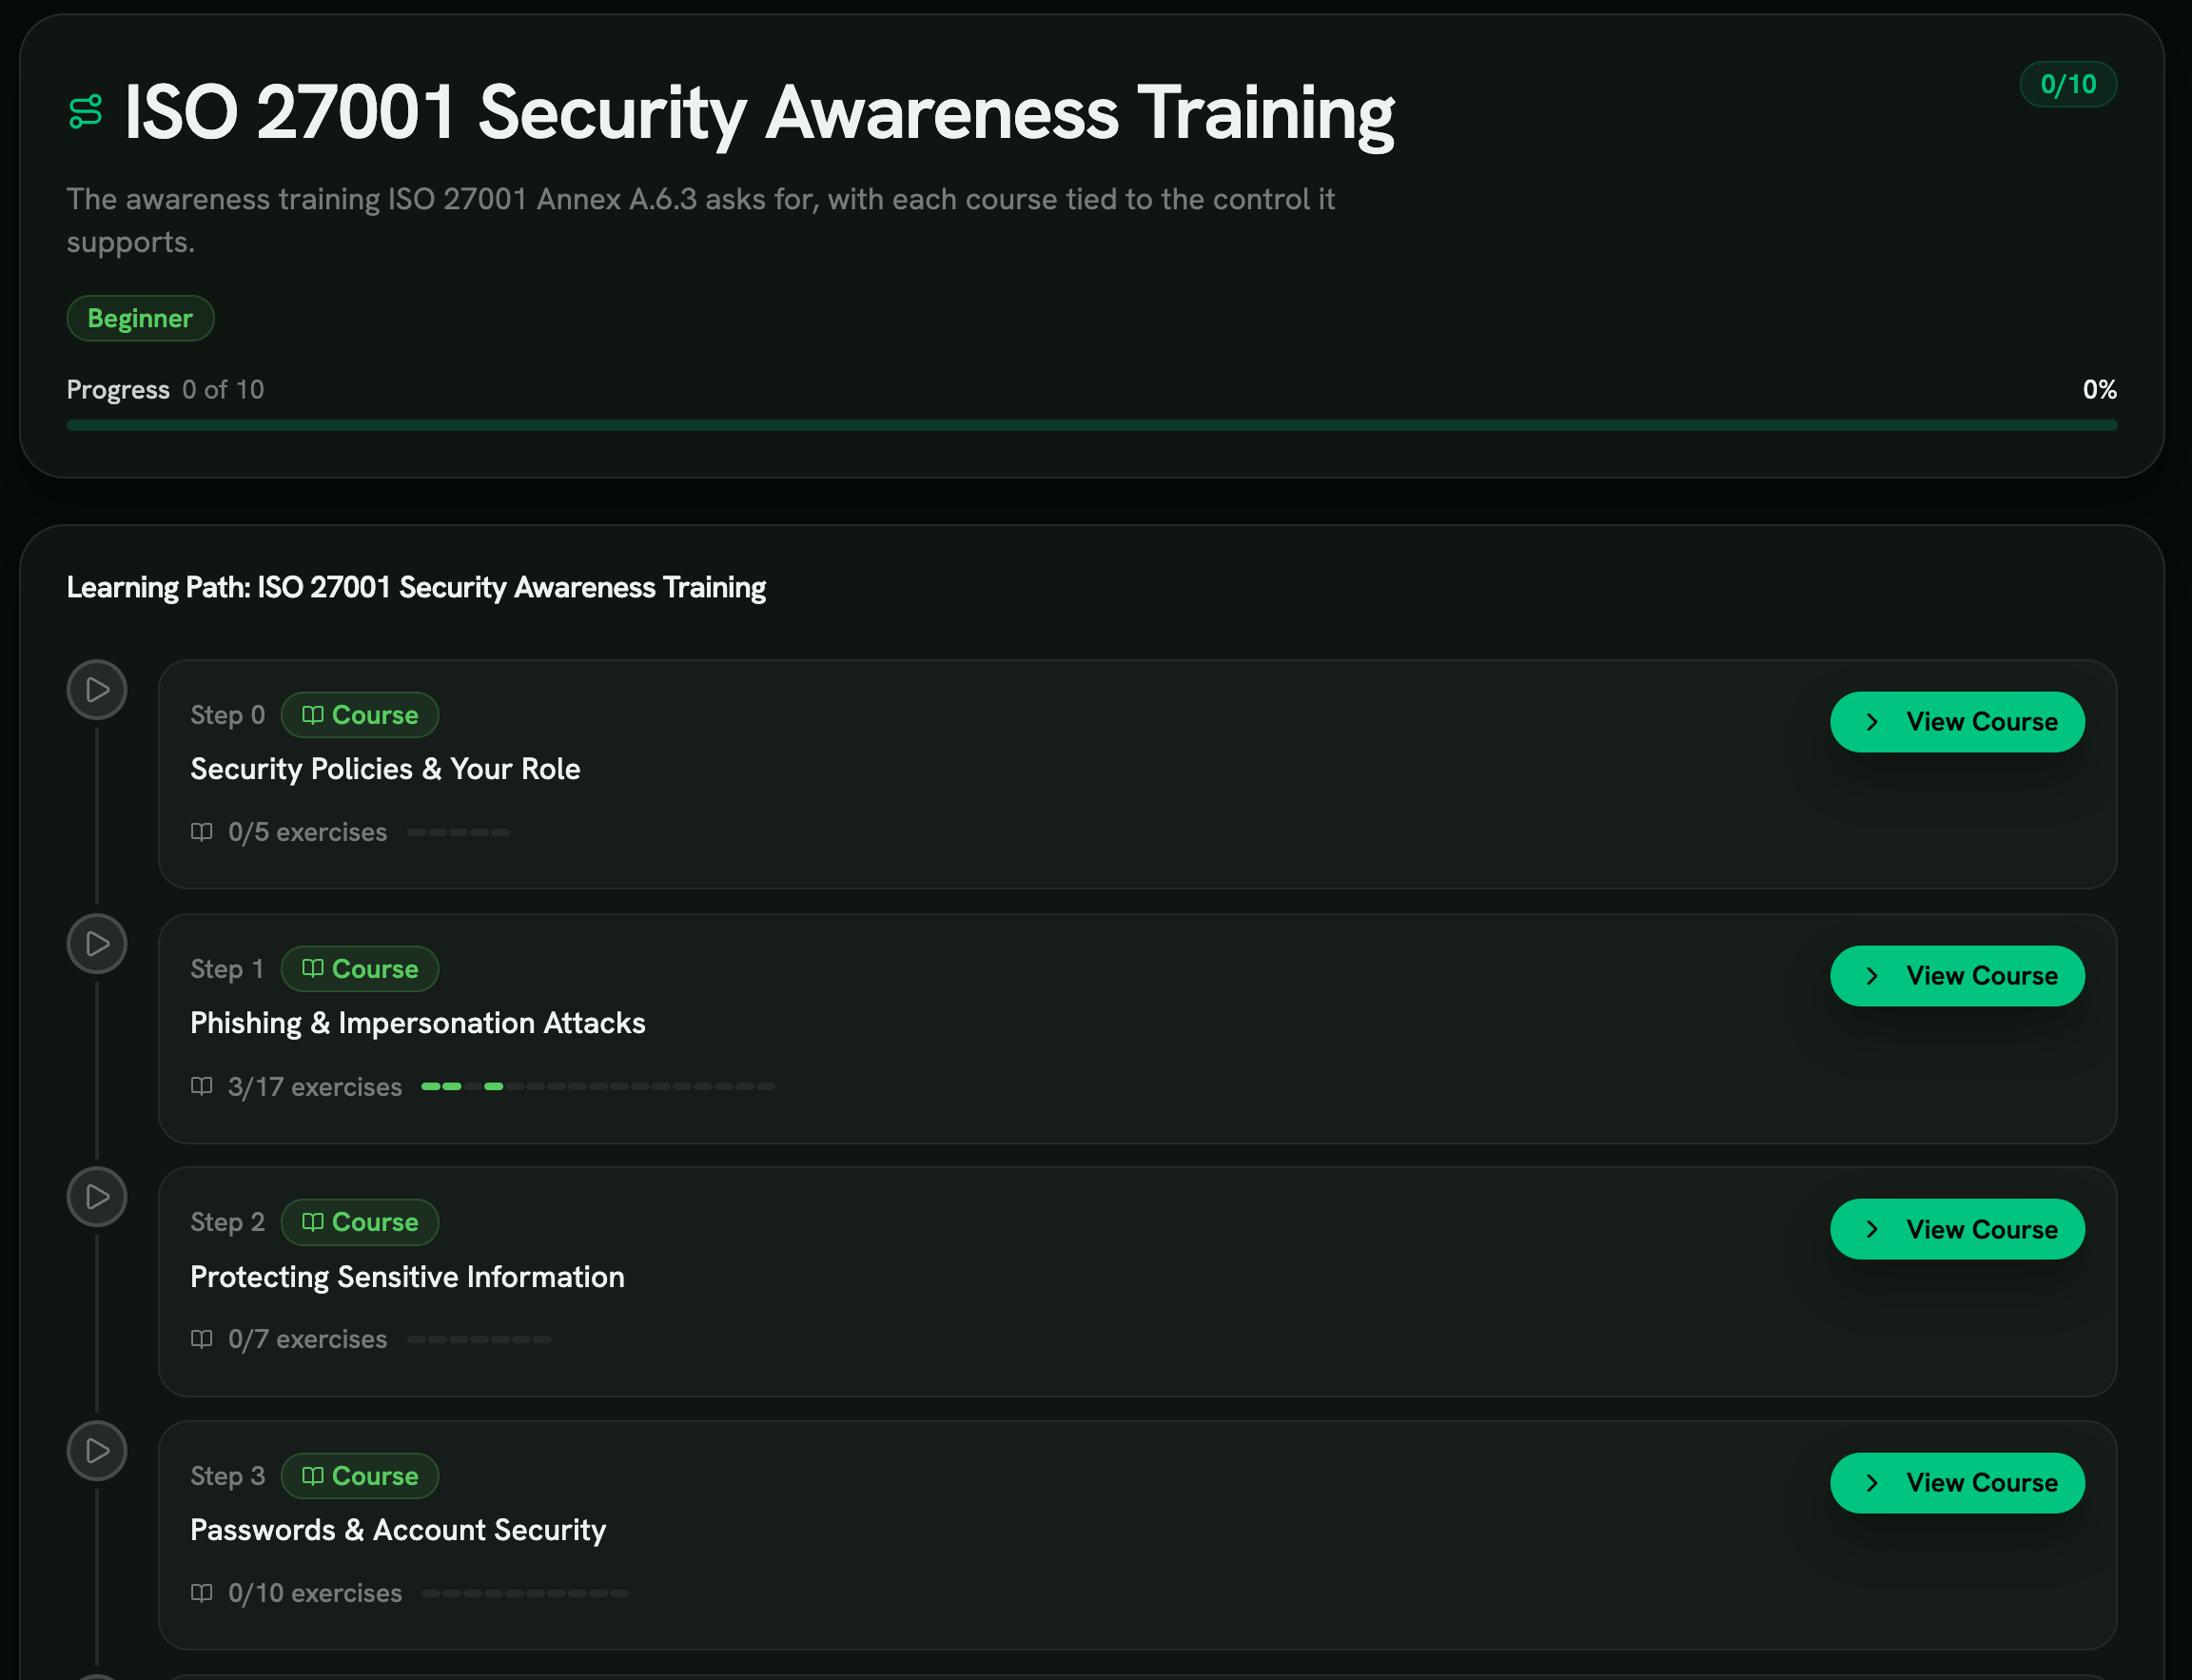
A path that follows Annex A
Ten courses, each tied to the control it evidences: A.6.3 awareness first, then A.5.10 through A.8.7.
- A.6.3 at the core
- The awareness control runs through every step, not just the first one.
- Policy to practice
- A.5.10 acceptable use and A.6.7 remote working sit next to phishing and passwords.
- Ready for the SoA
- Each step names the Annex A control, so the Statement of Applicability writes itself.
Recommended exercises
Baseline for everyone in the ISMS scope, role modules where the SoA marks elevated risk.
- ISMS Policy Awareness Clause 7.3 evidence: the learner reads and acknowledges the security policy, creating the named record auditors sample. Try the exercise
- Employee Security Responsibilities Covers each person’s contribution to the ISMS under Clause 7.3, framed by role to support Clause 7.2. Try the exercise
- Phishing Fixes the most common A.6.3 finding at recertification: no phishing scenarios and no reporting figures. Try the exercise
- Spear Phishing Targeted phishing for executives, finance and engineering, giving the role-specific Clause 7.2 competence auditors expect. Try the exercise
- Invoice & Payment Fraud For finance and AP, linking A.6.3 awareness to the financial controls in your SoA. Try the exercise
- Security Incident Response Supports A.5.24: proof that staff can escalate, preserve evidence and help the response team. Try the exercise
- Least Privilege Awareness The people side of A.8.3: a policy means little if staff ask for more access than they need or keep old access after moving roles. Try the exercise
- Joiner-Mover-Leaver Awareness Closes the access lifecycle gap surveillance auditors often find, with proof staff understand joiner-mover-leaver and confirm offboarding. Try the exercise
The Annex A controls a trained workforce keeps working
Other Annex A controls that depend on the same people.
A.6.3: Information security awareness, education and training program
Learners work through scenarios tied to your policy, your SoA and current attacks. Each completion is recorded with a score and timestamp and exported to your LMS or GRC tool.
The program runs all year rather than once, which meets the control’s “updated regularly” wording and gives you fresh evidence for every surveillance audit.
Clause 7.3: Awareness of policy, contribution, and nonconformity
ISMS Policy Awareness and Employee Security Responsibilities cover the three things Clause 7.3 names: the security policy, each person’s contribution to the ISMS, and what non-conformance means.
Their completion records are the Clause 7.3 evidence auditors sample.
Clause 7.2: Competence for roles affecting information security
Each job family is mapped to the modules its competence depends on. Engineers get secure coding and access management, finance gets invoice fraud and BEC, and the help desk gets vishing and MFA reset pretexts.
The mapping is written down, and the per-role evidence gives the auditor the Clause 7.2 trail they look for.
A.5.10: Acceptable use of information and other associated assets
The Internet & Email Acceptable Use exercise tests the policy in real situations: shadow IT, personal devices, moving sensitive documents, and outright misuse.
Its completion record shows staff were trained on the rules they are held to.
A.5.14: Information transfer
Secure Messaging Practices and Cloud Sharing Controls cover secure transfer. Learners decide which channel suits which class of data, how to share files externally without breaking the SoA, and how to use chat tools without leaking confidential material.
Both exercises add a record per employee to the audit pack.
A.5.24: Information security incident management planning and preparation
The Security Incident Response exercise puts learners in a live incident. They spot the signal, escalate through the right channel, preserve evidence and support the response team.
The control expects you to plan, prepare and train for incidents. One exercise gives you evidence for all three.
A.8.7: Protection against malware
The Phishing, Spear Phishing, Double Barrel Phishing and Ransomware exercises cover the human side of malware: how payloads arrive by email and chat, how to spot and report the lure, and what to do after a click.
Together with your EDR, that covers the part of A.8.7 that depends on people.
A.8.3: Information access restriction (least privilege and JML)
Least Privilege Awareness and Joiner-Mover-Leaver Awareness train people to ask only for the access they need, give it back when their role changes, and confirm offboarding is done.
That evidence supports both A.8.3 and A.5.18 in the SoA.
Nonconformities certification bodies raise on Annex A 6.3
Findings that show up in surveillance audits, and the breaches behind them.
Stage 2 audit failure on missing per-employee training records
A common Stage 2 failure: the organisation shows an awareness deck and an LMS dashboard reading 92% completion. The auditor picks 15 people from the HRIS, including 3 contractors hired in the last 90 days and 2 staff from a recently acquired subsidiary.
Two contractors have no training record. One acquisition employee never signed the policy. That opens a minor nonconformity against Clause 7.3 and A.6.3, with 60 days to fix it.
No certificate is issued until the corrective action is accepted, which usually delays RFPs, vendor onboarding and renewals that wait on the ISO 27001 logo.
Surveillance audit major on missing role-based training for new joiners
A second-year surveillance pattern: the auditor samples a year of joiners and finds engineers got the baseline module but nothing on secure coding or access management. Yet the SoA marks A.8.28 (secure coding) and A.5.18 (access rights) as applicable.
Because the gap is systemic and the role is critical, the auditor raises a major nonconformity. The organisation cannot show Clause 7.2 competence for people whose work affects security.
A major nonconformity needs an accepted corrective action before the certificate continues. In the worst case the certificate is suspended until a special audit.
Recertification setback when phishing-specific exercises are absent
A recertification pattern: the program covers policy, acceptable use and incident reporting. The auditor asks how it deals with phishing, the most common way in, and finds no phishing exercises, no simulation results and no reporting figures.
The auditor points to A.6.3’s requirement to keep the program current with relevant threats. The finding asks for a phishing program with role-based scenarios and tracked results.
Recertification is not blocked outright, but there are 90 days to deliver a corrective action plan. Missing that puts the certificate, and the contracts that depend on it, at risk.
Further reading
Related glossary terms
References
- ISO/IEC 27001:2022 Information security management systems International Organization for Standardization
- ISO/IEC 27002:2022 Information security controls International Organization for Standardization
- ISO/IEC 27001 Information security management BSI Group
- ISO/IEC 27001 standard guidance European Union Agency for Cybersecurity (ENISA)
- Cost of a Data Breach Report 2024 IBM Security
Take Annex A 6.3 off the nonconformity list
Role-based modules and a register mapped to your Statement of Applicability.
Frequently asked questions
What is ISO 27001 security awareness training?
ISO 27001:2022 names security awareness as Annex A control 6.3 and ties it to two mandatory ISMS clauses on competence and awareness. Certification bodies want per-employee, role-based evidence on a three-year cycle, and the most common nonconformity in the entire standard sits in this control area.
What is ISO 27001 Annex A 6.3?
Annex A 6.3 is the ISO 27001:2022 control titled "Information security awareness, education and training." It requires the organization to plan, establish, implement, and maintain an awareness, education, and training program for all employees, and to update it regularly in line with the information security policy and relevant topical policies.
It replaces the 2013 standard's A.7.2.2 control, which sat inside the Human Resource Security domain. The 2022 control sits inside the People controls theme and elevates the operational program from a paragraph in HR security into a named, separately auditable Annex A control.
Does ISO 27001 require security awareness training?
Yes, in three places. Clause 7.3 (Awareness) requires that every person doing work under the organization's control is aware of the information security policy, their contribution to ISMS effectiveness, and the implications of not conforming. Clause 7.2 (Competence) requires documented competence for roles whose work affects information security performance. Annex A 6.3 is the operational control that delivers both.
An auditor will check that the program exists, that it covers the people inside the ISMS scope (including contractors and third parties holding accounts), and that per-employee evidence is retained. Missing any of the three opens a nonconformity finding.
How often does ISO 27001 awareness training need to be refreshed?
The standard does not prescribe a fixed cadence. The control text in A.6.3 says the program must be updated "regularly," which auditors interpret in light of the information security policy, the threat landscape, and the topical policies referenced in the SoA. In practice, certification bodies expect at minimum an annual refresh for all staff plus event-driven updates when a new threat or policy change makes existing content out of date.
Best-in-class programs run continuously, with monthly role-based exercises and quarterly all-staff campaigns. The continuous model produces fresher evidence for every surveillance audit and reduces the nonconformity risk from the "updated regularly" clause.
What evidence do ISO 27001 auditors look for?
Auditors sample evidence at the employee level. The standard pack includes the awareness program plan, the role-based assignment matrix, signed policy acknowledgments, per-employee completion records (name, module, date, assessment score), phishing simulation results, awareness-campaign artifacts (newsletters, posters, town-hall slides), and a register of new joiner and contractor onboarding completions.
The pack has to cover the full audit period: 12 months for surveillance audits and 36 months for recertification. Aggregate completion rates do not satisfy the requirement. The auditor will sample named individuals across the ISMS scope, including contractors, third parties, and recent acquisitions, and ask for the records.
How does ISO 27001 training evidence differ between Stage 1, Stage 2, and surveillance audits?
Stage 1 is a documentation review. The auditor confirms that the awareness program is documented, that it covers Annex A 6.3 and Clauses 7.2 and 7.3, and that the role-based assignment matrix exists. Findings at Stage 1 are usually around documentation gaps rather than evidence gaps.
Stage 2 is the certification audit. The auditor samples per-employee records across the full ISMS scope, tests the policy acknowledgment process, and validates that the program runs as documented. This is where most awareness-related nonconformities open.
Surveillance audits in years 1 and 2 sample a subset of controls. A.6.3 is almost always included because it is the most commonly failed control area in the entire standard. Recertification in year 3 is a full audit again, with the same scope as Stage 2.
What changed for awareness training between 27001:2013 and 27001:2022?
The 2013 standard listed awareness as control A.7.2.2 inside the Human Resource Security domain. The 2022 standard moved it to A.6.3 inside the new People controls theme and rewrote the control text to make the program requirement explicit: planned, established, implemented, maintained, and updated regularly in line with the information security policy and relevant topical policies.
The transition deadline from 27001:2013 closed on 31 October 2025. Organizations operating against an old certificate after that date are no longer ISO 27001 certified. The SoA, the program documentation, and the audit evidence pack all need to reference A.6.3, not the legacy A.7.2.2.
Do contractors and third parties need ISO 27001 training?
Yes. Clause 7.3 applies to "all persons doing work under the organization's control," which extends to contractors, agency staff, and third parties wherever they hold an account or handle information assets inside the ISMS scope. The contracting model does not reduce the requirement; the organization remains accountable for the awareness evidence.
Practical implementation usually assigns the baseline awareness module to every contractor on day one, with a signed policy acknowledgment, and tracks completion in the same LMS or GRC system that holds the employee records. Auditors sample contractor records on the same basis as employees, so missing one contractor is the same finding as missing an employee.
How does ISO 27001 awareness training compare to SOC 2 CC1.4?
Both frameworks require a documented, role-based, per-employee awareness program. The depth of evidence is similar, and the same training program usually satisfies both with shared evidence packs. The differences are in audit mechanics: SOC 2 is a US AICPA attestation with annual Type 2 cycles, while ISO 27001 is an international ISO standard with three-year certification cycles and accredited certification bodies.
For organizations pursuing both, the practical pattern is to design the awareness program against ISO 27001 A.6.3 (the more prescriptive control) and map the evidence pack to SOC 2 CC1.4 as a secondary view. The same training records, role-based assignments, and policy acknowledgments support both audits.