EU AI Act security awareness training
Article 4 of the EU AI Act has applied since 2 February 2025. Since the Digital Omnibus it asks every provider and deployer to take measures that support their staff's AI literacy.
Five-to-ten-minute 3D exercises mapped to each EU AI Act duty, with completion evidence your auditor can export.
At a glance
- Regulation
- (EU) 2024/1689, in force since 1 August 2024
- Literacy duty
- Article 4, applicable since 2 February 2025
- Reworded
- By the Digital Omnibus, Regulation (EU) 2026/1744, on 27 July 2026
- Top fine
- €35M or 7% of turnover, for prohibited practices
Trusted by teams at





Founded by the creator of Kontra Application Security Training.
Play the exercises behind your EU AI Act program
Each one is a 3D scenario your staff finish in 5 to 10 minutes. Pick one and play it here, with no sign-up.
Exercises run in interactive 3D environments.
The dates that set your training calendar
Obligations switch on in stages, and each stage adds people who need to know more.
- 1 Aug 2024 Entry into force The regulation is published and the clock starts.
- 2 Feb 2025 Literacy and bans Article 4 AI literacy and the Article 5 prohibitions apply.
- 2 Aug 2025 GPAI and penalties General-purpose AI rules, the AI Office and national penalties.
- 27 Jul 2026 Digital Omnibus Article 4 reworded to “take measures to support” literacy.
- 2 Dec 2027 Annex III high-risk Human oversight and deployer duties for listed high-risk uses.
- 2 Aug 2028 Annex I products High-risk AI built into regulated products.
Article 4 and the deployer duties, mapped to exercises
Each row is a duty a national authority can ask about, with the exercises that build the literacy behind it.
Art. 4 AI Literacy Requirement Art. 5 Prohibited AI Practices Art. 10 Data Governance (High-Risk AI) Art. 14 Human Oversight Art. 16 / 26 Provider & Deployer Obligations Art. 27 Fundamental Rights Impact Assessment Art. 50 Transparency & Disclosure Art. 51-56 General-Purpose AI Models Art. 73 Serious Incident Reporting Art. 99 Penalties & Enforcement Recommended exercises
From prompt hygiene for every user to oversight drills for named operators.
- AI Literacy Essentials The Article 4 baseline: what AI is, how the systems at work behave, where they fail, and the daily habits the literacy duty expects of every employee and contractor. Try the exercise
- Prohibited AI Practices The eight Article 5 bans, and escalating any purchase, build or rollout that crosses one, given the €35M or 7% penalty tier. Try the exercise
- AI Risk Classification For legal, risk, product and engineering: the prohibited, high-risk (Annex III), limited-risk and minimal-risk classes, and what each one requires. Try the exercise
- Provider vs. Deployer Responsibilities Which duties belong to providers under Articles 9 to 22 and which to deployers under Article 26, the most common point of confusion in AI vendor contracts. Try the exercise
- Meaningful Human Oversight The Article 14 module for named overseers of high-risk systems: capabilities, limits, automation bias, and when to override or ignore the output. Try the exercise
- High-Risk AI Deployer Obligations Article 26 for deployer-side staff (oversight, input data, monitoring, logs, informing workers, stopping use, reporting incidents) ahead of the 2 December 2027 date the Digital Omnibus set for Annex III systems. Try the exercise
- Fundamental Rights Impact Assessment The Article 27 assessment public bodies and operators of certain high-risk systems must complete and send to the market surveillance authority before first use. Try the exercise
- AI Transparency and Disclosure The Article 50 module: chatbot disclosure, notice for emotion recognition and biometric categorisation, deepfake labels, and machine-readable marking of GPAI output. Try the exercise
- AI Support Chatbot Scam Article 50 chatbot disclosure from the user’s side: a fake AI support chat, reached from a sponsored search result, that asks for a one-time code. Try the exercise
- Shadow AI Tools Everyday Article 4 literacy: a whiteboard photo uploaded to a free consumer AI app, the approved-tool list, and reporting the upload. Try the exercise
- Unapproved AI Notetakers An AI notetaker joins a confidential HR meeting and posts a public recap link, the kind of unapproved tool Article 4 expects staff to spot. Try the exercise
- Prompt Injection in Documents Hidden text in a PDF steers an AI summary. Staff learn this limit of the system and to check the source, as Article 4 literacy calls for. Try the exercise
- What Counts as AI Applies the Article 3 definition to a team’s everyday tools, using inference rather than automation as the test, and names the provider and deployer of each. Try the exercise
- Labeling AI and Deepfakes The Article 50 deployer check on a campaign: deepfakes of real places and events, the lighter rule for satire, where the label goes, and a request no label can fix. Try the exercise
- Using AI Within the Law The Article 26 duty to tell workers before AI ranks them, and the Article 5 ban on emotion recognition at work, within one ordinary working day. Try the exercise
- When AI Use Goes Wrong Maps a hiring shortcut to the Article 99 tiers, separates company fines from what happens to staff, and shows how a quick report changes the outcome. Try the exercise
One path built for Article 4
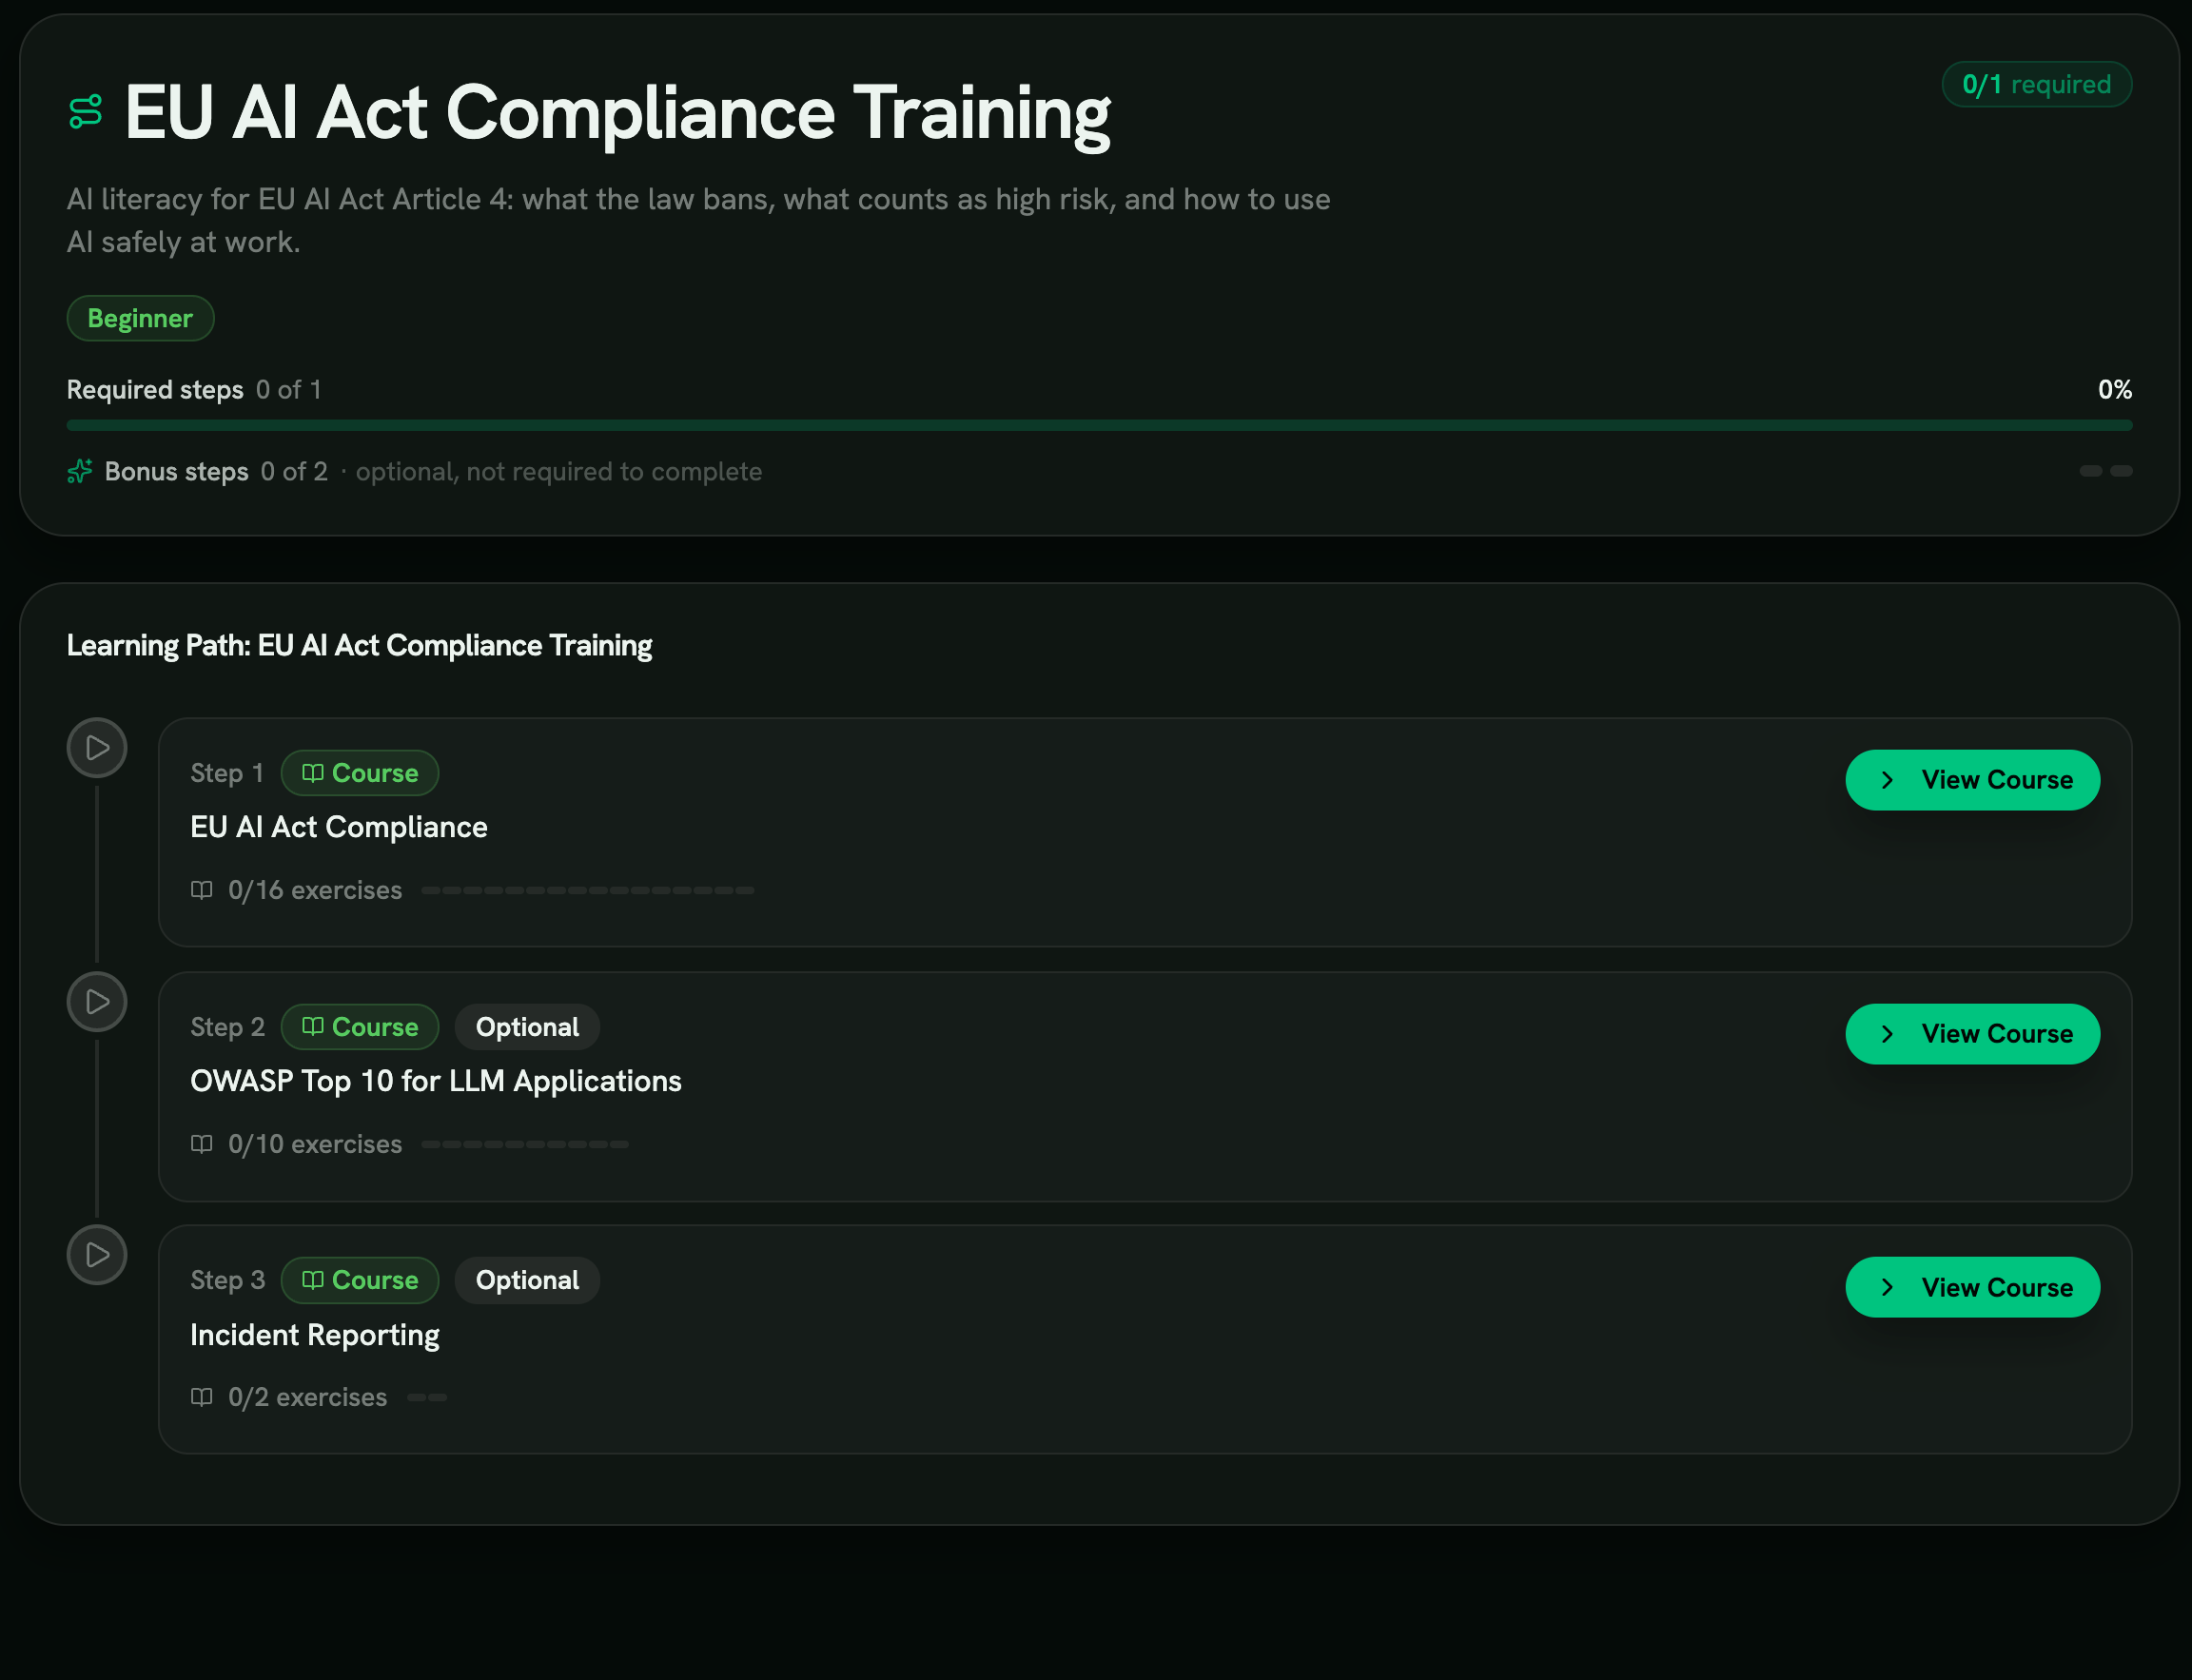
The EU AI Act Compliance Training path: one required course, two optional ones for the people who build or run AI.
- EU AI Act Compliance
- The required course: 16 exercises on risk tiers, prohibited practices and human oversight.
- OWASP Top 10 for LLMs
- Optional for developers and AI operators who need the attack side.
- Incident reporting
- Optional, so teams know what to escalate under Article 73.
What Article 4 asks for, and who counts as staff
What Article 4 asks for now, and what the high-risk duties will add.
01 Scope: provider, deployer, importer, or distributor
The Act defines four roles, each with different duties:
- Provider: develops an AI system, or has one developed, and puts it on the EU market under its own name or trademark.
- Deployer: uses an AI system under its authority at work, such as a bank running a credit-scoring model, a hospital using a triage tool, or a recruiter screening CVs with an AI shortlister.
- Importer: brings an AI system from outside the EU onto the EU market.
- Distributor: makes it available without changing it.
Most companies deploy many systems and provide a few. The Article 4 literacy duty applies equally to providers and deployers.
02 Article 4: the AI literacy duty, amended in July 2026
Article 4 requires providers and deployers to take measures that support their staff’s AI literacy, taking into account their technical knowledge and the context the systems are used in.
The duty first applied on 2 February 2025. From 27 July 2026 the Digital Omnibus replaced the original wording, which asked for a “sufficient level” of literacy.
The AI Office’s Living Repository and its Article 4 Q&A still explain why an ongoing programme, not a single seminar, is the credible way to show those measures.
03 Risk tiers: prohibited, high-risk, limited risk, minimal risk
Article 5 bans eight practices outright.
Annex III lists eight areas where systems are high-risk by default. They carry the heaviest controls in Articles 8 to 27: risk management, data governance, transparency to deployers, human oversight and post-market monitoring.
Limited-risk systems, such as chatbots, emotion recognition, biometric categorisation and deepfakes, carry the Article 50 transparency duties. Minimal-risk systems add nothing beyond Article 4 literacy.
The risk class decides which extra training sits on top of the literacy baseline.
04 Articles 14 and 26: human oversight and deployer obligations
Article 14 requires providers to design high-risk systems so people can oversee them effectively while they run. Article 26 puts the operating side on deployers: oversight must go to people with the competence, training, authority and support to do it.
A bank running a high-risk credit model has to name its overseers, train them on what the model can and cannot do, and give them real power to override it. Expect a national authority to ask for those overseers’ training records first.
05 Article 27: Fundamental Rights Impact Assessment for public-sector and essential-service deployers
Article 27 requires a Fundamental Rights Impact Assessment (FRIA) before first use from public bodies, private operators providing public services, and operators of certain high-risk systems such as creditworthiness and life and health insurance pricing.
The FRIA covers:
- the intended purpose
- how long and how often the system is used
- who is affected
- the specific risks of harm
- human oversight measures
- mitigations
It must be sent to the national market surveillance authority. Preparing one takes real literacy, so legal, risk, product and engineering teams benefit from training before they start.
06 Article 50: transparency for chatbots, deepfakes, and GPAI output
Article 50 covers limited-risk systems and GPAI output:
- Providers of AI that talks to people must tell them it is an AI, unless that is obvious.
- Deployers of emotion recognition or biometric categorisation must tell the people exposed to it.
- Deployers who create or alter image, audio or video that counts as a deepfake must disclose that it is artificial.
- Providers of GPAI models that produce synthetic content must mark it in a machine-readable way.
Each duty means a concrete step or disclosure for staff, so training has to cover them.
07 Article 99 penalties, the EU AI Office, and national competent authorities
National competent authorities enforce the Act. Each member state names at least one notifying authority and one market surveillance authority. The EU AI Office in DG CNECT, Brussels, supervises GPAI directly and coordinates the European Artificial Intelligence Board.
Article 99 sets three penalty tiers:
- up to €35M or 7% of global annual turnover for Article 5 breaches
- up to €15M or 3% for most operator duties, including provider, deployer and transparency obligations
- up to €7.5M or 1% for misleading information
SMEs and start-ups pay the lower of the two amounts, not the higher.
08 Role-based literacy that survives a regulator’s question
The EU AI Act Compliance course has 16 interactive 3D exercises, and the wider catalogue adds more. Together they cover:
- Article 4 baseline: AI Literacy Essentials, Using AI Tools Responsibly at Work, Safe GenAI Usage, Sensitive Data Exposure Through AI.
- Risk classification: AI Risk Classification, Provider vs. Deployer Responsibilities, Prohibited AI Practices, High-Risk AI Deployer Obligations.
- Data and oversight: AI Data Governance, AI Bias and Discrimination, Meaningful Human Oversight, AI and Data Protection.
- Transparency: AI Transparency and Disclosure, General-Purpose AI Model Obligations.
- Assurance: AI Governance in Your Organization, Fundamental Rights Impact Assessment, AI Incident Reporting, EU AI Act Penalties and Enforcement.
Each one puts the learner in a realistic situation, asks for a decision under pressure, and ends with feedback naming the article, the duty and the next practical step.
Article 4 asks you to consider each person’s technical knowledge and how they use AI, so depth varies by role:
- Developers and ML engineers: data governance, bias and provider-side modules.
- People operating AI on the deployer side, such as the analyst running a credit model, the recruiter using a shortlister or the radiologist using a triage tool: deployer duties, human oversight and incident reporting.
- Legal, risk and compliance: the Fundamental Rights Impact Assessment, penalties and enforcement, and governance.
- Executives and the board: a briefing on penalty exposure and how the named authorities enforce.
Staff who use AI but do not build or run it start with the AI Basics for Everyone course. It covers what counts as an AI system, labelling deepfakes, AI under data protection, copyright and employment law, and what misuse costs the company and the person.
Every completion creates a record with the person, role, date, module version, assessment result and SCORM status. The pack is laid out so you can send a national authority or the AI Office individual records for named overseers and a summary for everyone else.
The course is updated as the rules move: when the AI Office issues guidance, when a national authority states its expectations, and as new duties start on 2 December 2027 and 2 August 2028.
How regulators and the AI Office read Article 4 so far
No Article 4 fine has been issued yet, so this is guidance, not case law.
EU AI Office Article 4 guidance and Q&A, published early 2025
In early 2025 the Commission’s AI Office published a Living Repository on AI literacy and a public Q&A on Article 4.
Written for the original wording, the Q&A says “sufficient level” is judged case by case, not against one curriculum. It also says the duty covers staff and contractors at every level, and that providers and deployers should document the literacy measures they take.
The Office has said plainly that one onboarding video does not satisfy Article 4. Organisations share their programme designs in the Living Repository, which now holds working examples from financial services, public administration and large industrial deployers.
National competent authority preparation across France, Spain, Italy, Germany, and the Netherlands
Member states are building supervision as the deadlines arrive.
- Spain created AESIA, based in La Coruña, the first dedicated national AI agency in the EU.
- France has put the CNIL forward as the likely lead authority.
- Italy splits the work between AgID for AI policy and the Garante for privacy-related AI supervision.
- Germany has pointed to the BNetzA, with federal and Länder data protection authorities keeping a role.
- The Netherlands has given the Autoriteit Persoonsgegevens a coordinating role.
Each authority is publishing transitional guidance and taking voluntary submissions under the Commission’s AI Pact. That is the best current guide to what Article 4 documentation will need to show in a formal investigation.
Industry early-mover compliance patterns inside large multinationals
Through 2025, many large multinationals, including banks, insurers, telecoms, industrial groups and professional services firms, rolled out AI literacy programmes ahead of the deeper Article 26 deployer duties. The Digital Omnibus has since moved those duties to 2 December 2027.
The Commission published the EU AI Pact commitments with named signatories, which gives a partial view of who has committed to what.
The usual design has three layers: a baseline for anyone who uses an AI tool at work, a deeper module for people who build or run AI systems, and a module for overseers named under Articles 14 and 26. These early movers treat the literacy record as their main defence in an audit and organise their LMS evidence around it.
From literacy to the high-risk duties
Governance measures that literacy training feeds into.
Article 4: supporting AI literacy across the workforce
The EU AI Act course covers the regulation, the timeline, the four risk tiers and the everyday practices Article 4 expects of staff and contractors who work with AI. Modules ship as SCORM 1.2 and 2004, so completion records land in the LMS an authority will inspect. Content varies by role, which is what Article 4 asks for.
For people who use AI tools every day, the AI at Work course adds workplace scenarios: unapproved AI notetakers, uploads to consumer AI apps, unchecked AI drafts and prompt injection hidden in documents.
The AI Basics for Everyone course starts a step earlier for the whole workforce. Its What Counts as AI exercise teaches the Article 3 definition and whether you are the provider or the deployer of each tool.
Article 5: prohibited AI practices awareness
The Prohibited AI Practices module teaches staff the eight banned categories:
- subliminal manipulation
- exploiting vulnerabilities
- social scoring
- predictive policing based on profiling
- untargeted scraping of facial images
- emotion recognition at work and in education
- biometric categorisation by sensitive traits
- real-time remote biometric identification in public spaces by police
Staff learn to escalate any purchase, build or rollout that crosses the line. These carry the €35M or 7% penalty tier, so this is where training product, procurement and legal teams pays off most.
Article 10: data governance for AI training, validation, and testing data
The AI Data Governance module covers Article 10: relevance, representativeness, accuracy, completeness, checking for bias, and the data preparation choices that shape how a system behaves.
Engineering, data and risk teams learn what to document so the data pipeline holds up before a high-risk system goes live. The same records support the technical documentation duty in Article 11.
Article 14: meaningful human oversight for high-risk AI
The Meaningful Human Oversight module trains the people who will oversee high-risk systems. They learn what the system can and cannot do, how automation bias works, and when and how to override or ignore its output. Under Article 14, oversight needs named people who are trained and allowed to overrule the system.
Each person gets an individual training record, which Article 26 requires deployers to keep.
Article 26: deployer obligations for high-risk AI
The High-Risk AI Deployer Obligations module covers what Article 26 puts on deployers:
- assigning human oversight
- using input data within the provider’s instructions
- monitoring operation
- keeping logs for at least six months
- informing workers
- stopping use if the system threatens health, safety or fundamental rights
- reporting incidents
Provider vs. Deployer Responsibilities sets out which duties sit with which role over the system’s life.
Article 27: Fundamental Rights Impact Assessment workflow
The Fundamental Rights Impact Assessment module covers the assessment public-sector deployers and operators of certain high-risk systems must complete before first use.
Legal, risk, product and engineering teams learn the seven elements it must address, the duty to notify the national market surveillance authority, and how it connects to the GDPR Article 35 DPIA when personal data is involved.
Article 50: transparency, deepfake disclosure, and synthetic content
The AI Transparency and Disclosure module covers the duties toward users: telling people they are talking to an AI, labelling deepfake images, audio and video as artificial, and marking GPAI synthetic content in a machine-readable way. Communications, marketing, product and engineering teams learn the process changes Article 50 requires and the exceptions for artistic, satirical and fictional work and for detecting crime.
The AI Support Chatbot Scam exercise in the AI at Work course shows the chatbot disclosure duty from the user’s side, in a fake support chat that asks for a one-time code.
The Labeling AI and Deepfakes exercise runs the deployer’s label check before a campaign goes live. It covers deepfakes of real places and events, the lighter rule for satire, and why a label never replaces consent.
Article 99: penalty regime awareness for executives and risk owners
The EU AI Act Penalties and Enforcement module shows executives, legal and risk owners the three penalty tiers, the roles of the AI Office and national authorities, the cap for SMEs and start-ups, and what authorities weigh when setting a fine: gravity, duration, intent, cooperation and past infringements. It gives you the executive briefing record most boards now ask for before internal audit and risk committee reviews.
For everyone else, When AI Use Goes Wrong shows who pays for what. The organisation pays the fine, the employee answers to their employer, and a quick, complete report improves the outcome.
Further reading
Related glossary terms
References
- Regulation (EU) 2024/1689 (the AI Act) EUR-Lex (Official Journal of the European Union)
- European AI Office European Commission, DG CNECT
- Regulatory framework for AI European Commission
- Living repository to foster learning and exchange on AI literacy (Article 4) European AI Office
- AI Pact European Commission
Start Article 4 with something people finish
Role-based AI literacy tracks and records ready for the high-risk duties.
Frequently asked questions
What is EU AI Act security awareness training?
EU AI Act training is how organisations meet Article 4 of Regulation (EU) 2024/1689, which obliges every provider and deployer of AI systems used in the European Union to take measures supporting the AI literacy of their staff. The duty applies regardless of risk tier, and the staged penalty regime reaches €35 million or 7% of global annual turnover for the most serious breaches.
What is EU AI Act Article 4 AI literacy?
Article 4 of Regulation (EU) 2024/1689 requires providers and deployers of AI systems to take measures to support the development of AI literacy of their staff, taking into account their technical knowledge and the context the AI systems are used in. That is the wording since the Digital Omnibus took effect on 27 July 2026; the original text asked them to ensure a sufficient level of literacy.
The duty first applied on 2 February 2025 and covers every provider and deployer regardless of risk tier. The EU AI Office Living Repository and Q&A from 2025 still describe credible measures: a documented programme rather than a single onboarding video.
Does the EU AI Act require AI training for all employees?
Article 4 applies to staff and any other person dealing with the operation and use of AI systems on the entity's behalf. In practice that means anyone who uses an AI tool as part of their job, including office productivity assistants, customer-service copilots, code assistants, marketing generators, and any embedded AI in line-of-business software. Article 4 does not require identical depth for everyone; it requires calibration to role.
For most enterprises the practical answer is a baseline literacy module for all staff who touch any AI tool at work, with deeper role-specific modules for developers, deployer-side operators, named overseers under Articles 14 and 26, legal and risk teams, and executives. Article 26 separately requires deployers of high-risk AI systems to ensure that natural persons assigned to oversight have the necessary competence, training, authority, and support.
When did the EU AI Act AI literacy duty start?
The Article 4 AI literacy duty became applicable on 2 February 2025, six months after the regulation entered into force on 1 August 2024, on the same date as the Article 5 ban on prohibited practices. The Digital Omnibus changed its wording from 27 July 2026, but the duty itself still applies.
The other milestones are 2 August 2025 (GPAI model rules, governance chapter, penalty regime, national competent authorities), 2 August 2026 (Article 50 transparency duties and the general date of application), 2 December 2027 (high-risk obligations for the Annex III domains, moved by the Omnibus), and 2 August 2028 (high-risk AI embedded in regulated products under Annex I).
What do AI literacy measures need to cover?
The amended Article 4 sets no benchmark level. It asks for measures that take account of the technical knowledge of the people involved and the context the AI systems are used in, and the EU AI Office Q&A on Article 4 describes the same contextual test. A claims handler using an AI triage tool needs different literacy from the data scientist who built it.
In practice authorities will look for a documented programme rather than a single training event, calibrated by role, refreshed when the regulation or the AI systems change, and supported by evidence that named individuals have completed the modules relevant to their job. The Commission's AI Pact and the Living Repository on AI Literacy give a public bench of programme designs that the AI Office considers acceptable.
Who needs Article 14 human-oversight training under the EU AI Act?
Article 14 applies to providers of high-risk AI systems and requires that those systems be designed and developed so they can be effectively overseen by natural persons during the period in which the AI system is in use. Article 26 puts the operating side of that duty on deployers of high-risk AI systems: assign oversight to natural persons who have the necessary competence, training, authority, and support to do the job.
Practically, every named overseer of a high-risk AI system needs targeted training on the system's capabilities and limitations, on automation bias, on the conditions under which to override or disregard the output, and on the escalation path. The training record for those individuals is the document a national competent authority is most likely to ask for first during an investigation.
What are the EU AI Act penalties?
Article 99 sets a three-tier penalty stack. Breaches of the prohibited AI practices in Article 5 carry the highest tier: up to €35 million or 7% of global annual turnover for the previous financial year, whichever is higher. Non-compliance with most operator obligations (provider duties such as data governance, deployer duties, transparency) carries up to €15 million or 3% of global annual turnover. GPAI model providers face the same ceiling under Article 101.
Supplying incorrect, incomplete, or misleading information to notified bodies or national competent authorities carries up to €7.5 million or 1% of global annual turnover. SMEs and start-ups face the lower of the two values rather than the higher. National authorities and the EU AI Office consider the gravity, duration, intentional or negligent character, cooperation, and prior infringements when calibrating fines.
Does the EU AI Act apply to US companies?
Yes, the regulation has extraterritorial reach. It applies to providers placing AI systems on the EU market or putting them into service in the Union, regardless of where the provider is established. It applies to deployers established in the EU. It also applies to providers and deployers established outside the EU when the output produced by the AI system is used in the Union.
That last hook captures a large slice of the global AI economy: a US-based SaaS vendor whose AI feature is used by a French customer is in scope, and a US-based deployer whose AI output is delivered to or relied on inside the EU is in scope. Non-EU providers must designate an authorised representative in the Union before placing high-risk AI systems on the market.
What is the timeline for full EU AI Act applicability?
The regulation entered into force on 1 August 2024 and applies in stages. On 2 February 2025 the prohibited practices in Article 5 and the Article 4 AI literacy duty became applicable. On 2 August 2025 the General-Purpose AI model rules, the governance chapter (including the EU AI Office and national competent authorities), and the Article 99 penalty regime became applicable.
The Digital Omnibus on AI, Regulation (EU) 2026/1744, entered into force on 27 July 2026 and moved the dates still ahead. The Article 50 transparency duties and most remaining provisions applied on 2 August 2026, the high-risk obligations for Annex III systems apply from 2 December 2027, and high-risk AI embedded in products under Annex I follows on 2 August 2028. Organisations should sequence their compliance programme against these dates, with Article 4 literacy and prohibited-practice screening as the immediate priorities.