Application Security Training that developers finish by writing the fix
Secure coding training your developers finish by writing the fix. They break a deliberately vulnerable app, then fix the code that let them in. OWASP Top 10 for web and APIs, plus Git, Docker and cloud.
Try it yourself. No sign-up needed.
The exploit
A single quote in a lookup form empties the customer table.
The fix
Bind user input as a parameter and the quote stays data, never code.
The exploit
Change one id in the path and the API hands over another rider’s trips.
The fix
Authentication proves who is calling. Only an owner check proves they may.
The exploit
The key is gone from HEAD and still live three commits back.
The fix
Rotate the credential first. A history rewrite alone does not un-leak it.
The exploit
Anyone who can pull the image can read the layer that built it.
The fix
A BuildKit secret mount lets the build read a value it never stores.
The exploit
A support note names the bucket, and the bucket answers anonymously.
The fix
Block public access, then let one named reader through the front door.
Animated preview. The exercise itself runs in a full simulated workstation.
Trusted by teams at





Founded by the creator of Kontra Application Security Training.
Pick the attack surface your team ships
Each AppSec track is a set of short exercises in a simulated workstation. Start with one, or assign the whole track to a team.
Training that starts at the failed scan
Our GitLab CI/CD component reads SAST, Secret Detection, Dependency Scanning and Container Scanning reports in the merge request pipeline. Each finding is matched by its CWE to a short lesson for the developer who wrote the code.
See the GitLab setupLessons can also be assigned from Jira Service Management tickets, PagerDuty incidents and Datadog detections.
-
- build
- test
- sast
- deploy
-
CWE-89 SQL injection · src/orders.ts:42 -
A lesson matched to this finding: SQL Injection, about 7 minutes.
-
Lesson completed. Recorded on this merge request.
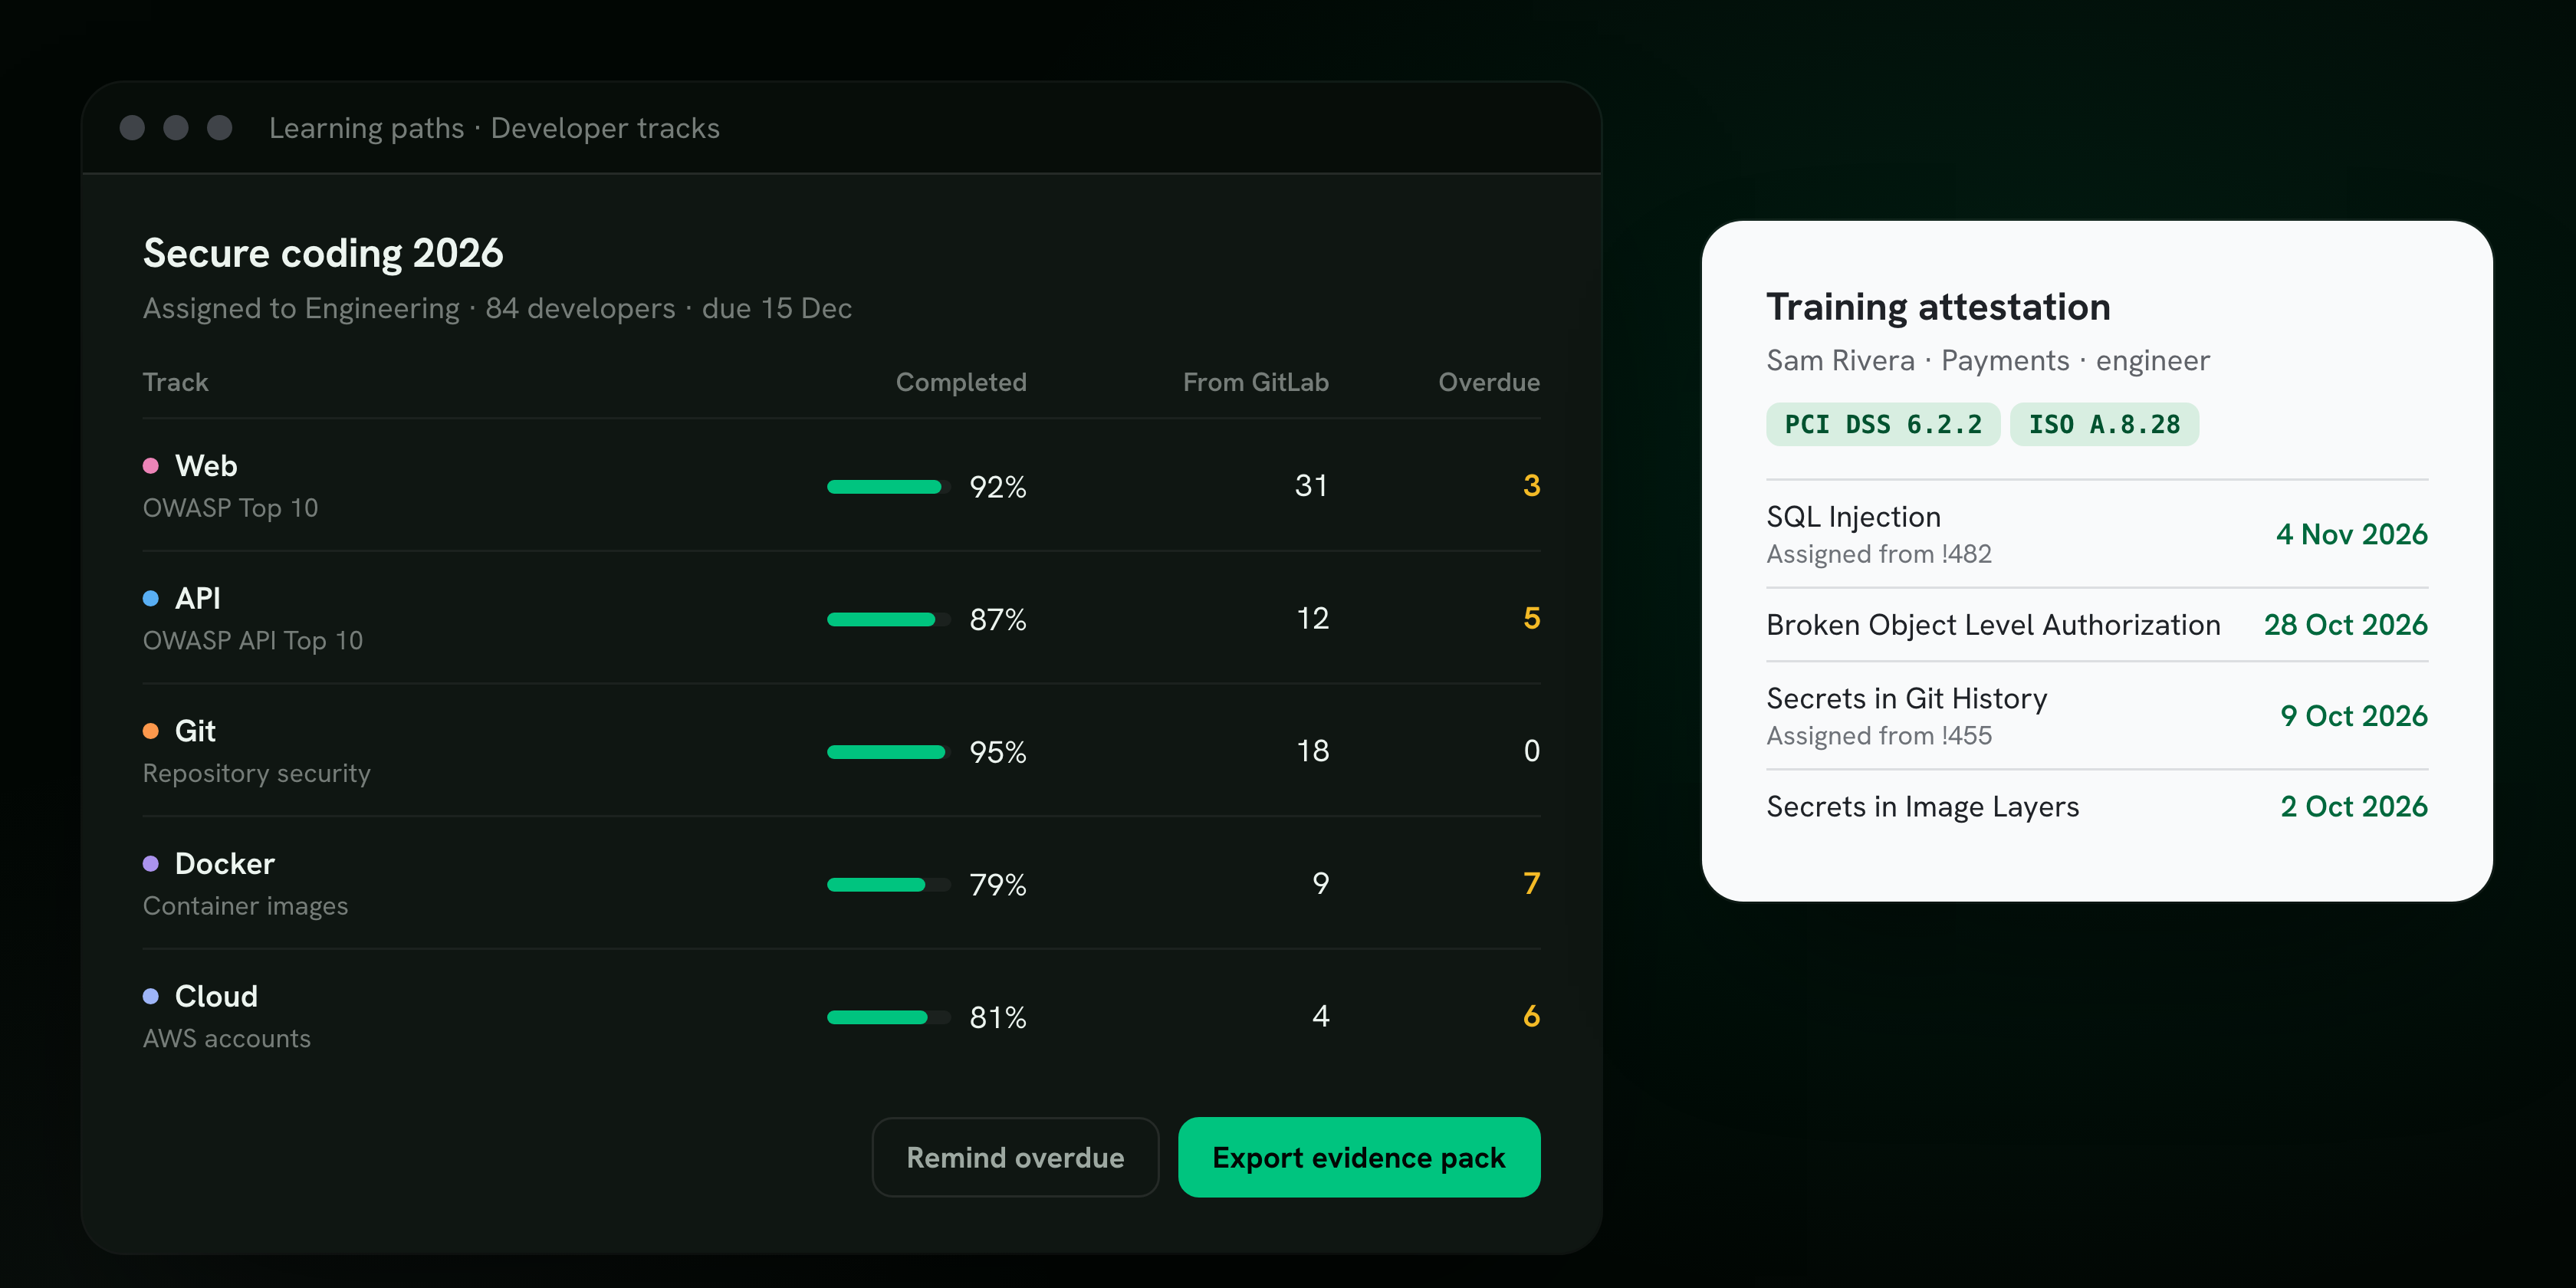
See who finished and who is overdue
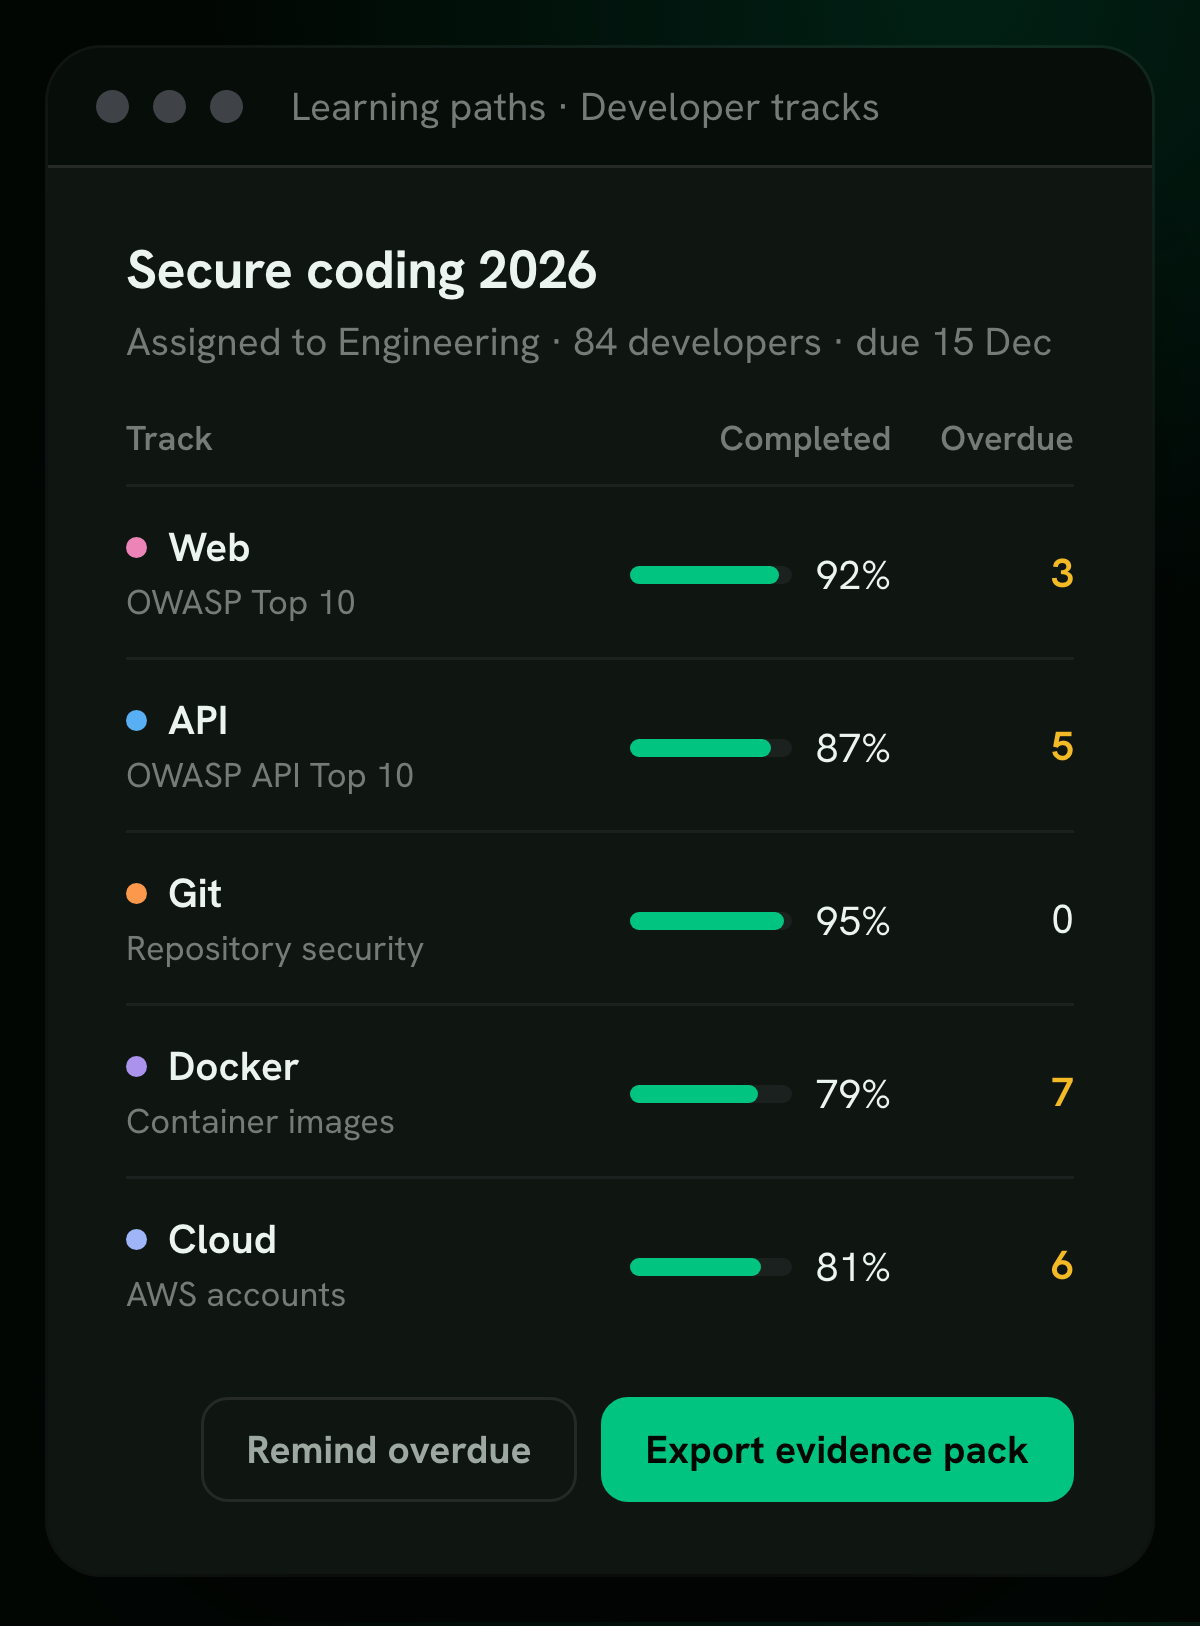
Assign a track to a team with a due date. The console shows completion per track and per developer, which lessons came from GitLab findings, and exports per-developer evidence for PCI DSS and ISO 27001.
Covers the languages your team ships in
The vulnerable code and its fix are shown in the language your developers work in every day.
- JavaScript
- TypeScript
- Java
- C#
- Python
- Scala
- PHP
- Ruby
- Go
- Kotlin
Developers and everyone else, on one platform
Most companies buy developer training from one vendor and security awareness from another. RansomLeak runs both, with one contract, one admin console and one audit trail.
Your developers
- Exploit-and-fix tracks for web, API, Git, Docker and cloud
- Lessons assigned from GitLab scan findings
- Evidence for PCI DSS 6.2.2 secure-coding training
Everyone else
- Interactive 3D security awareness exercises
- Phishing and smishing simulations
- Privacy, compliance and AI security courses
Shared by both
- SSO and SCIM provisioning
- SCORM and LTI 1.3, or our cloud LMS
- Completion evidence synced to Vanta and Drata
Run the first exploit yourself
It takes a few minutes and no sign-up. When your team is ready, we will set up the tracks you need.
Questions engineering leaders ask
What is application security training?
Training that teaches developers to find and fix vulnerabilities in the code they ship. On RansomLeak every exercise is hands-on: you exploit a bug in a deliberately vulnerable app, then write the fix and watch the attack fail.
Most exercises take 5 to 10 minutes. Tracks cover the OWASP Top 10 for web apps and APIs, plus Git repositories, Docker images and cloud accounts.
Is this secure development training for the whole SDLC?
Yes. The tracks follow code from the repository to production: Git for secrets and branch protection, web and API for the code itself, Docker for images and cloud for the account it runs in.
Our GitLab CI/CD component adds the pipeline step. A SAST, secret, dependency or container finding on a merge request assigns the matching lesson to the developer who wrote the code.
Which languages do the exercises support?
The web track shows the vulnerable code and its fix in JavaScript, TypeScript, Java, C#, Python, Scala, PHP, Ruby, Go and Kotlin. Each developer picks the language they work in every day.
Do developers need to install anything?
No. Every exercise runs in the browser inside a simulated workstation, with the vulnerable app, the attacker tools and the editor already set up. Nothing touches your own systems.
Can lessons be assigned automatically?
Yes. From code, our GitLab CI/CD component turns SAST, Secret Detection, Dependency Scanning and Container Scanning findings into a matched lesson on the merge request. GitHub and Bitbucket are not supported yet.
Outside code, a Jira Service Management or Freshservice ticket, a PagerDuty incident or a Datadog detection can assign a lesson, as can Tines, Cortex XSOAR and Cisco XDR playbooks.
Does it cover PCI DSS 6.2.2 and ISO 27001 secure-coding requirements?
Yes. Completion is tracked per developer and exported in audit-ready reports, and the evidence can sync to Vanta and Drata. See the compliance mapping for how exercises map to each framework.
Can we deliver it through our own LMS?
Yes. Exercises ship as SCORM 1.2 and 2004 packages or an LTI 1.3 launch, so they work in Moodle, Canvas, Cornerstone, Workday and most other LMSs. You can also run them on the RansomLeak cloud LMS with SSO.