Skip to content

Blog

AWS Cloud Security Misconfigurations to Fix First
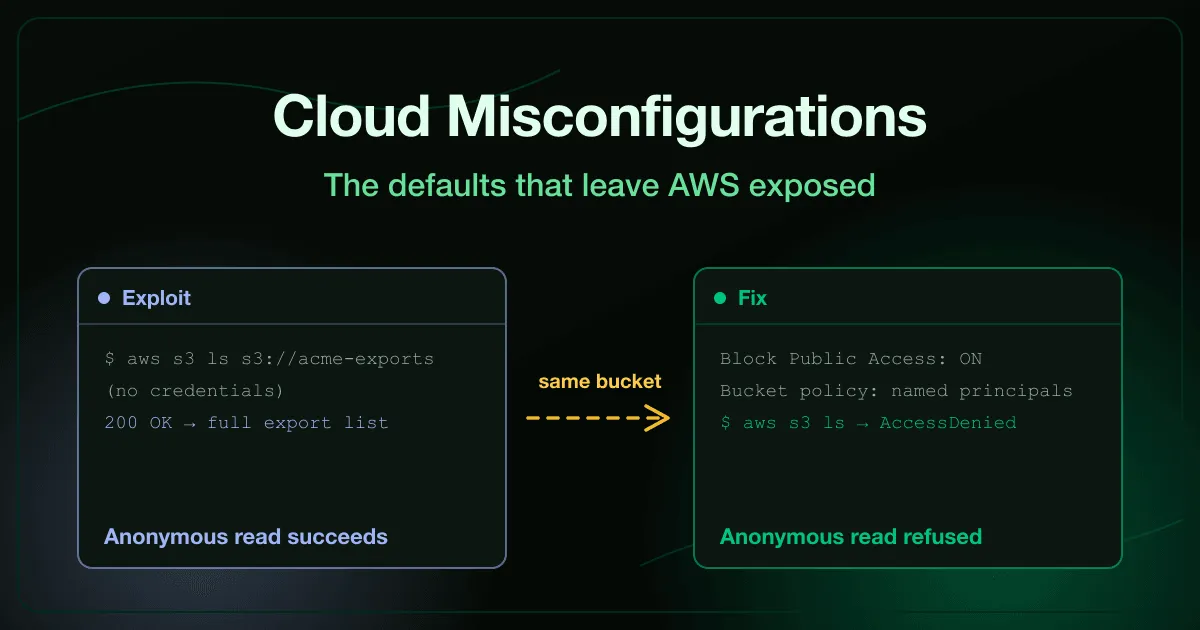
AWS cloud security misconfigurations shown as an anonymous request listing a public storage bucket next to the account-level block-public-access fix that refuses it

A support page told customers to allowlist a storage hostname so their downloads would work. Nobody thought twice about publishing that hostname, because knowing a name is not the same as having access to it.

Except it was. Asking that hostname for a listing worked from an ordinary browser with no credential offered and none required, and next to the folder the company meant to publish sat one nobody did, full of client records.

Nothing about that bucket was exploited in the traditional sense. A permission that AWS makes off by default was switched on at some point, by someone, for a reason that made sense at the time, and it stayed on because nothing about a misconfigured setting looks different from a correct one until someone asks it the right question.
AWS IAM Best Practices to Stop Privilege Escalation

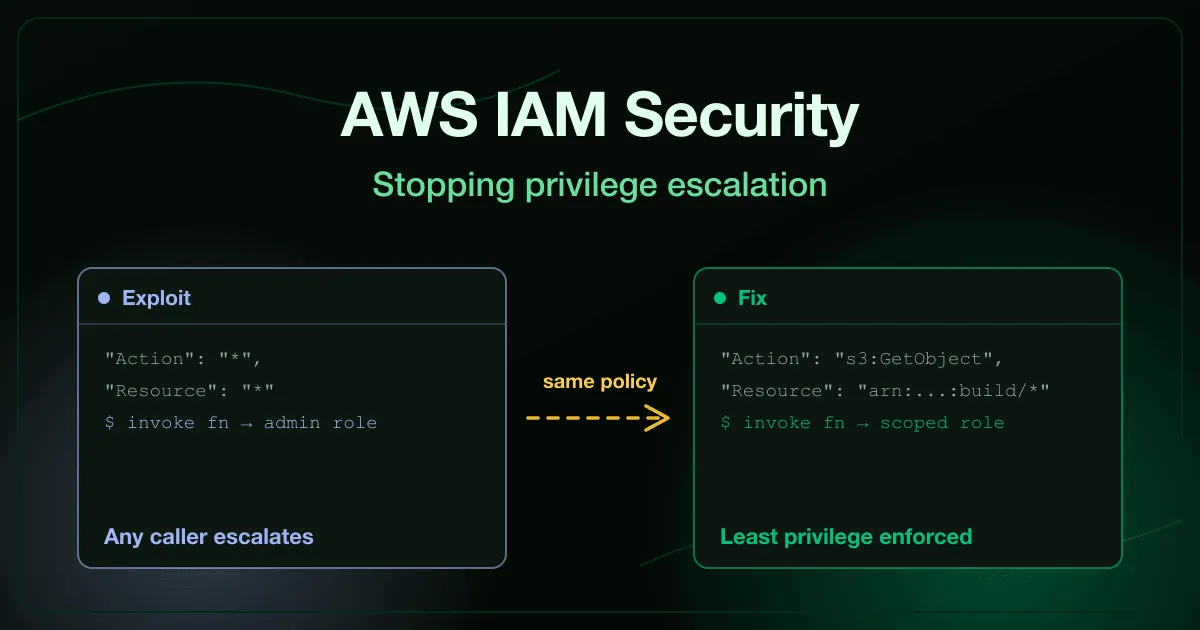
AWS IAM security shown as a wildcard policy escalating through role-passing next to the scoped policy and permission boundary that stops it

A build agent’s credential should be able to upload artifacts and read its own configuration. Nothing more. On paper that is a short, auditable list.

In practice the policy attached to it often reads "Action": "*", "Resource": "*", because a wildcard was close enough to what the pipeline needed and nobody came back to narrow it. That credential is now an administrator wearing a boring name, and the person who granted it never has to know.

The attacker who finds it does not need to hold the privileged role directly. They only need to pass it to something that will run with it, which is why this class of failure survives a policy review that only checks who holds the admin role.

API Security Best Practices: OWASP API Top 10 in Practice

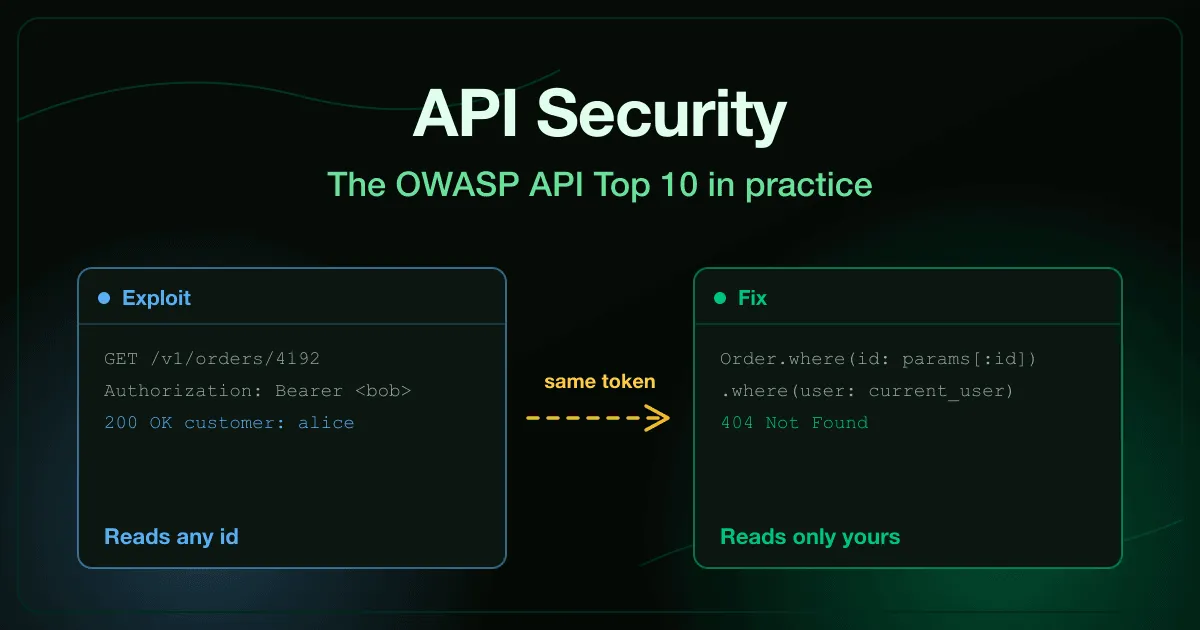
API security best practices illustrated by a request that swaps one object id and returns another customer record, next to the ownership check that rejects it

A developer builds an endpoint that returns a customer’s order. It checks the session token, loads the order by the id in the URL, and returns it. Every test passes, code review approves it, and the API ships.

Nothing in that flow asks whether the order belongs to the caller. Change one digit in the id and the endpoint hands over someone else’s record, because it was never told not to.

That single missing comparison is API1 in the OWASP API Security Top 10, and it remains the most common way real APIs leak data. It also shows why API security best practices read differently from web application ones.

The vulnerability is not a payload, an encoding bug, or a missing header. It is a business rule nobody wrote down.

Container Security Best Practices for Images and Runtime

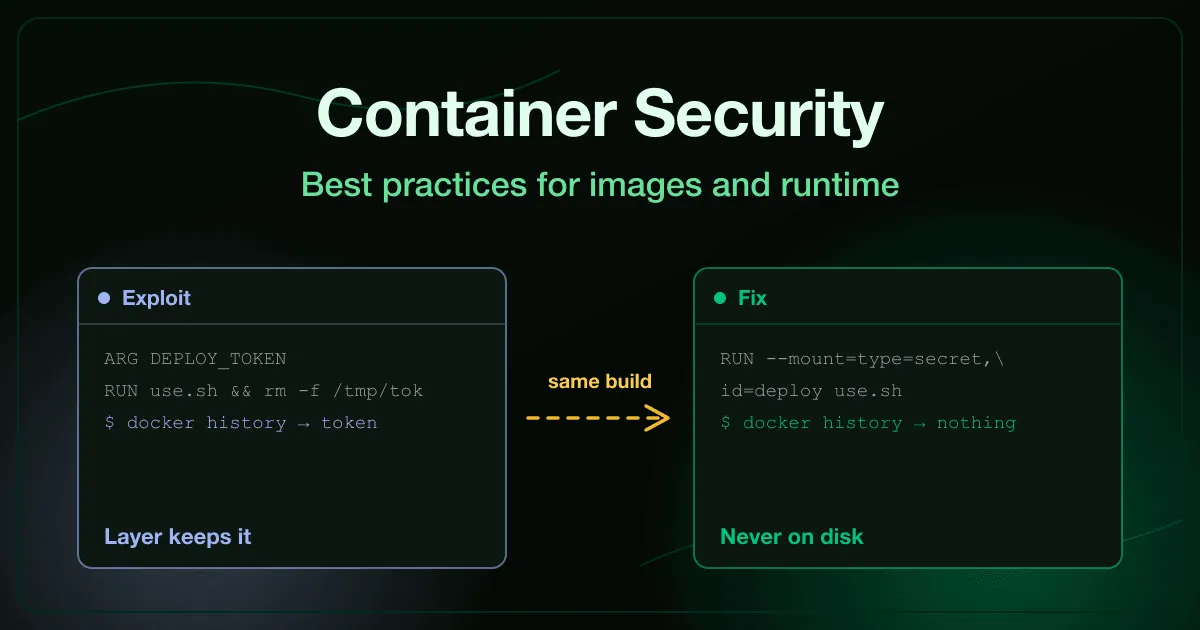
Container security best practices shown as an image layer holding a live credential next to the hardened multi-stage build that never writes it to disk

A build passes a deployment token into a RUN step, uses it, and deletes the file on the next line. The Dockerfile looks careful. The image is published to a public registry.

Image layers are append-only, so the delete did not remove anything. It stacked a new layer on top of the one still holding the token, and docker history reads it back in a single command.

That gap between what the Dockerfile appears to do and what the image actually contains is where most container security work lives. The runtime has a matching version of the same problem, where a flag added to make a container work in staging quietly hands it the host.

Best Secure Coding Training Platforms for 2026

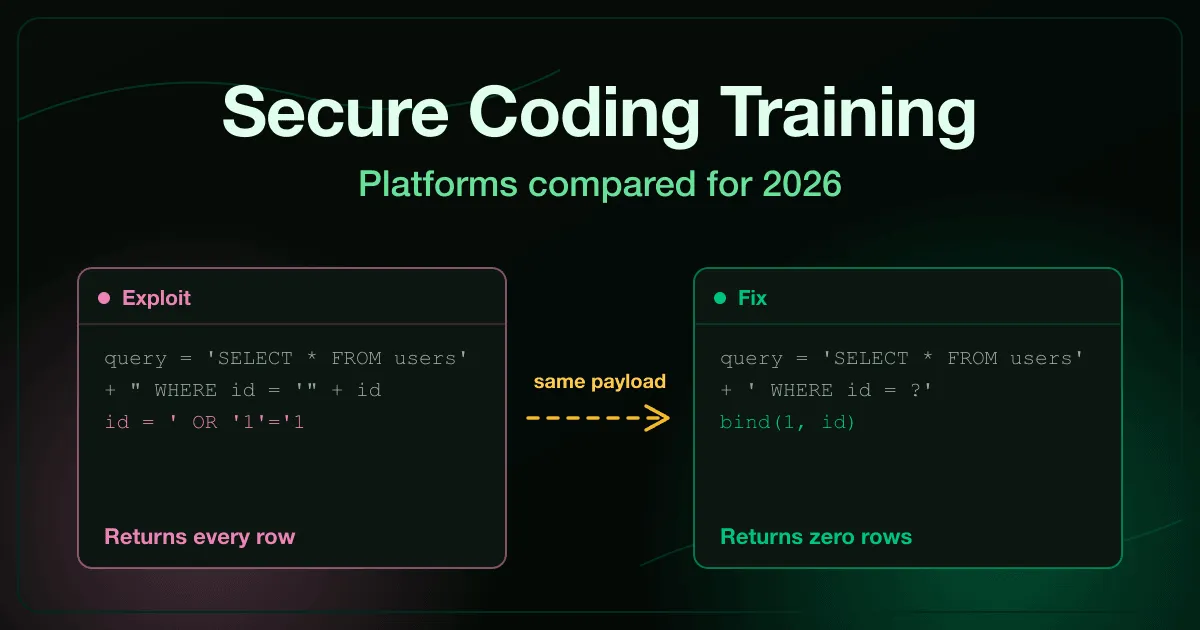
Secure coding training platforms compared for 2026 - a SQL injection payload returning every row against vulnerable code and zero rows against the parameterized fix

The best secure coding training platform in 2026 depends on how your developers learn and how wide your stack runs. Secure Code Warrior leads on language breadth and enterprise benchmarking. Veracode Security Labs fits teams already standardized on Veracode scanning. RansomLeak wins on exploit-then-fix depth across web, API, Git, cloud, mobile, and frontend. This roundup compares eight application security training vendors with a transparent methodology.

Updated August 2026.