Skip to content

appsec

2 posts with the tag “appsec”

API Security Best Practices: OWASP API Top 10 in Practice
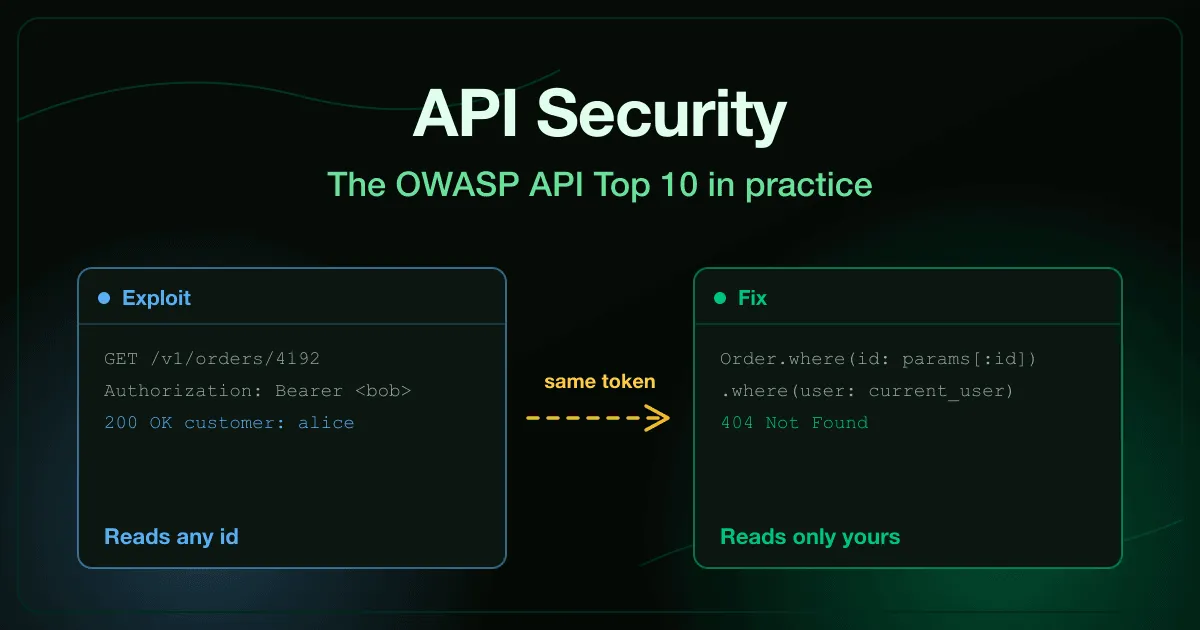
API security best practices illustrated by a request that swaps one object id and returns another customer record, next to the ownership check that rejects it

A developer builds an endpoint that returns a customer’s order. It checks the session token, loads the order by the id in the URL, and returns it. Every test passes, code review approves it, and the API ships.

Nothing in that flow asks whether the order belongs to the caller. Change one digit in the id and the endpoint hands over someone else’s record, because it was never told not to.

That single missing comparison is API1 in the OWASP API Security Top 10, and it remains the most common way real APIs leak data. It also shows why API security best practices read differently from web application ones.

The vulnerability is not a payload, an encoding bug, or a missing header. It is a business rule nobody wrote down.
Best Secure Coding Training Platforms for 2026

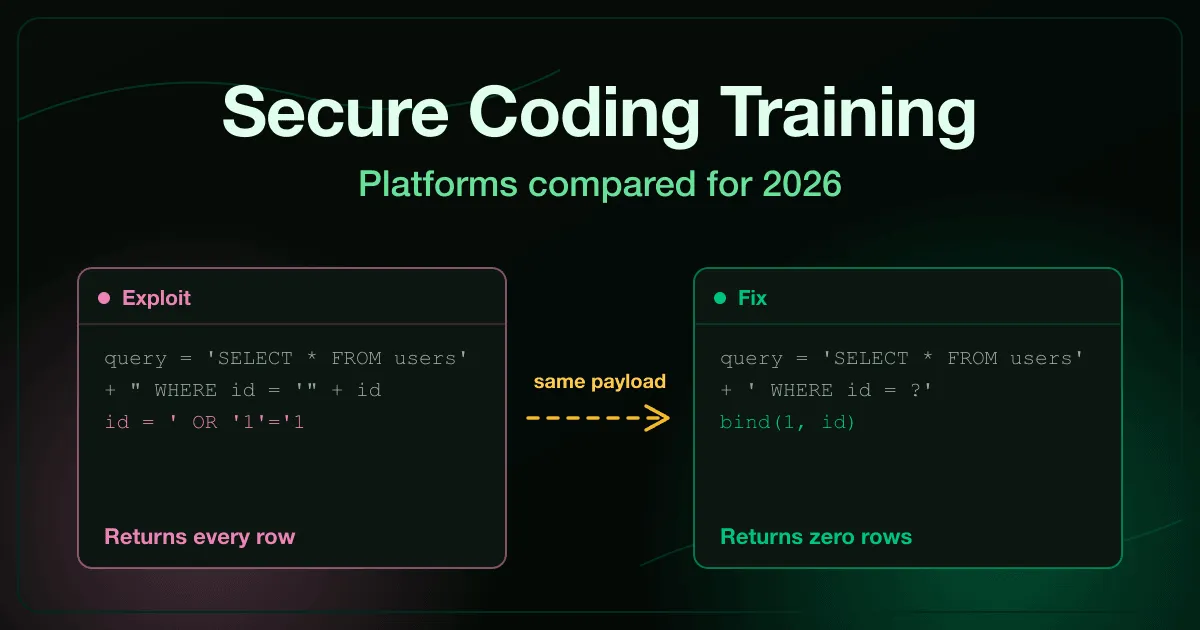
Secure coding training platforms compared for 2026 - a SQL injection payload returning every row against vulnerable code and zero rows against the parameterized fix

The best secure coding training platform in 2026 depends on how your developers learn and how wide your stack runs. Secure Code Warrior leads on language breadth and enterprise benchmarking. Veracode Security Labs fits teams already standardized on Veracode scanning. RansomLeak wins on exploit-then-fix depth across web, API, Git, cloud, mobile, and frontend. This roundup compares eight application security training vendors with a transparent methodology.

Updated August 2026.