Skip to content

eu ai act

7 posts with the tag “eu ai act”

AI in Recruitment: Bias, Fake Candidates, and the Law
AI in recruitment illustrated as a candidate video call where half of the face breaks into a synthetic grid, next to a ranked shortlist with one flagged row

A recruiter runs 400 applications for a remote developer role through an AI shortlister, then books three video interviews. The top candidate interviews well, clears the background check, and asks for the laptop to go to a new address.

Two of those steps involved AI, and both can fail in ways the recruiter never sees. The shortlister may have dropped qualified people for reasons nobody chose, and the person on camera may not be the person on the documents.
AI Literacy Training: Meeting EU AI Act Article 4

AI literacy training under EU AI Act Article 4 shown as an open book and brain with a checkmark inside a circle of EU stars

Most of the EU AI Act applies to a narrow set of high-risk systems. Article 4 is the exception, because it reaches every organization that builds or uses AI, no matter how harmless the tool looks.

It has applied since 2 February 2025, well ahead of the high-risk obligations, which the Digital Omnibus pushed back to December 2027. So while teams plan for the heavier duties, the literacy clause is already live.

Deepfakes and the EU AI Act: Article 50 Transparency

EU AI Act deepfakes shown as a face split between a real photo and a synthetic wireframe with an Article 50 label tag inside a circle of EU stars

The EU AI Act does not ban deepfakes. It treats them as a transparency problem, so the duty is not to stop synthetic media but to make sure people know when content is artificial.

That duty lives in Article 50, and it splits the responsibility between the company that builds the generation tool and the company that publishes the result. Getting the split wrong is how a marketing clip or a training video turns into a compliance gap.

EU AI Act and GDPR: Where the Two Laws Overlap

EU AI Act and GDPR shown as two interlocking rings sharing a common core inside a circle of EU stars

Teams often treat the EU AI Act as a brand new rulebook that lands on a clean desk. It does not. If your AI system touches personal data, GDPR was already on that desk, and the AI Act stacks on top of it.

That stacking is where most of the confusion lives. The same project can owe a Data Protection Impact Assessment under one law and a Fundamental Rights Impact Assessment under the other, and nobody wants to run two parallel compliance tracks if one mapped program will do.

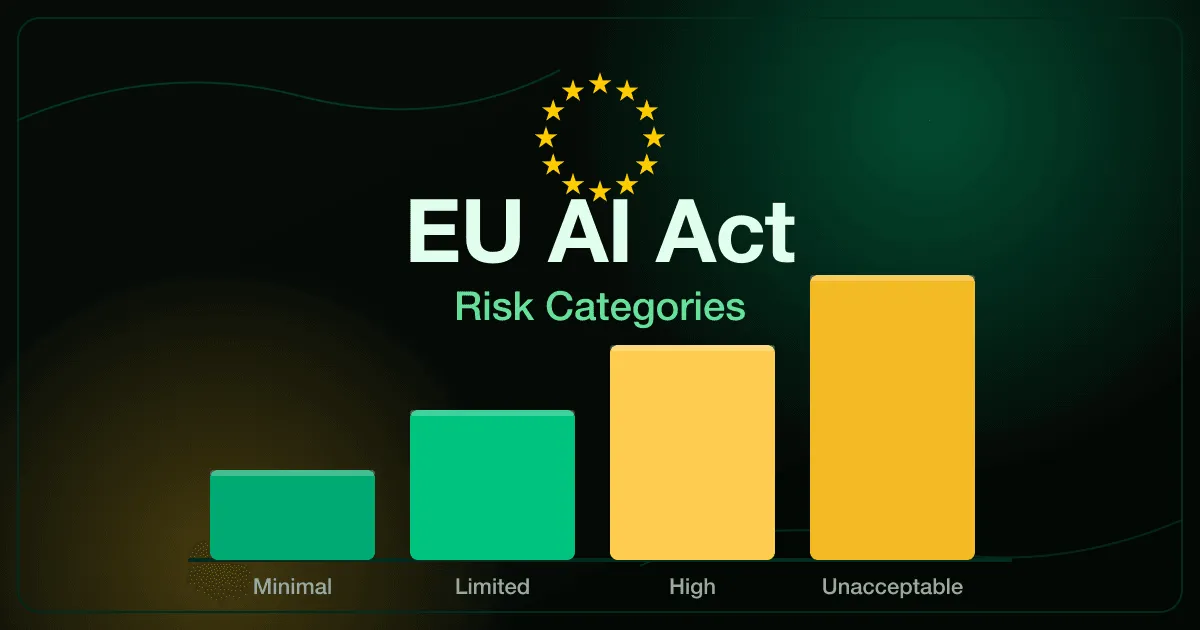
EU AI Act Risk Categories: The 4 Levels Explained

EU AI Act risk categories shown as a four-level pyramid from minimal to unacceptable risk inside a circle of EU stars

The EU AI Act does not treat every AI system the same way. It uses a risk-based design, so the obligations on a spam filter look nothing like the obligations on a CV-screening tool or a credit-scoring model.

That single decision, which risk category your system falls into, drives almost everything else: the controls you owe, the documentation you keep, and the size of the fine if you get it wrong.

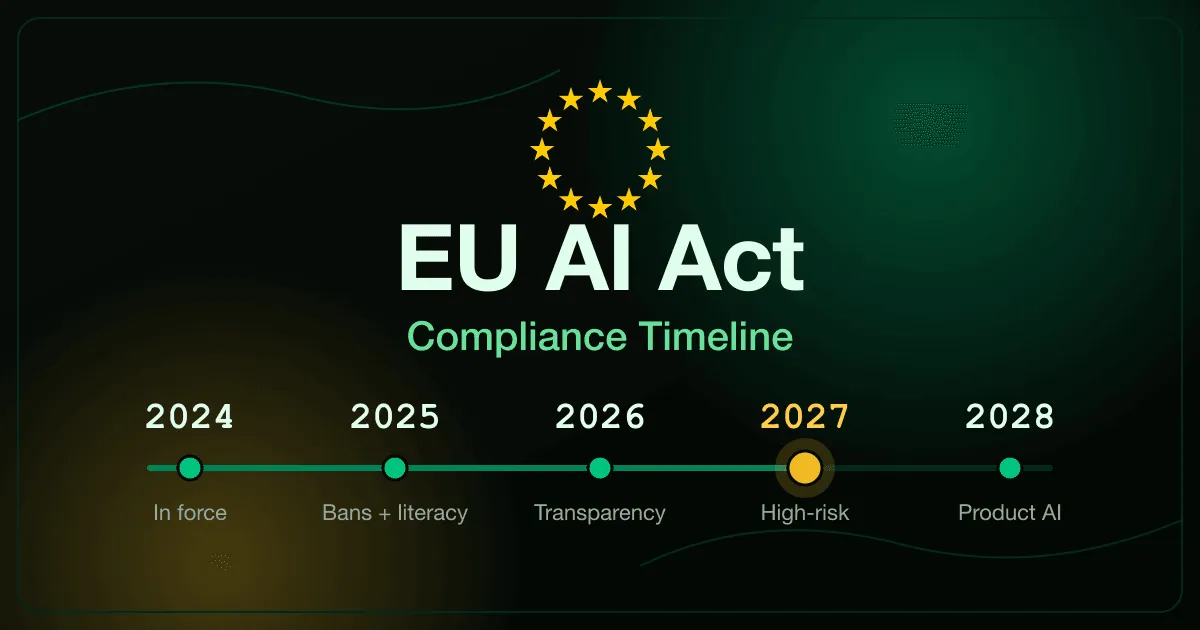
EU AI Act Timeline: Compliance Deadlines to 2028

EU AI Act compliance timeline showing the staged deadlines from 2024 to 2028, with the high-risk regime in December 2027, under a circle of EU stars

The EU AI Act does not arrive on a single date. It applies in stages between 2024 and 2028, and each stage switches on a different set of obligations for the organizations that build or use AI systems in Europe.

The schedule also moved. The Digital Omnibus on AI, in force since 27 July 2026, pushed the high-risk regime for Annex III systems back to 2 December 2027, which gives most compliance teams extra runway while the obligations themselves still arrive.

Compliance Training That Passes Audits

Compliance training - security shield with checkmarks representing regulatory compliance

Regulatory compliance is not optional. If you handle healthcare data, process payments, or serve European customers, specific frameworks mandate how you protect information. Security awareness training sits at the center of nearly every one of those requirements.

And yet most organizations treat compliance training as a checkbox exercise. Annual videos. Generic quizzes. Certificates that prove nothing except attendance. I’ve watched this pattern repeat for years, and it fails both the spirit and the letter of what regulators actually expect.

The organizations that get this right do something different. They build training that satisfies auditors and creates employees who understand why regulations exist, how their daily actions either protect or expose sensitive data, and what to do when something looks wrong.