Secrets in Git and CI/CD: Why Deleted Keys Still Work
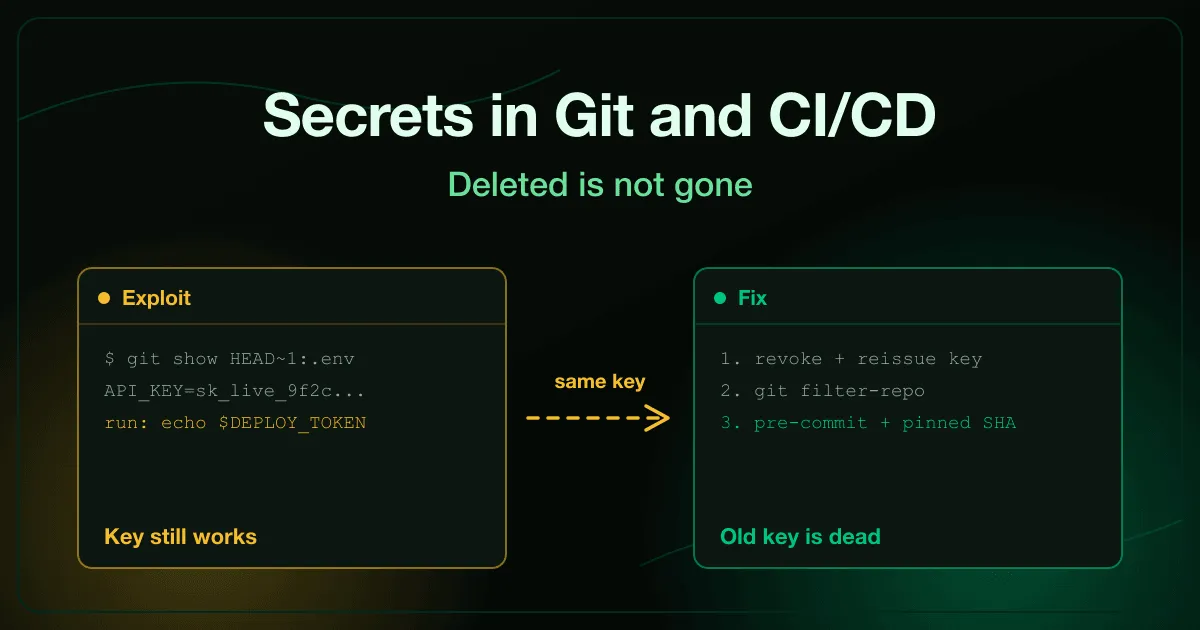
A leaked secret in Git or CI/CD is any credential, such as an API key, deploy token or private key, that ends up in a repository’s history, a tracked file or a build log. Deleting it from the latest commit does not revoke it. Anyone with a clone or log access can still read and use it until the credential itself is rotated.
This post covers the four places secrets leak in a delivery pipeline, the order to fix them in, and the guardrails that stop the next one.