Skip to content

patch management

2 posts with the tag “patch management”

PHP2Shell: How One Request Became RCE, and the Fix
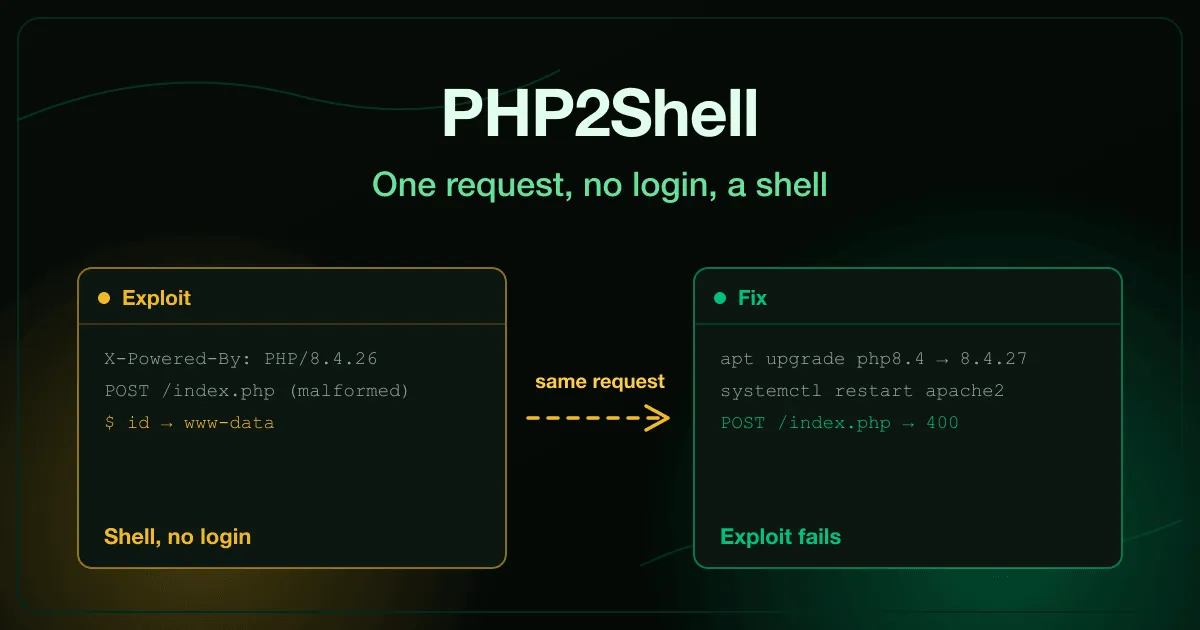
PHP2Shell remote code execution explained: an unauthenticated request runs a shell on PHP 8.4.26, then fails after updating to 8.4.27 and restarting Apache

PHP2Shell is the nickname for two critical PHP runtime flaws, CVE-2026-109618 and CVE-2026-109619, disclosed in October 2026. Together they let an attacker run commands on a web server with one malformed request and no login. Exploitation started on 17 October, four days before PHP shipped fixes on 21 October.

This post walks the attack chain, the response that actually closes it, and the cleanup that patching alone never does. Everything here mirrors our free PHP2Shell RCE exercise, where you play both the attacker and the engineer on call.
Zero-Day Patch Management: Installed Is Not Running

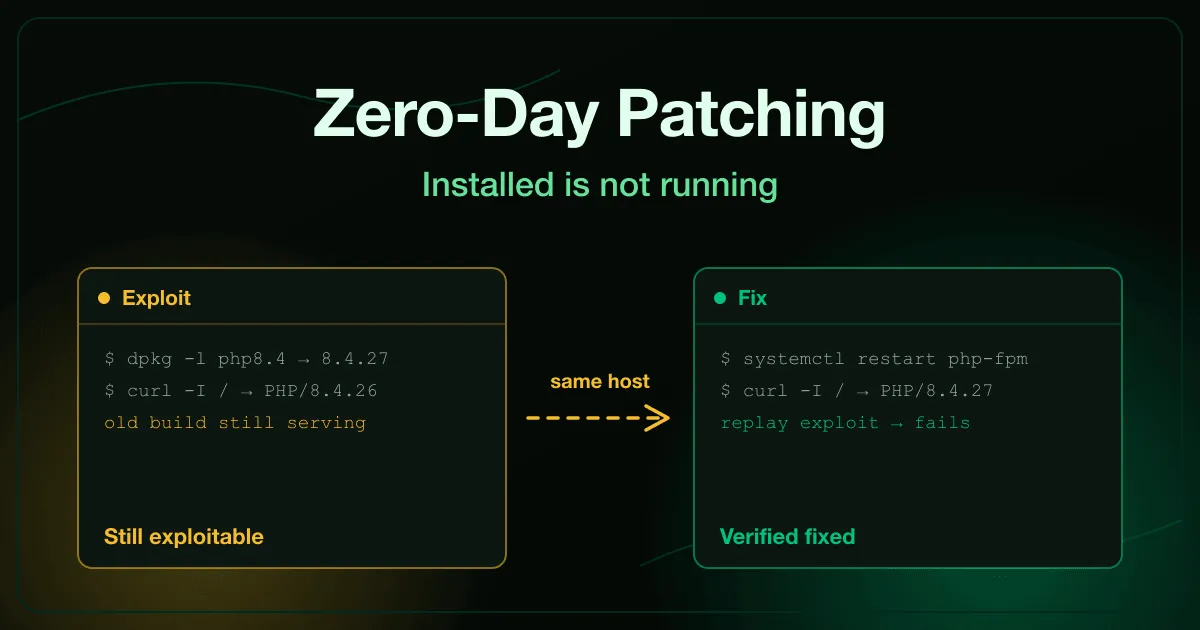
Zero-day patch management: the package manager reports PHP 8.4.27 while the server still serves 8.4.26, until a restart loads the fixed build and the exploit fails

Zero-day patch management is the process of closing a vulnerability that attackers are already exploiting, often before or within hours of a vendor fix. It covers four steps: install the fixed build, make sure the running service actually loads it, verify the exploit fails, and clean up anything the attacker reached while the hole was open.

Most teams are good at the first step. The other three are where incidents keep happening.