HTTP2Shell: How a Brotli Flaw Became RCE, and the Fix
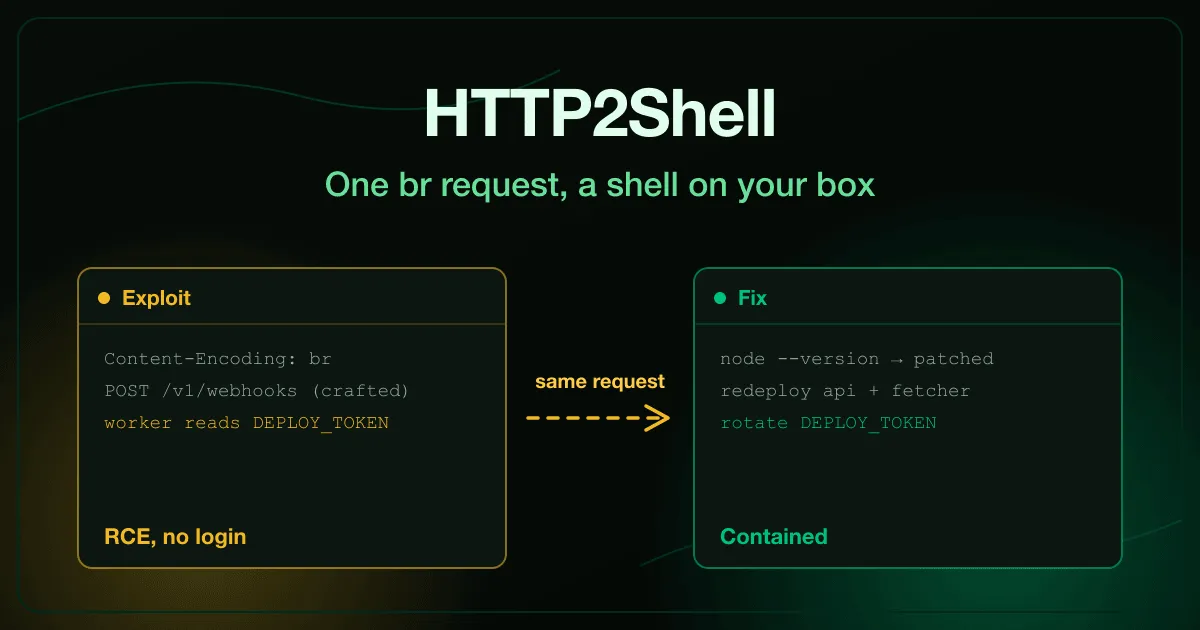
HTTP2Shell, also called Node2Shell, is the nickname for CVE-2026-111497, an out-of-bounds write in Google’s Brotli decompression library. Fixes shipped on 21 October 2026. Any service that automatically decodes Content-Encoding: br traffic can be pushed into corrupting its own memory, and from there into running attacker commands.
This post walks the attack chain and the response that actually contains it. Everything here mirrors our free HTTP2Shell RCE exercise, where you play both the attacker and the platform engineer on call.